After nearly a decade of federal departments and agencies routinely failing to meet mandatory cyber security standards, the federal government will scrap its foundational Essential Eight framework in favour of a new principles-based standard.
Subscribe now for unlimited access.
or signup to continue reading
Save $100 + Bonus Tote
All articles from our website
& app
The digital version of
Today's
Paper
Crosswords, Sudoku and Trivia
All other
in your area
Cyber Security Minister Tony Burke announced the new ASD Essentials, developed by the Australian Signals Directorate (ASD).
The new standard establishes guidance across three core areas: enterprise information technology (IT), cloud environments and operational technology. It will also include specific advice to help organisations manage artificial intelligence in their networks.
Under ASD Essentials, agencies will also face a different accountability regime.
Rather than relying on self-assessed checklists, departments will be judged area-by-area on effectiveness ratings backed by independent testing and simulated exercises, with the framework mandating explicit executive-level accountability for cyber risks.
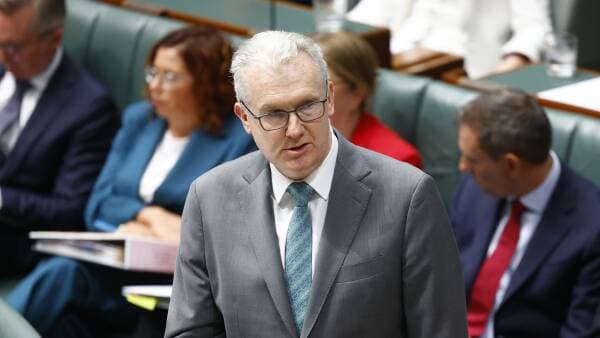
Minister for Cyber Security Tony Burke. Picture by Keegan Carroll
The urgency of the reset comes as the public service cemented its place as the primary target for malicious cyber actors.
The ASD's 2024-25 Annual Cyber Threat Report showed the federal government was the most targeted sector in the nation, accounting for nearly one third (32 per cent) of all cyber security incidents responded to by the cyber security agency.
Over that period, the ASD responded to more than 1200 incidents, an 11 per cent increase. Notifications of malicious cyber activity had surged by 83 per cent to more than 1700, and threat alerts issued to critical infrastructure spiked by 111 per cent.
While the new standards will officially take effect over the next year or two, under the outgoing Essential Eight framework, agencies were rated from Maturity Level 0 to 3. It was the benchmark used to measure whether departments could withstand targeted attacks by sophisticated adversaries.
Instead, the ASD's own Commonwealth Cyber Security Posture in 2025 report revealed a systemic compliance crisis. It found 78 per cent of agencies failed to meet the mandatory Maturity Level 2 baseline across all eight threat mitigation strategies, despite the requirement being in place under the mandatory Protective Security Policy Framework (PSPF) since July 2022.
Mr Burke said the accelerating pace of cyber threats meant Australian organisations needed workable guidance that matched the growing complexity of digital networks.
"The ASD Essentials give organisations a clear roadmap for strengthening their cyber security, helping leaders understand what matters most, where to focus their efforts, and how to build online resilience," Mr Burke said.
"Cyber resilience is not achieved through technology alone. ASD Essentials gives organisations the tools to strengthen their human firewall by instilling a greater security culture amongst workers."
It also found the department operated an unsegmented network on ageing platforms, relied on unverified compensating controls, and ran critical parliamentary systems under expired risk approvals.
The failure to maintain basic cyber security hygiene mirrored a decade-long pattern.
A 2021 cross-agency audit found a number of departments had not fully complied with mandatory cyber controls.
Head of the Australian Cyber Security Centre Stephanie Crowe said the rapidly changing threat landscape meant critical infrastructure operators and large organisations needed to act to embed greater resilience across their networks.
"Good cyber security does not have to be complicated", Ms Crowe said.
"The ASD Essentials provides practical, prioritised guidance that Australian organisations can use to reduce risk, protect critical systems and strengthen their defences against real-world threats."
Ms Crowe also said the new framework built on the foundations of the Essential Eight to ensure prior work done continued "to deliver value while driving strong cyber resilience".
The ASD's 2025 posture review also found some of the roadblocks to building cyber capacity for departments were structural and financial.
Nearly 60 per cent of agencies reported aging legacy systems were crippling their ability to deploy basic security controls.
A lack of dedicated funding was cited a key obstacle for more than a third of agencies, more so than software availability and cyber workforce shortages.
More from National News

As it happens
Breaking news alert
Be the first to know when news breaks.