Everspin, an artificial intelligence cybersecurity company, said on the 22nd that it has applied blocking rules to clients of its web security solution Eversafe for Web to stop attacks targeting the programming language PHP.
PHP is a development language used in a wide range of web services, including corporate websites, content management systems and e-commerce platforms. Two vulnerabilities were recently found in PHP: improper handling of exceptional conditions (CVE-2026-109618) and use-after-free (CVE-2026-109619).
The vulnerabilities can lead to remote code execution, which allows commands to be issued to a server from outside. PHP rated their severity at 9.2 on the Common Vulnerability Scoring System, a critical ranking. After information about the flaws leaked before a patch was available, the PHP security team released an emergency security update on the 21st.
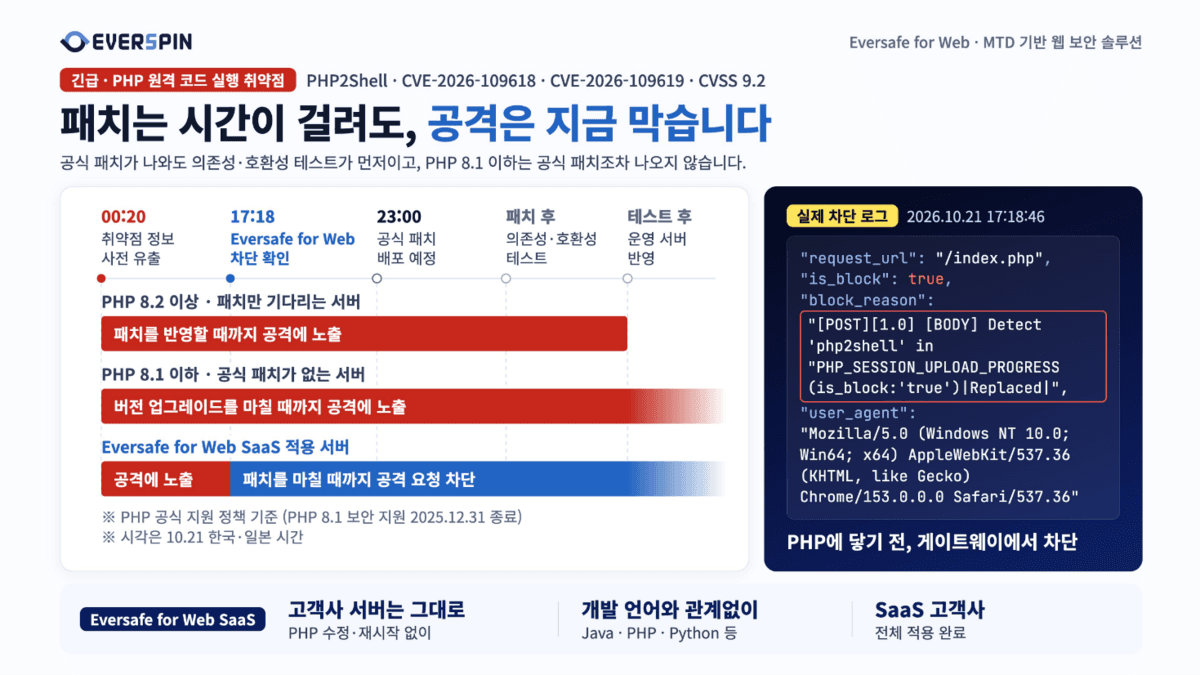
Everspin applied the blocking rules to clients using Eversafe for Web through its cloud service. All deployments were completed before the official patch from the PHP development team was released.
The company said it sent attack requests in a test environment based on publicly available technical analysis and confirmed that the requests were blocked by its vulnerability attack response feature. Attack requests are filtered at the front end before reaching client servers. Everspin said the test verified that a security feature already provided to existing clients can respond immediately to attacks exploiting new vulnerabilities.
Even after a patch is released, applying it to services takes time, because operators must check PHP versions and configurations and examine whether the update affects existing functions. PHP 8.1 and earlier versions, which are no longer supported, receive no official patch and require a version upgrade. That is why reducing exposure to attacks before a patch is applied matters.
Everspin said its vulnerability attack response feature protects client services before a patch is in place. It added that while clients review the scope of impact and apply the update after a patch is released, attacks can be blocked at the front end of the server without modifying or restarting client servers. Removing the vulnerability itself, however, still requires applying the official patch. The feature works regardless of the development language, including Java and PHP.
Everspin plans to expand support for clients running PHP-based services. For services that have found it difficult to use on-premise installations on their own servers, the company is proposing adoption of its cloud service.