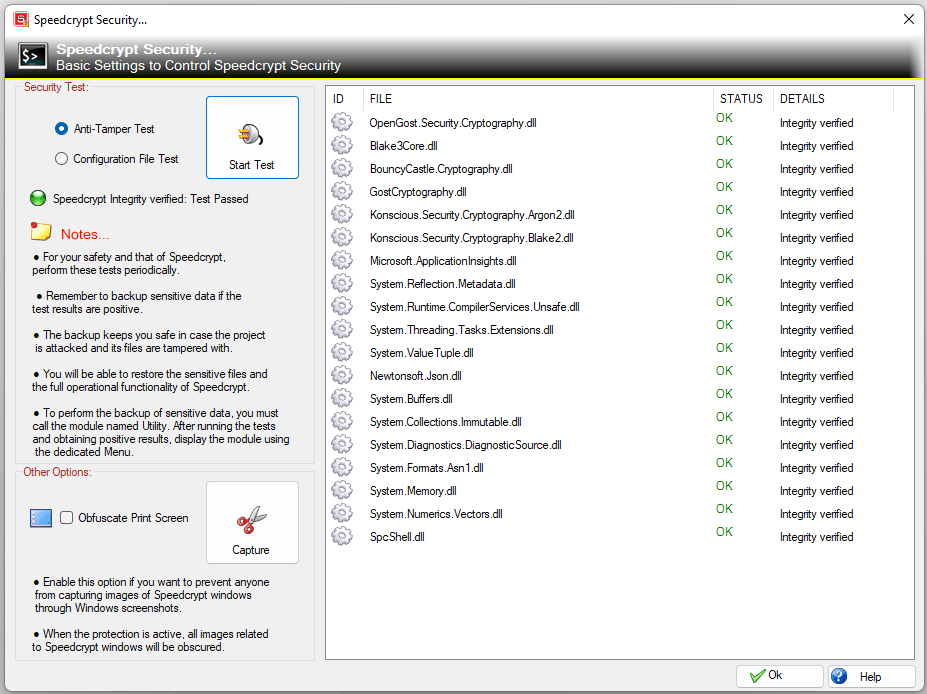
In modern endpoint security, preventing credential theft has historically focused on defeating keyloggers. However, contemporary infostealers and advanced persistent threats (APTs) have evolved. Instead of relying solely on low-level keyboard hooks, modern malware frequently implements continuous, asynchronous screen-scraping loops via graphics APIs like DirectX or GDI.
If a user enters sensitive data via a virtual keyboard or opens a password manager, a host-based surveillance vector can capture the visual buffer at the exact millisecond the plaintext is exposed. Standard user-space protections that attempt to intercept the Print Screen key intercept nothing when malware captures the screen directly from the window graphics pipeline.
To neutralize this threat, defensive software must move beyond input filtering and enforce hardening directly at the Window Manager layer.

The Architectural Solution: Desktop Window Manager Affinity
The most resilient way to thwart visual surveillance on Windows architectures is to instruct the Desktop Window Manager (DWM) to actively omit the application's window from any visual capture loop, video recording, or screen dump.
To demonstrate this paradigm, we will examine the open-source implementation of Speedcrypt, an advanced cryptographic suite built for .NET. Speedcrypt implements a highly specialized, isolated native Win32 bridging class designed to dynamically apply window display affinity with automated fallback mechanics.
Implementing Native Protections via P/Invoke
The core mechanism relies on interfacing directly with user32.dll to change how the OS handles the visual buffer of our application window. Below is the primary P/Invoke binding and constant definitions extracted from the Speedcrypt architecture:
csharp
internal static class SpeedcryptGhost
{
    // Windows API constants
    private const int WDA_NONE = 0;
    private const int WDA_MONITOR = 1;
    private const int WDA_EXCLUDEFROMCAPTURE = 17; // Enables total transparency on Windows 10 2004+

    // P/Invoke with SetLastError to allow GetLastWin32Error.
    [DllImport("user32.dll", SetLastError = true)]
    private static extern bool SetWindowDisplayAffinity(IntPtr hWnd, int dwAffinity);
}
Deconstructing the Constants
While historical implementations relied heavily on WDA_MONITOR (which renders the window as a solid black rectangle in screenshots), modern user experiences require a cleaner approach.
The introduction of WDA_EXCLUDEFROMCAPTURE (value 17) during the Windows 10 2004 update changed the landscape. Instead of displaying an ugly black box that signals to the user (or malware) that a security mechanism is active, it instructs the Desktop Window Manager to completely drop the window from the composited image. The application behind it is revealed, making the target window completely invisible to screen-capture tools while remaining fully functional for the user.
Deterministic Fallback Pipeline
A common flaw in endpoint protection software is assuming the host platform fully supports modern API extensions. If a tool hardcodes WDA_EXCLUDEFROMCAPTURE on an outdated Windows build, the call fails silently or throws an unhandled exception, leaving the application entirely unprotected.
The architecture behind Speedcrypt solves this by implementing a deterministic fallback pipeline. The system proactively probes for modern transparency masking, and instantly drops back to standard black-box monitoring if the host kernel denies the request:
csharp
/// <summary>
/// Internal wrapper to handle fallback logic between transparency and black box masking.
/// </summary>
private static bool ApplyProtection(Form form)
{
    // Try Windows 10 2004+ total transparency mode first
    if (SetAffinityInternal(form, WDA_EXCLUDEFROMCAPTURE))
    {
        return true;
    }

    // Fallback to legacy black rectangle window masking
    return SetAffinityInternal(form, WDA_MONITOR);
}

/// <summary>
/// Internal helper that actually calls the Win32 API and logs results on failure.
/// </summary>
private static bool SetAffinityInternal(Form form, int affinity)
{
    if (form == null || !form.IsHandleCreated)
    {
        return false;
    }

    try
    {
        bool result = SetWindowDisplayAffinity(form.Handle, affinity);
        if (!result)
        {
            int err = Marshal.GetLastWin32Error();
            var ex = new COMException($"SetWindowDisplayAffinity execution failed for affinity: {affinity}.", err);
            CentralLog.LogException(ex, "SpeedcryptGhost", $"SetWindowDisplayAffinity failed. Affinity: {affinity}, Win32Error: {err}. " + ex.Message);
            return false;
        }

        return true;
    }
    catch (Exception ex)
    {
        CentralLog.LogException(ex, "SpeedcryptGhost", "SetAffinityInternal exception occurred: " + ex.Message);
        return false;
    }
}
Conclusion
Securing sensitive visual data cannot rely on high-level user-space hooks that malware can easily subvert. By shifting the defensive perimeter directly to the Windows Desktop Window Manager affinity pipeline, developers can guarantee strong memory-level structural protection against host-based surveillance.
However, in the offensive security landscape, an absolute axiom remains: there is no such thing as an impenetrable defense. While leveraging DWM affinity significantly raises the operational cost for an attacker, it is not a silver bullet. A system compromised at the kernel level or targeted by highly specialized rootkits could still theoretically subvert these architectural boundaries. Endpoint security is a battle of continuous mitigation and introducing strategic friction, rather than achieving absolute, permanent invulnerability.
The implementation analyzed above represents a core layer of the open-source Speedcrypt cryptographic suite. By coupling raw native Win32 performance with deterministic C# fallback handling, it provides a practical blueprint for software architects looking to harden their applications from the ground up, while remaining fully conscious of the evolutionary and adaptive nature of modern threats.
Open Source & Peer Review Invitation
The defensive implementation analyzed in this article is part of Speedcrypt, an open-source cryptographic suite built to test multi-jurisdictional compliance and endpoint resilience.
Because cryptography and system hardening should always be fully transparent, the binaries and full source code are available for public audit. If you are a security researcher, a .NET developer, or a cybersecurity enthusiast, you are highly encouraged to review the Win32 subsystem bindings and test the architecture against localized injection vectors.
- Official Source & Binaries: You can inspect the source architecture and access the portable deployment directly on the Speedcrypt SourceForge Repository:
sourceforge.net - Project Integrity & PGP Signatures: Full SHA-256 checksums and OpenPGP detached signatures for local binary auditing can be verified at the Speedcrypt Integrity Page:
speedcrypt.info