
Shekhar Vaidya is a veteran technology journalist and computer science engineer. He is the founder of TechLatest, where he has spent years providing technical analysis on hardware and Windows ecosystems. Now a Computing Writer at XDA, Shekhar leverages his deep background in NAS, storage solutions, and PC internals to help readers master their tech.
Over the past year, I tested several DNS servers. Every DNS server I tested blocked ads and filtered trackers while I was at home. As soon as I switched from home Wi-Fi to mobile data or public Wi-Fi, ads and trackers returned. As a solution, I exposed AdGuard Home (AGH) as a self-hosted encrypted DNS server. After that, I pointed my phones at it, and now they filter through my own AGH from everywhere. But while setting up AGH for when I was away, I broke it at home.
Every DNS server worked, but CGNAT was the wall
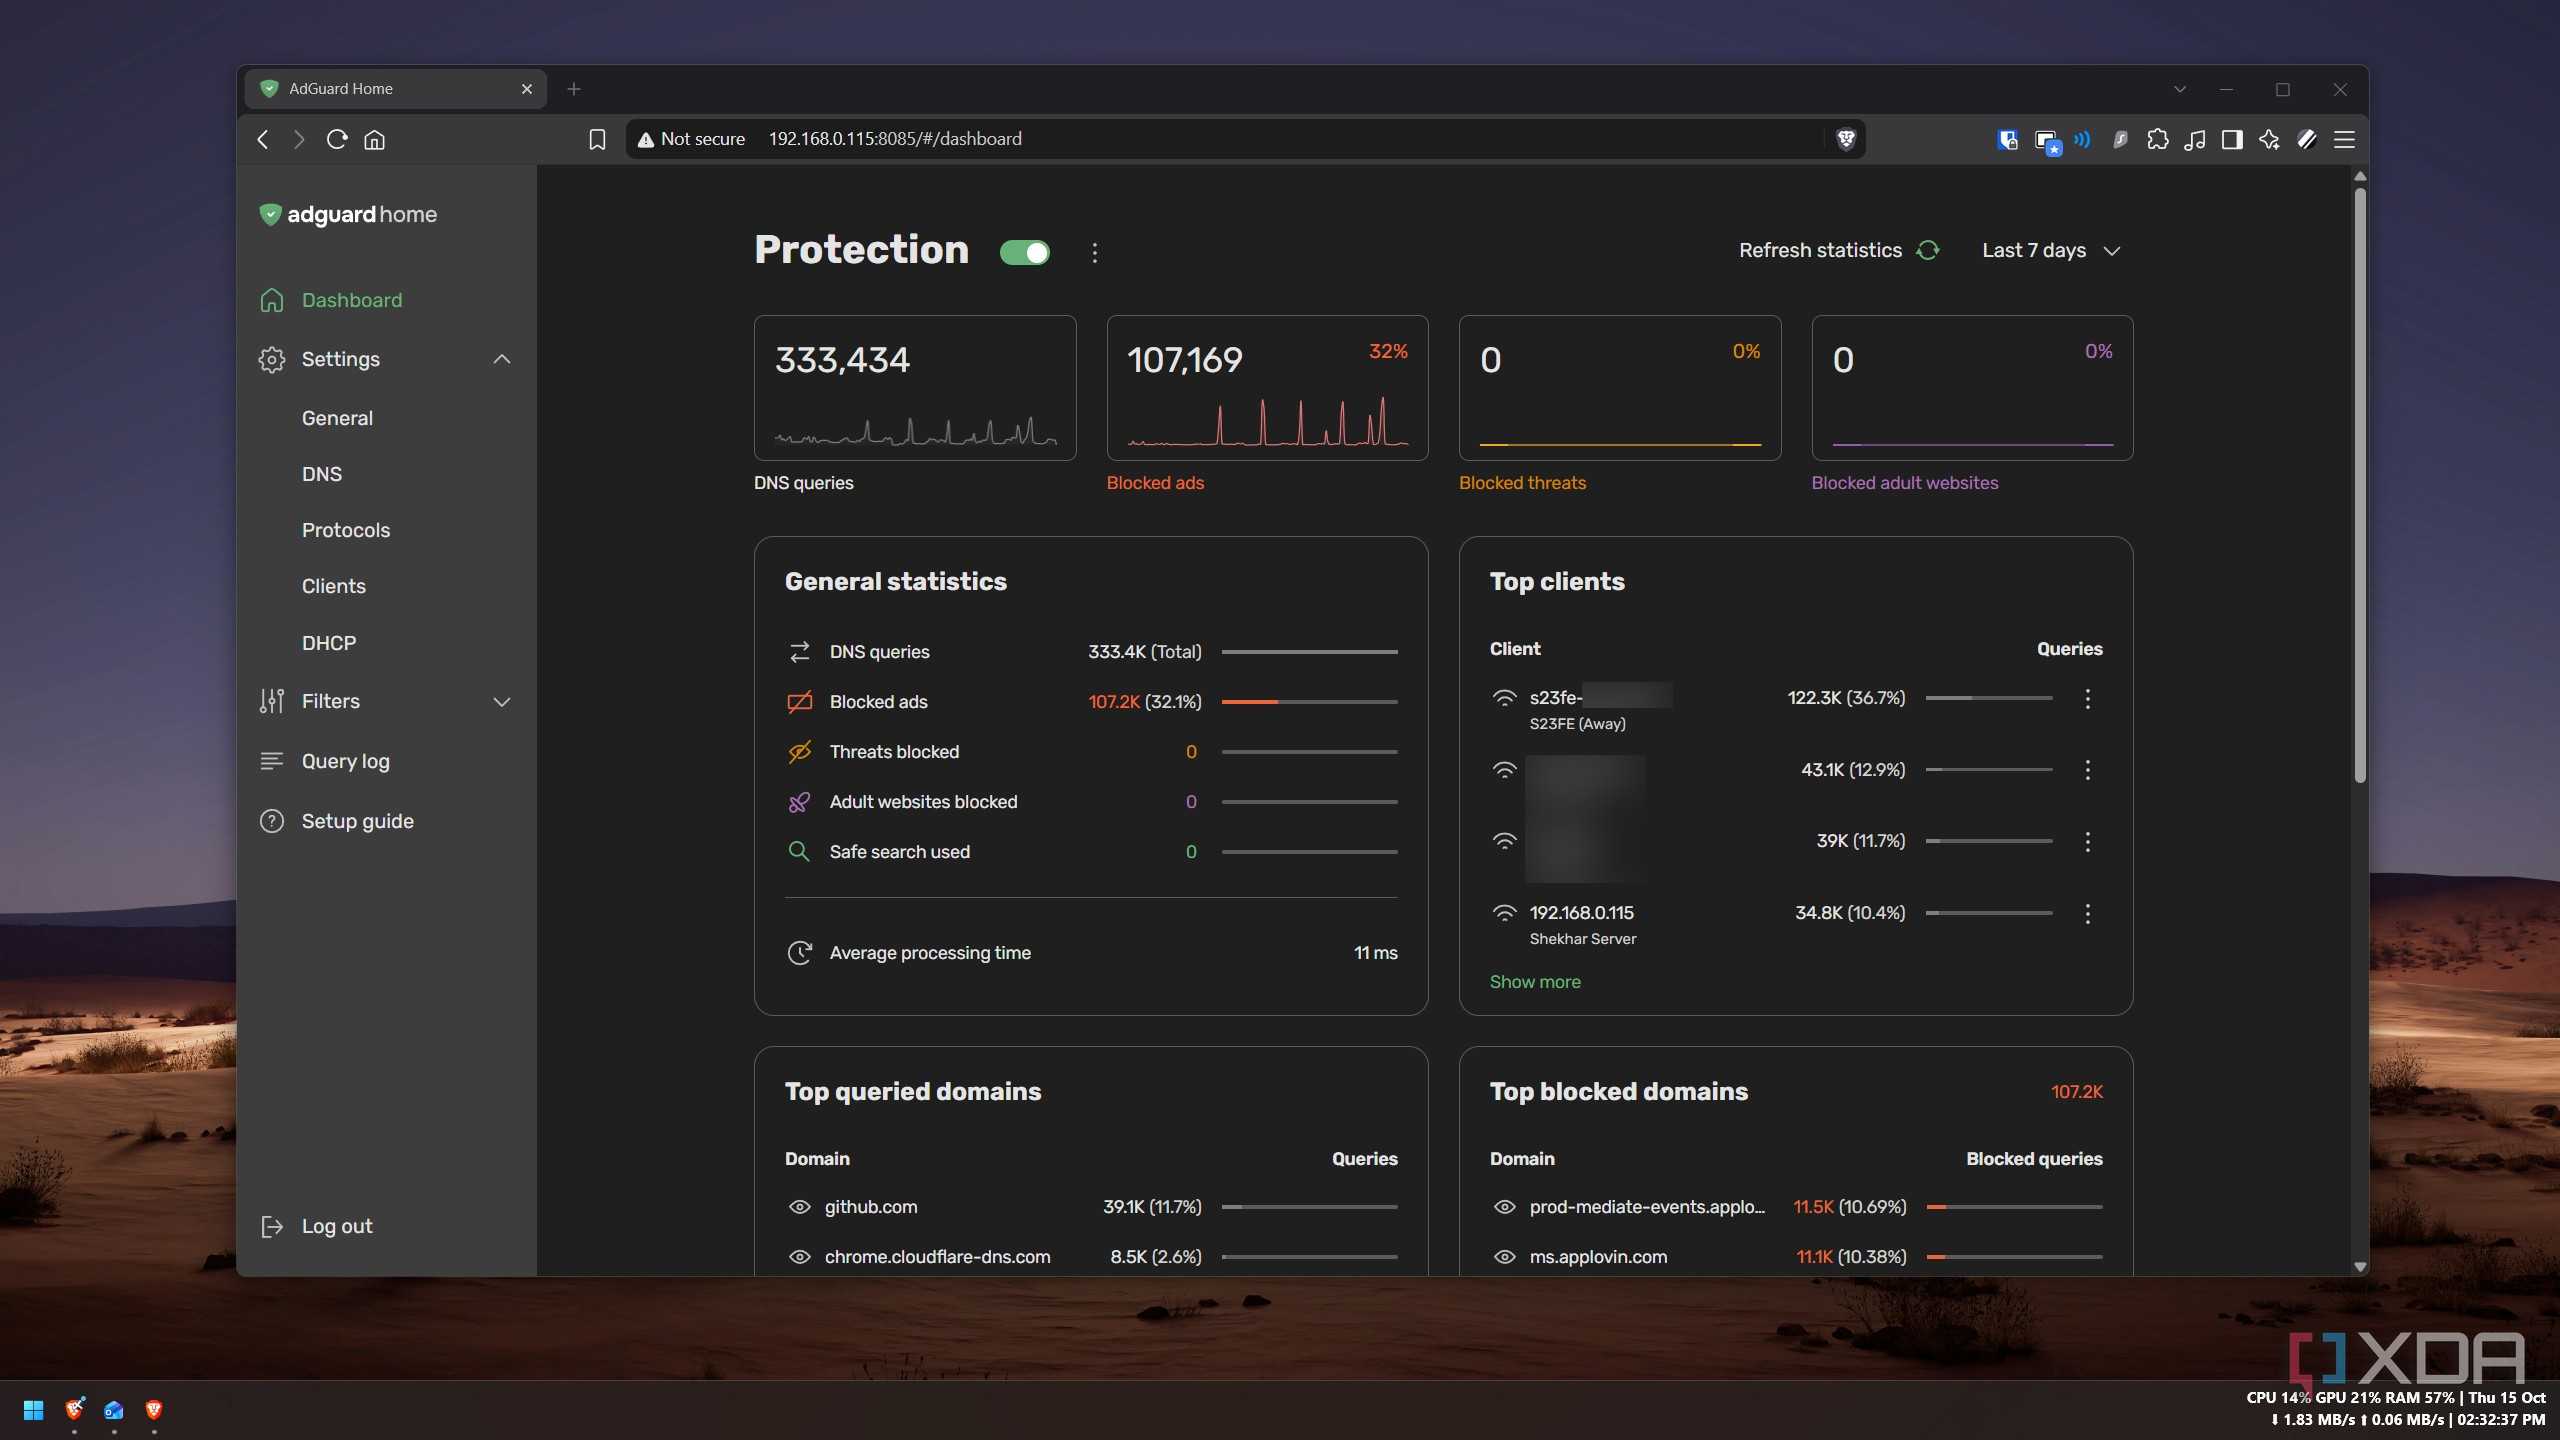
I started with just Pi-Hole, upgraded to Pi-Hole + dnscrypt, switched to AGH, then to just Unbound, then to Technitium, and then finally settled on AGH with DoH via Quad9. I had different reasons to make the switch — sometimes features, sometimes functionality, and sometimes UI — but they all had one thing in common. All of them worked as they were supposed to; they filtered requests and blocked them when needed.
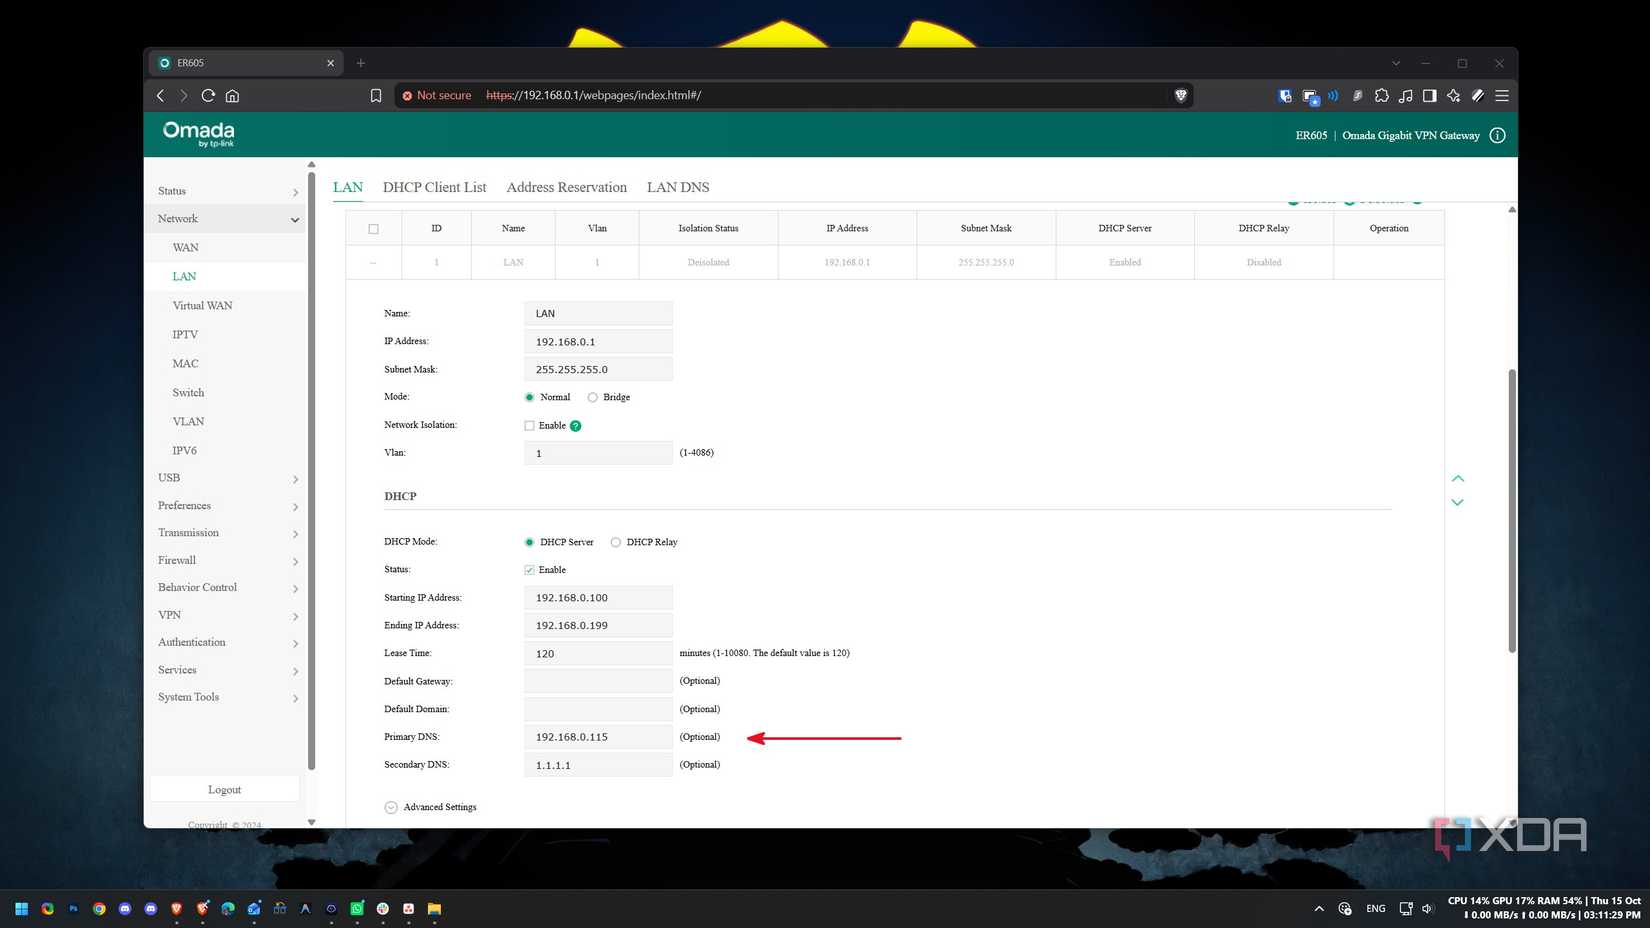
I always set it on my DHCP router as a DNS server so every device on that network could benefit without any extra setup. But the devices only benefited when they were at home. The moment I left home, that protection faded. With mobile data and public Wi-Fi, the ads and trackers AGH blocked at home started appearing again. To be clear, it wasn't an AGH or blocklist issue; it was how AGH was supposed to work.
I knew about encrypted DNS, but when I researched it earlier, I didn’t go forward because a big wall stood in my way. Both of my home internet connections were behind CGNAT, and without a public IP, internet traffic could never reach my home directly.
But last month, my primary ISP gave me a public static IP address, and that made me rethink encrypted DNS. Before moving forward, I checked my devices to see whether they actually supported encrypted DNS. Turned out both my phones (iPhone and Galaxy) supported it natively. So, I decided to set it up and point each phone at my own DNS service.
I pointed both phones at my house, and they ask it for everything
The iPhone took the easy door; Android didn’t
I thought setting it up and getting my phones to use the filtering service would be straightforward, but it was only simple in principle; making both phones actually use it was tricky.
Before I go through each phone’s setup, let me explain how I set up encrypted DNS. Don’t worry. I won’t bore you with every minute detail. Even though I have a public IP and my own router, which I use for DHCP, the PPPoE session is still on my ISP-managed ONT.
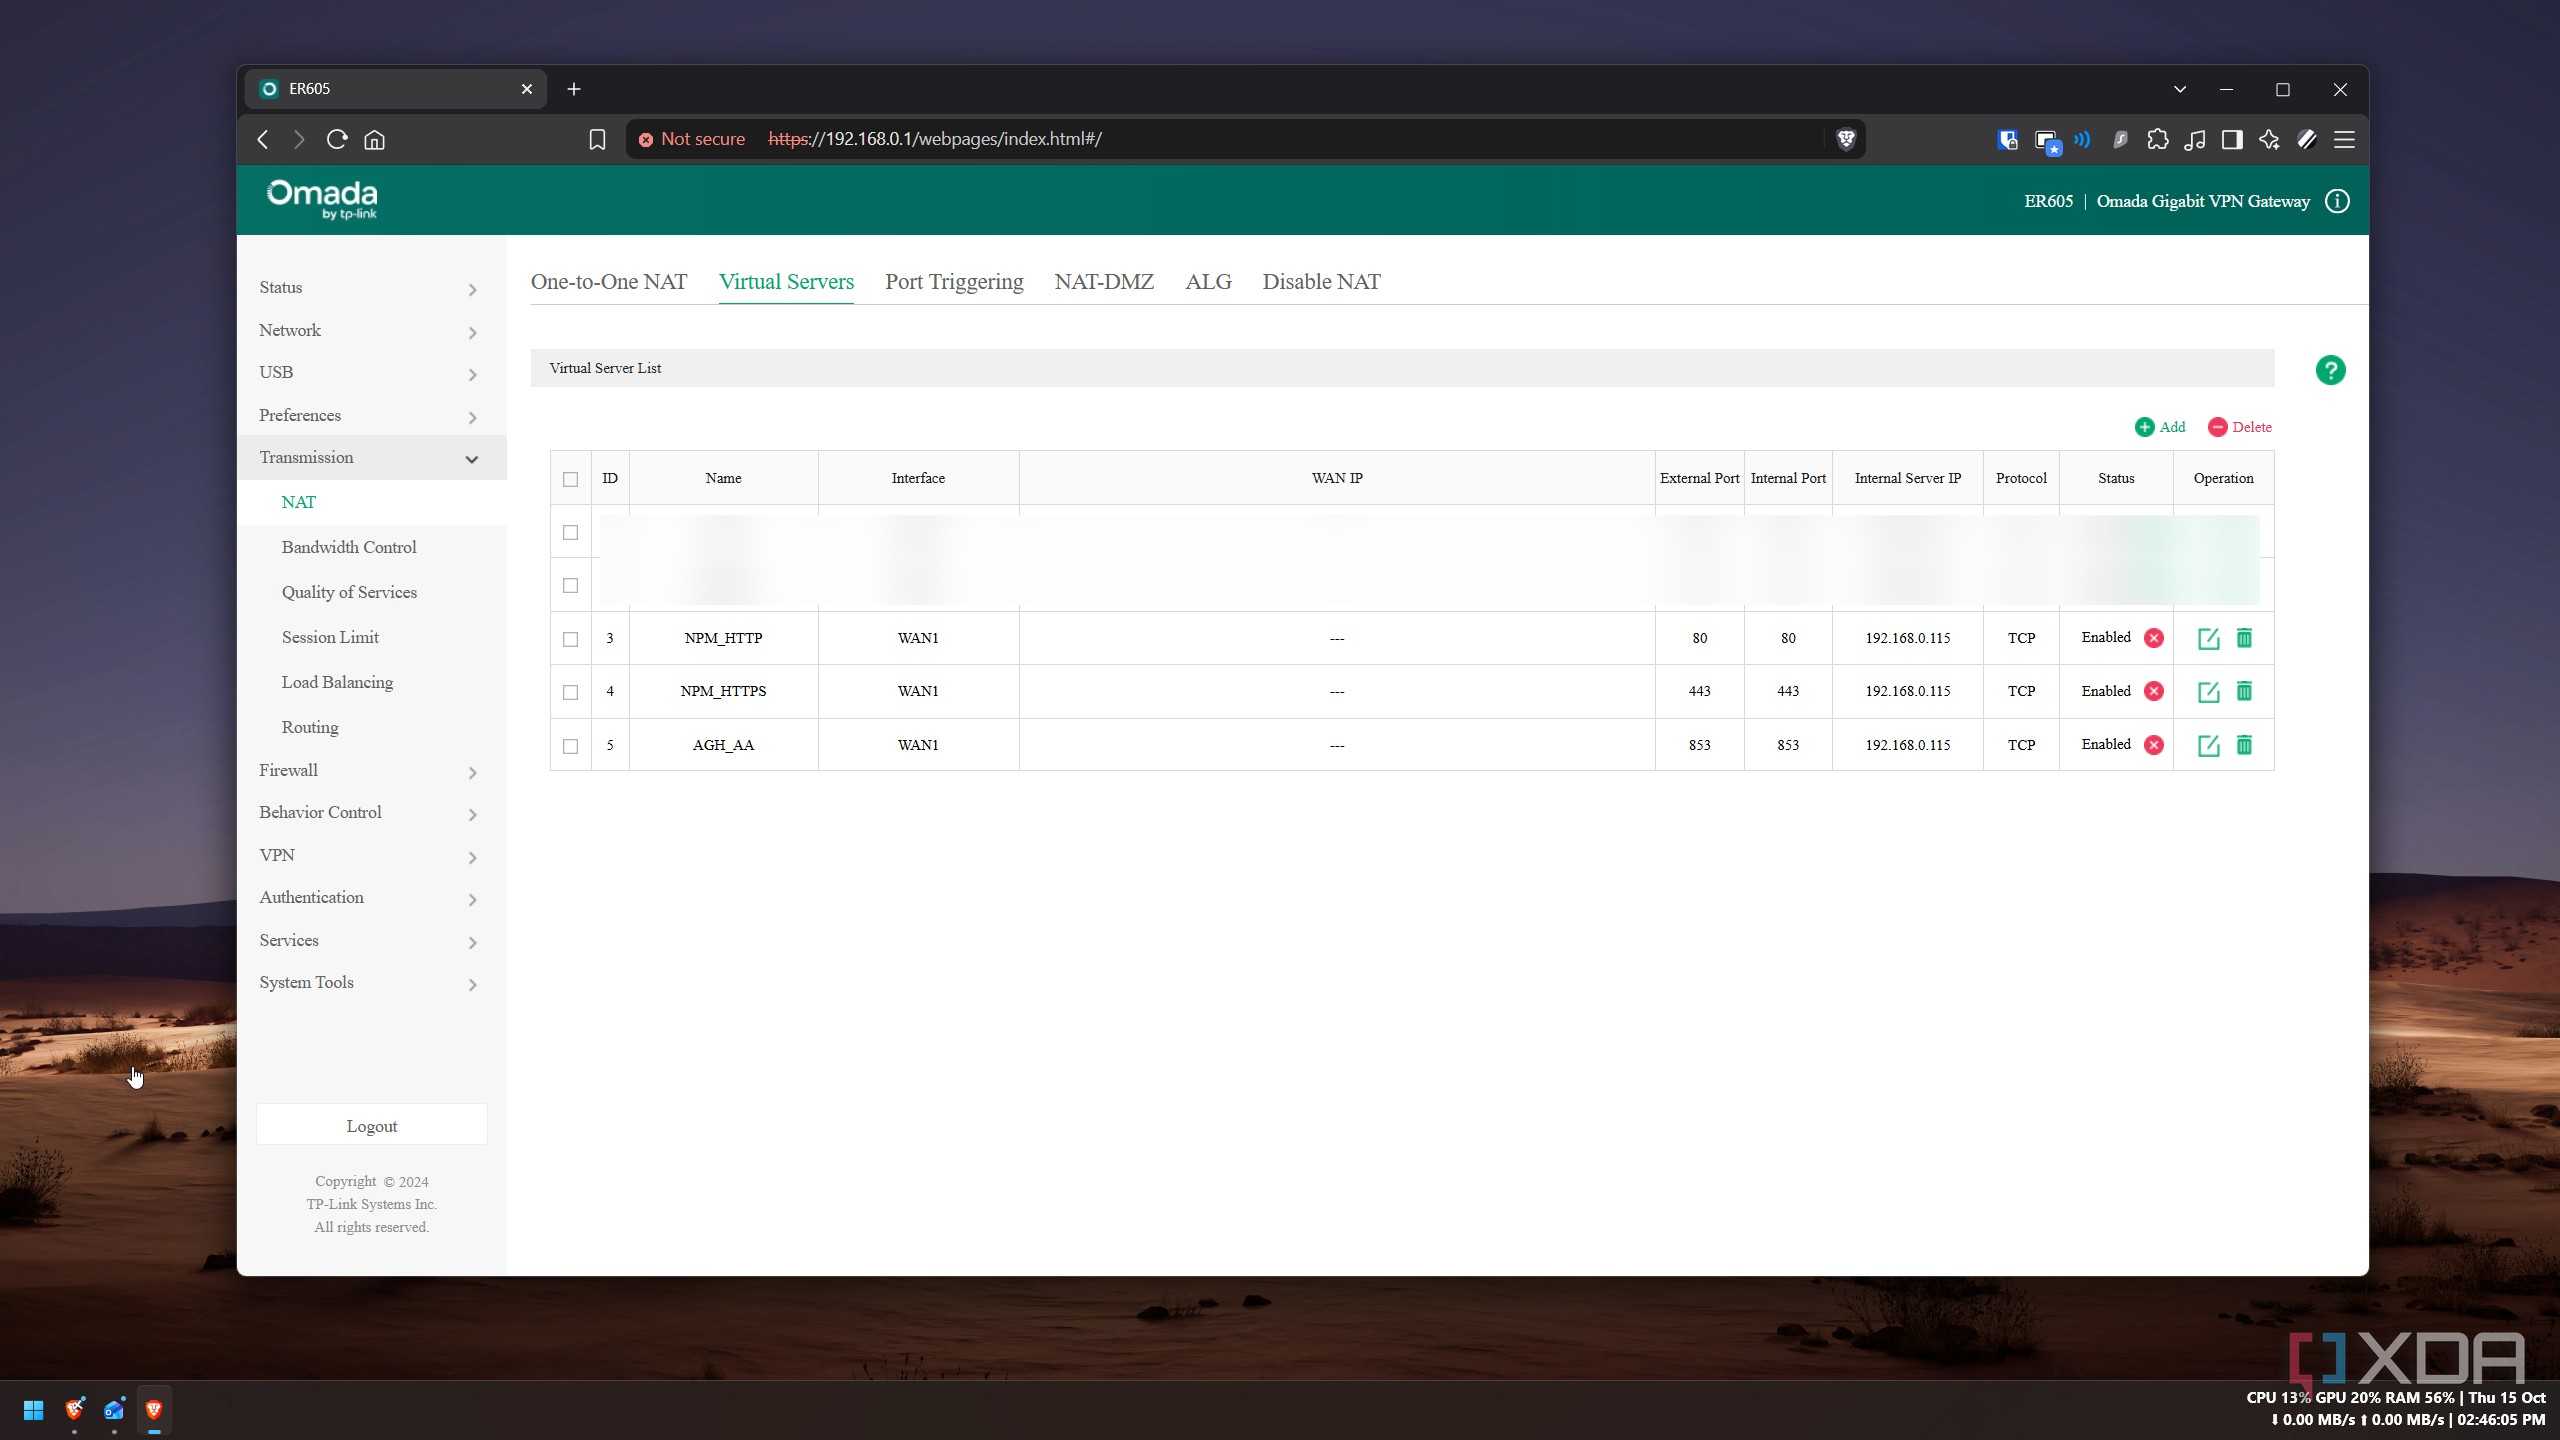
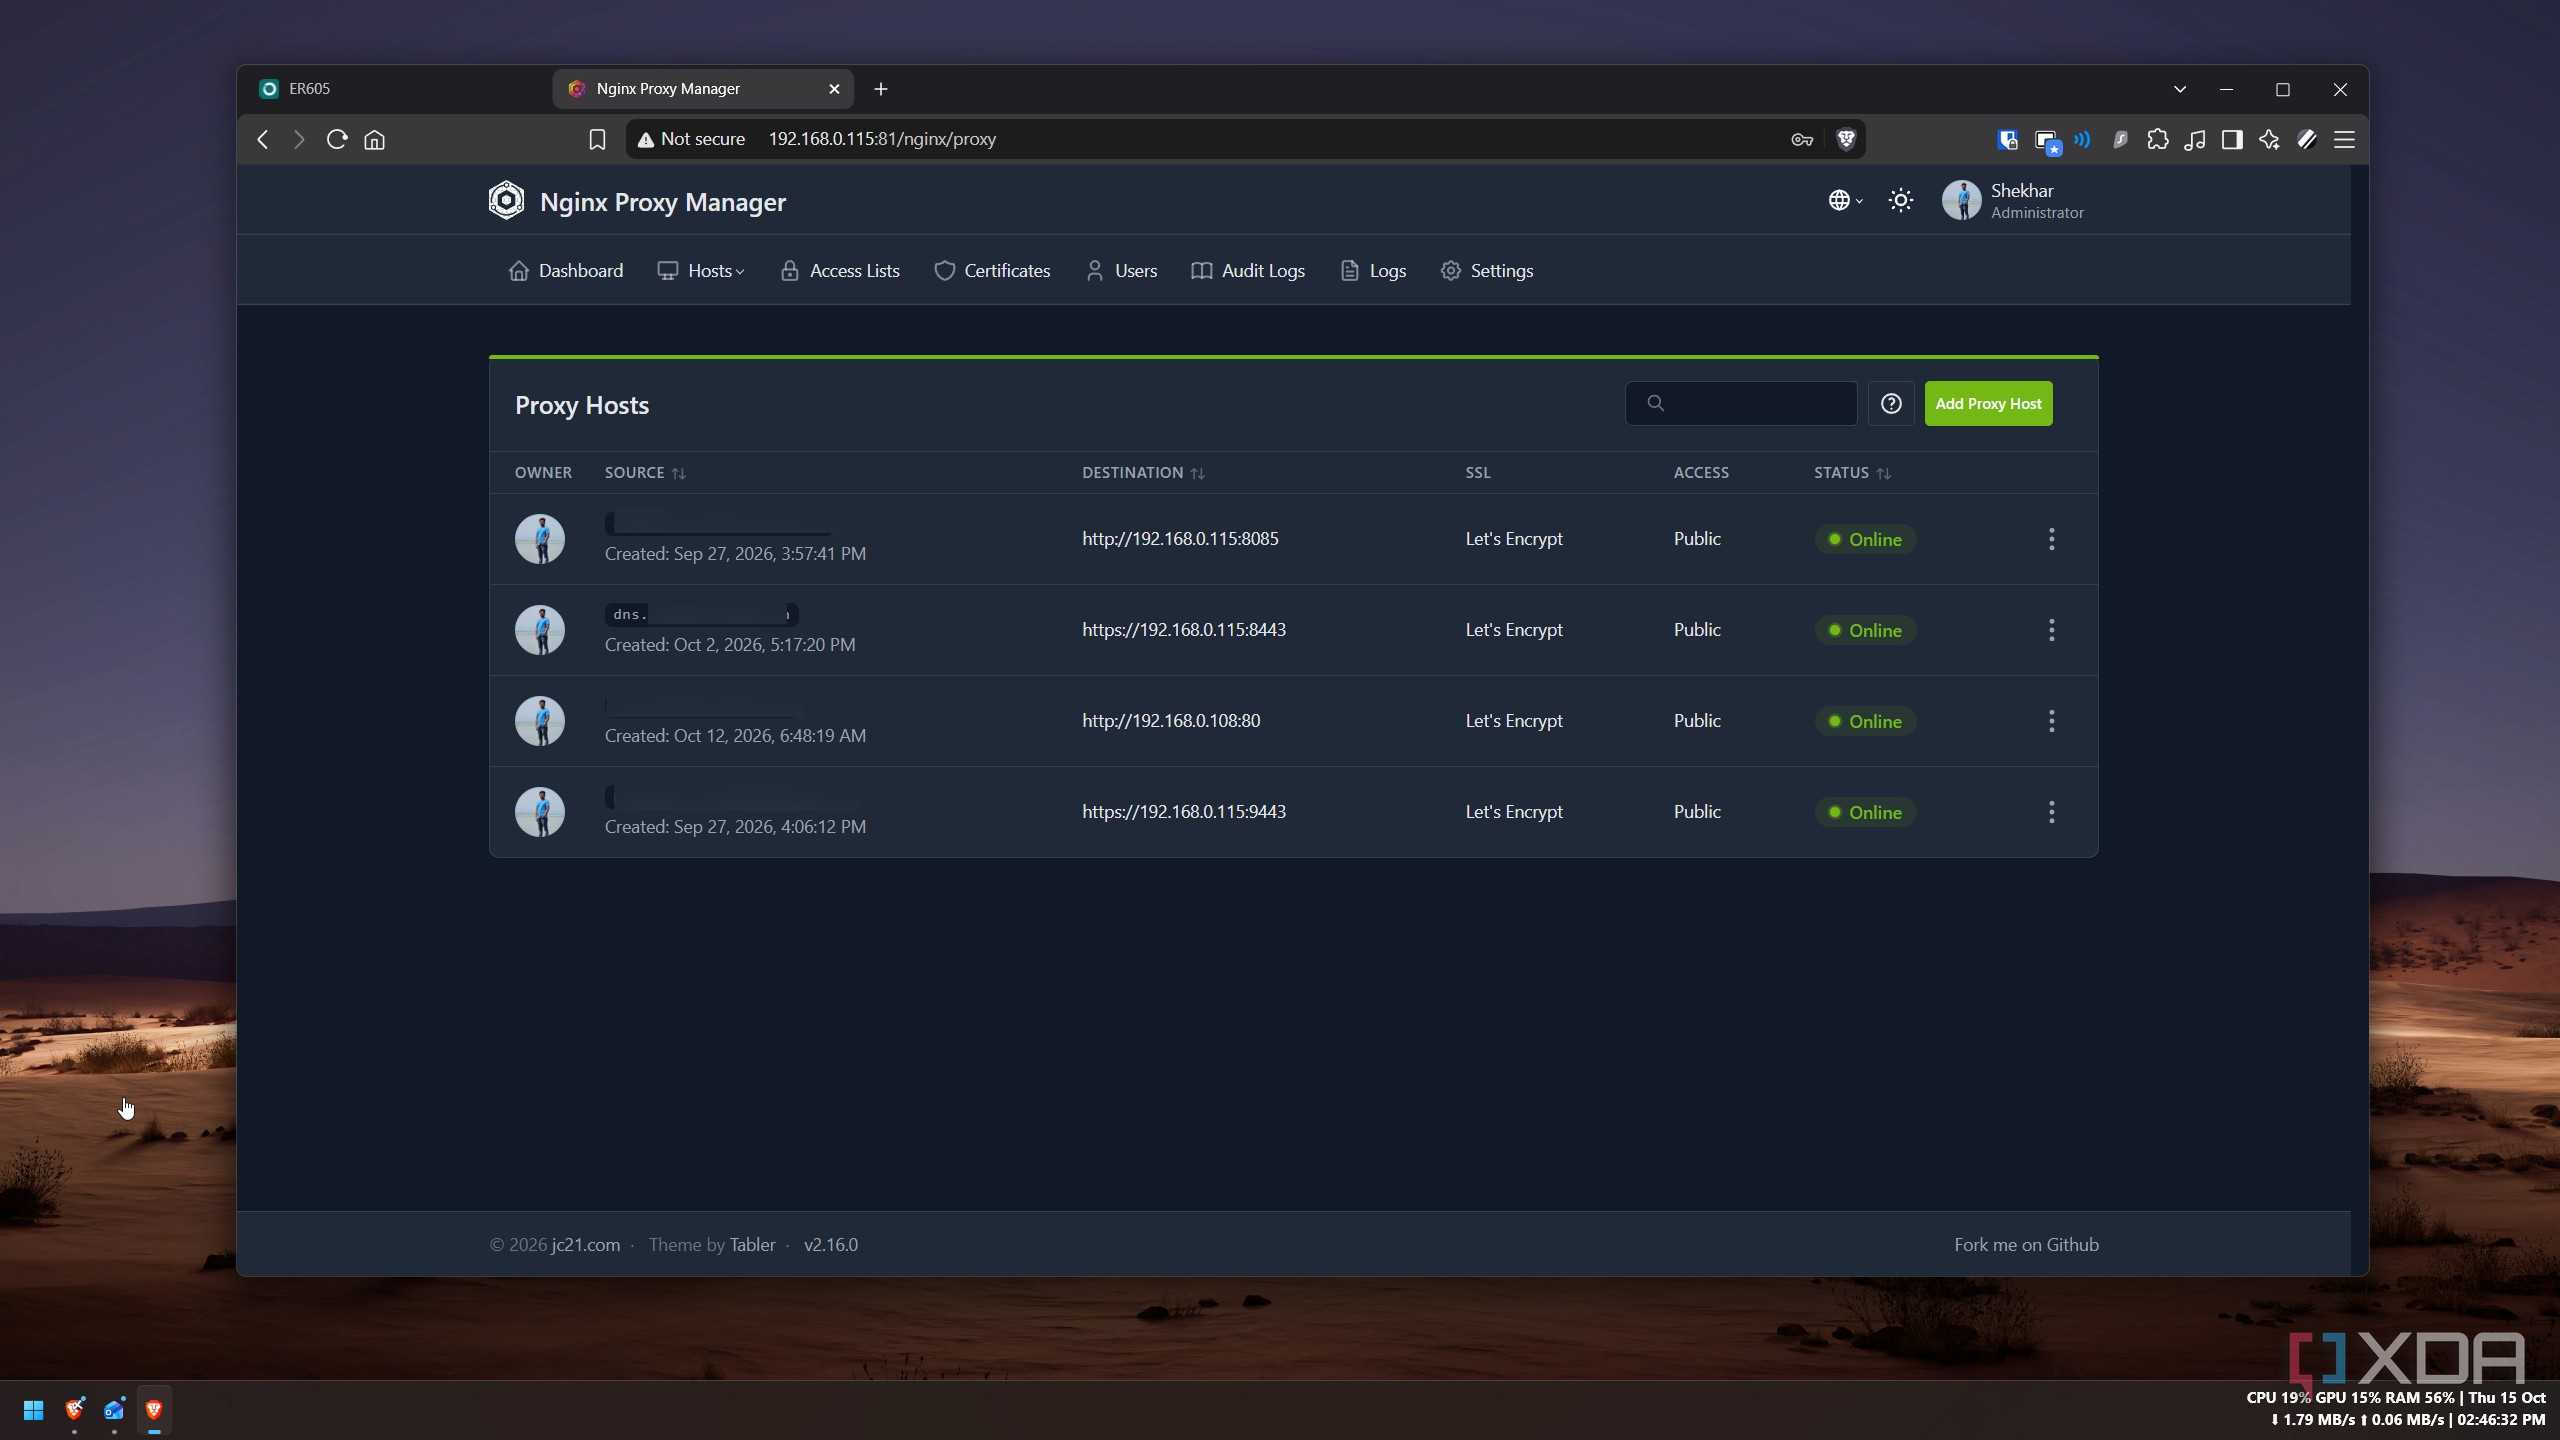
You might be thinking, why not move the PPPoE to my own router, right? But that is a whole different story, and I have already talked about it. That’s how internet traffic reaches my ISP-ONT; then its DMZ hands everything to my router (ER605), which forwards it to my home server. Nginx Proxy Manager (NPM) listens on 80/443.
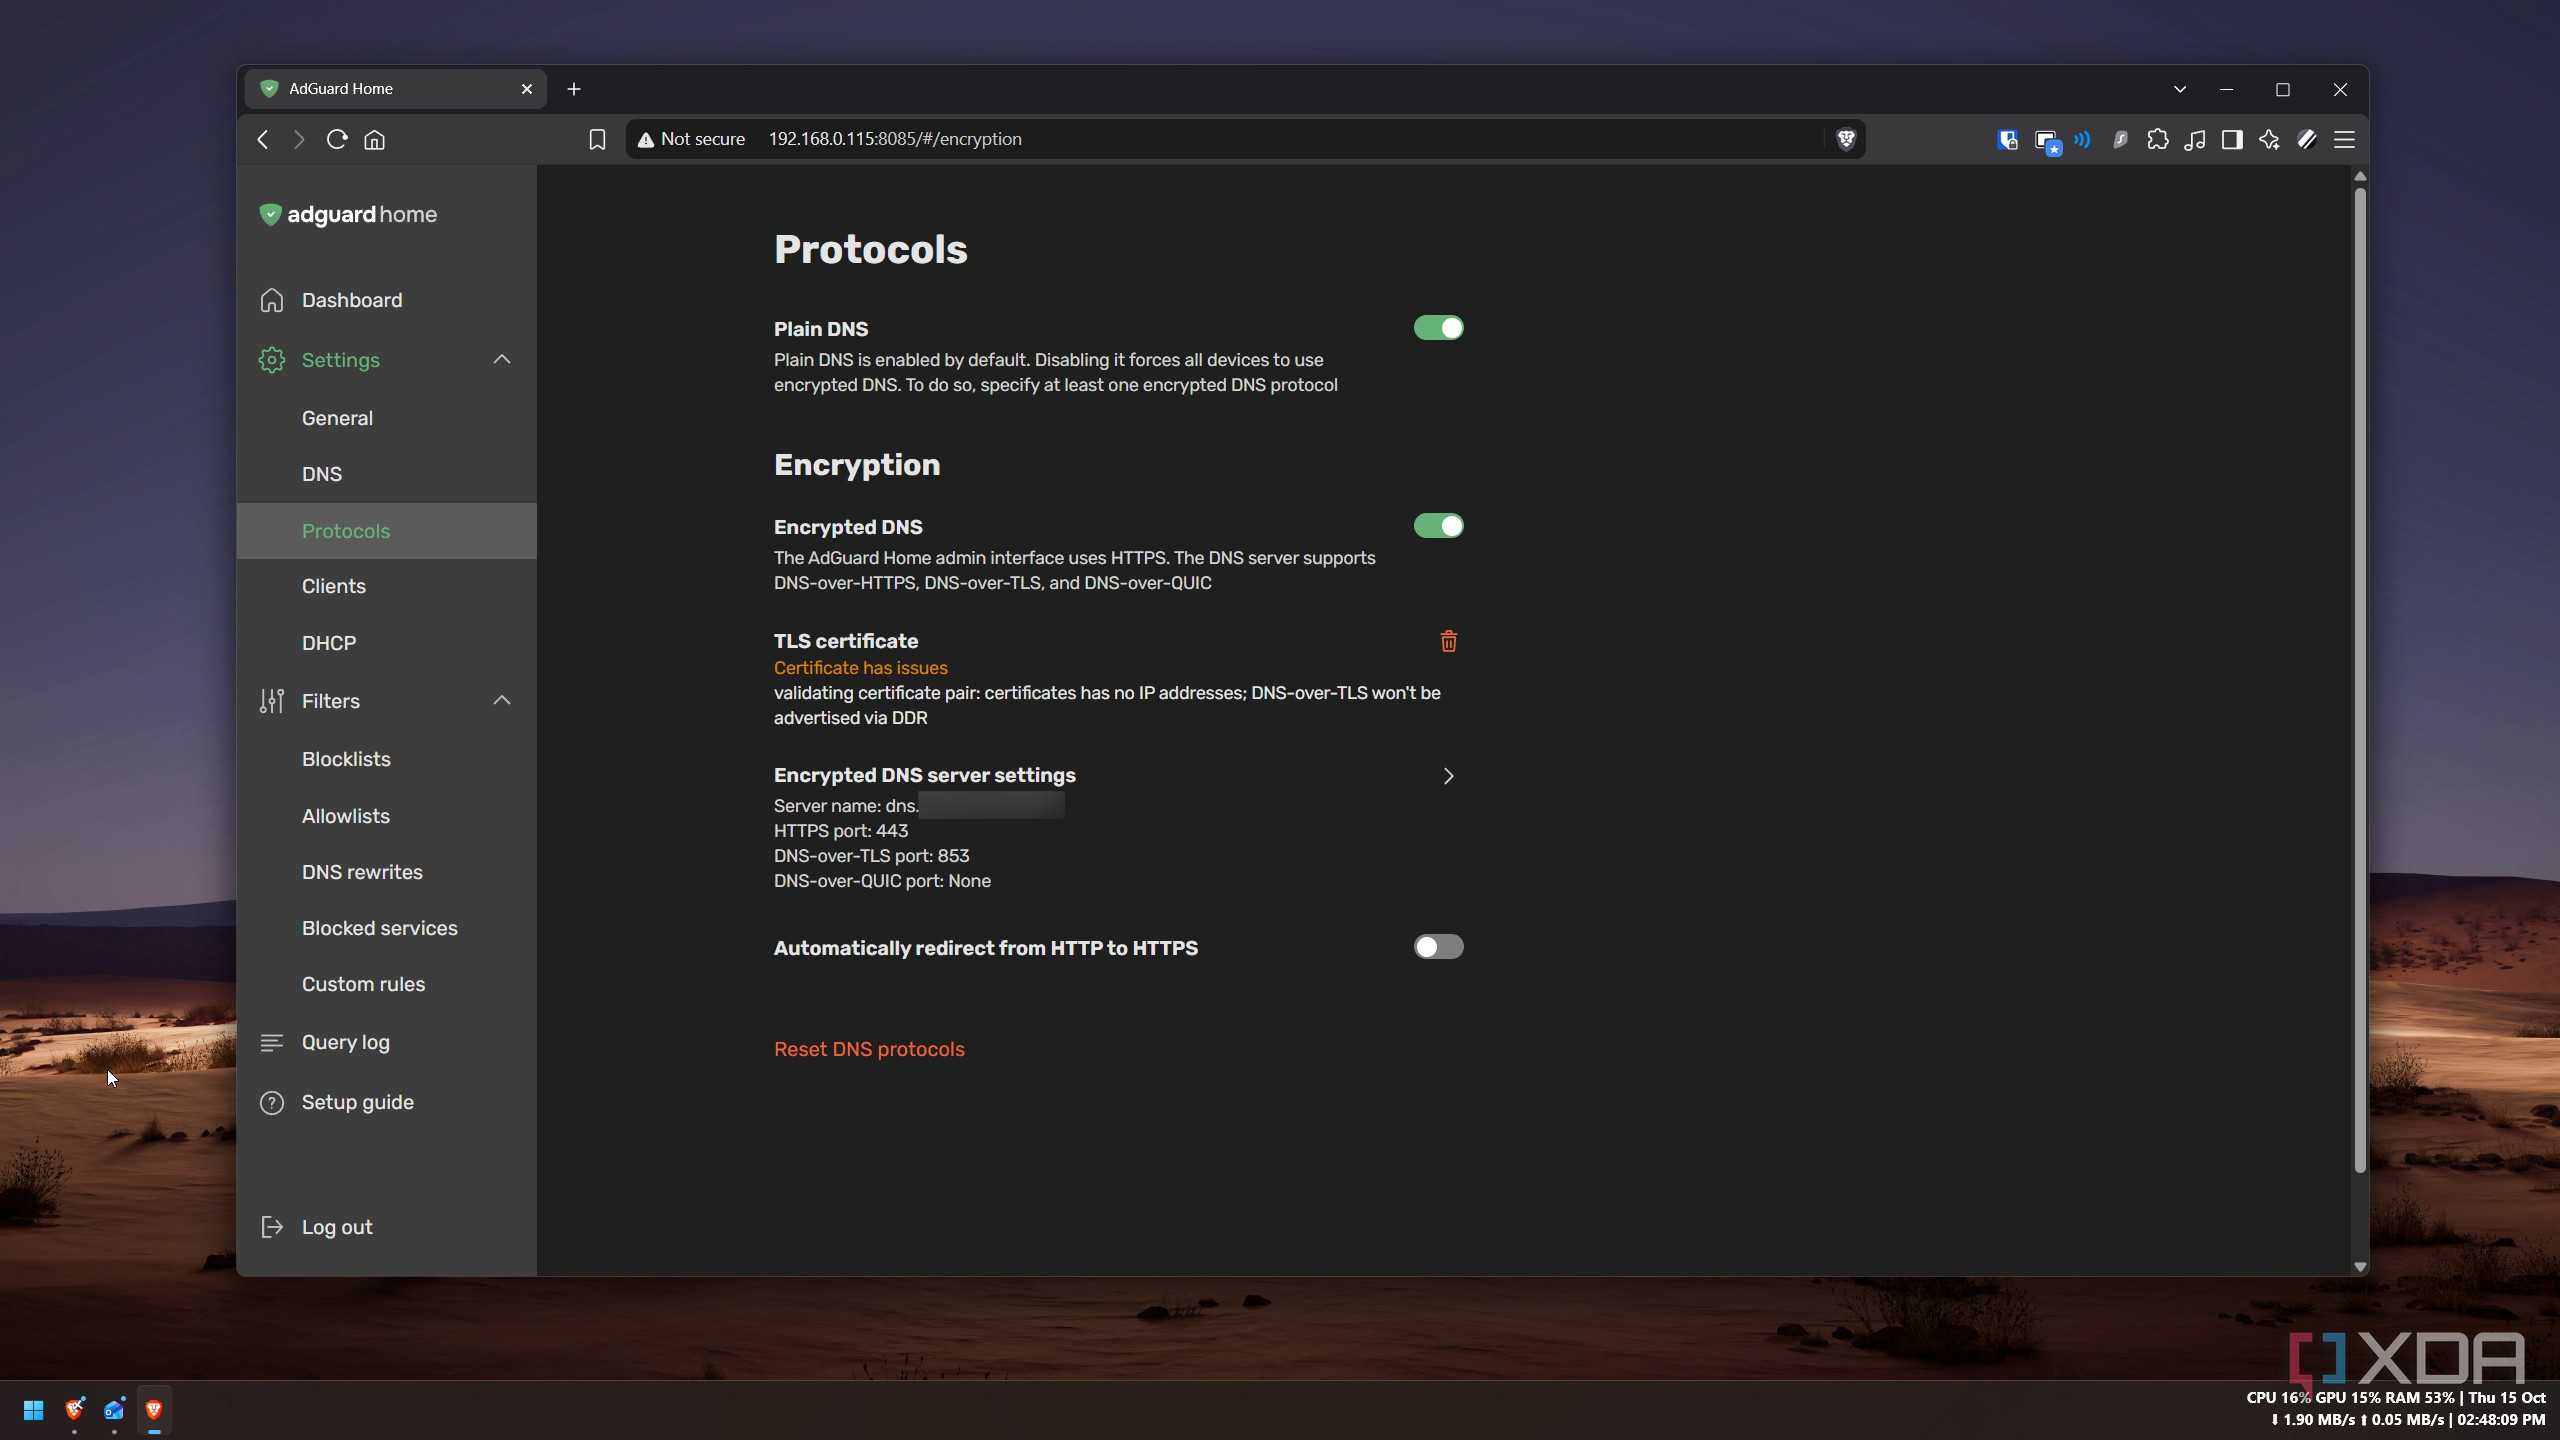
Coming back to the actual encrypted DNS setup. I exposed AGH through my own domain (dns.example.com) using the static public IP and a valid TLS certificate on NPM. And AGH used the same certificate. Now, the phones could be pointed at it and send their DNS requests to the home server using built-in encrypted DNS settings. But the routes for each phone were different.
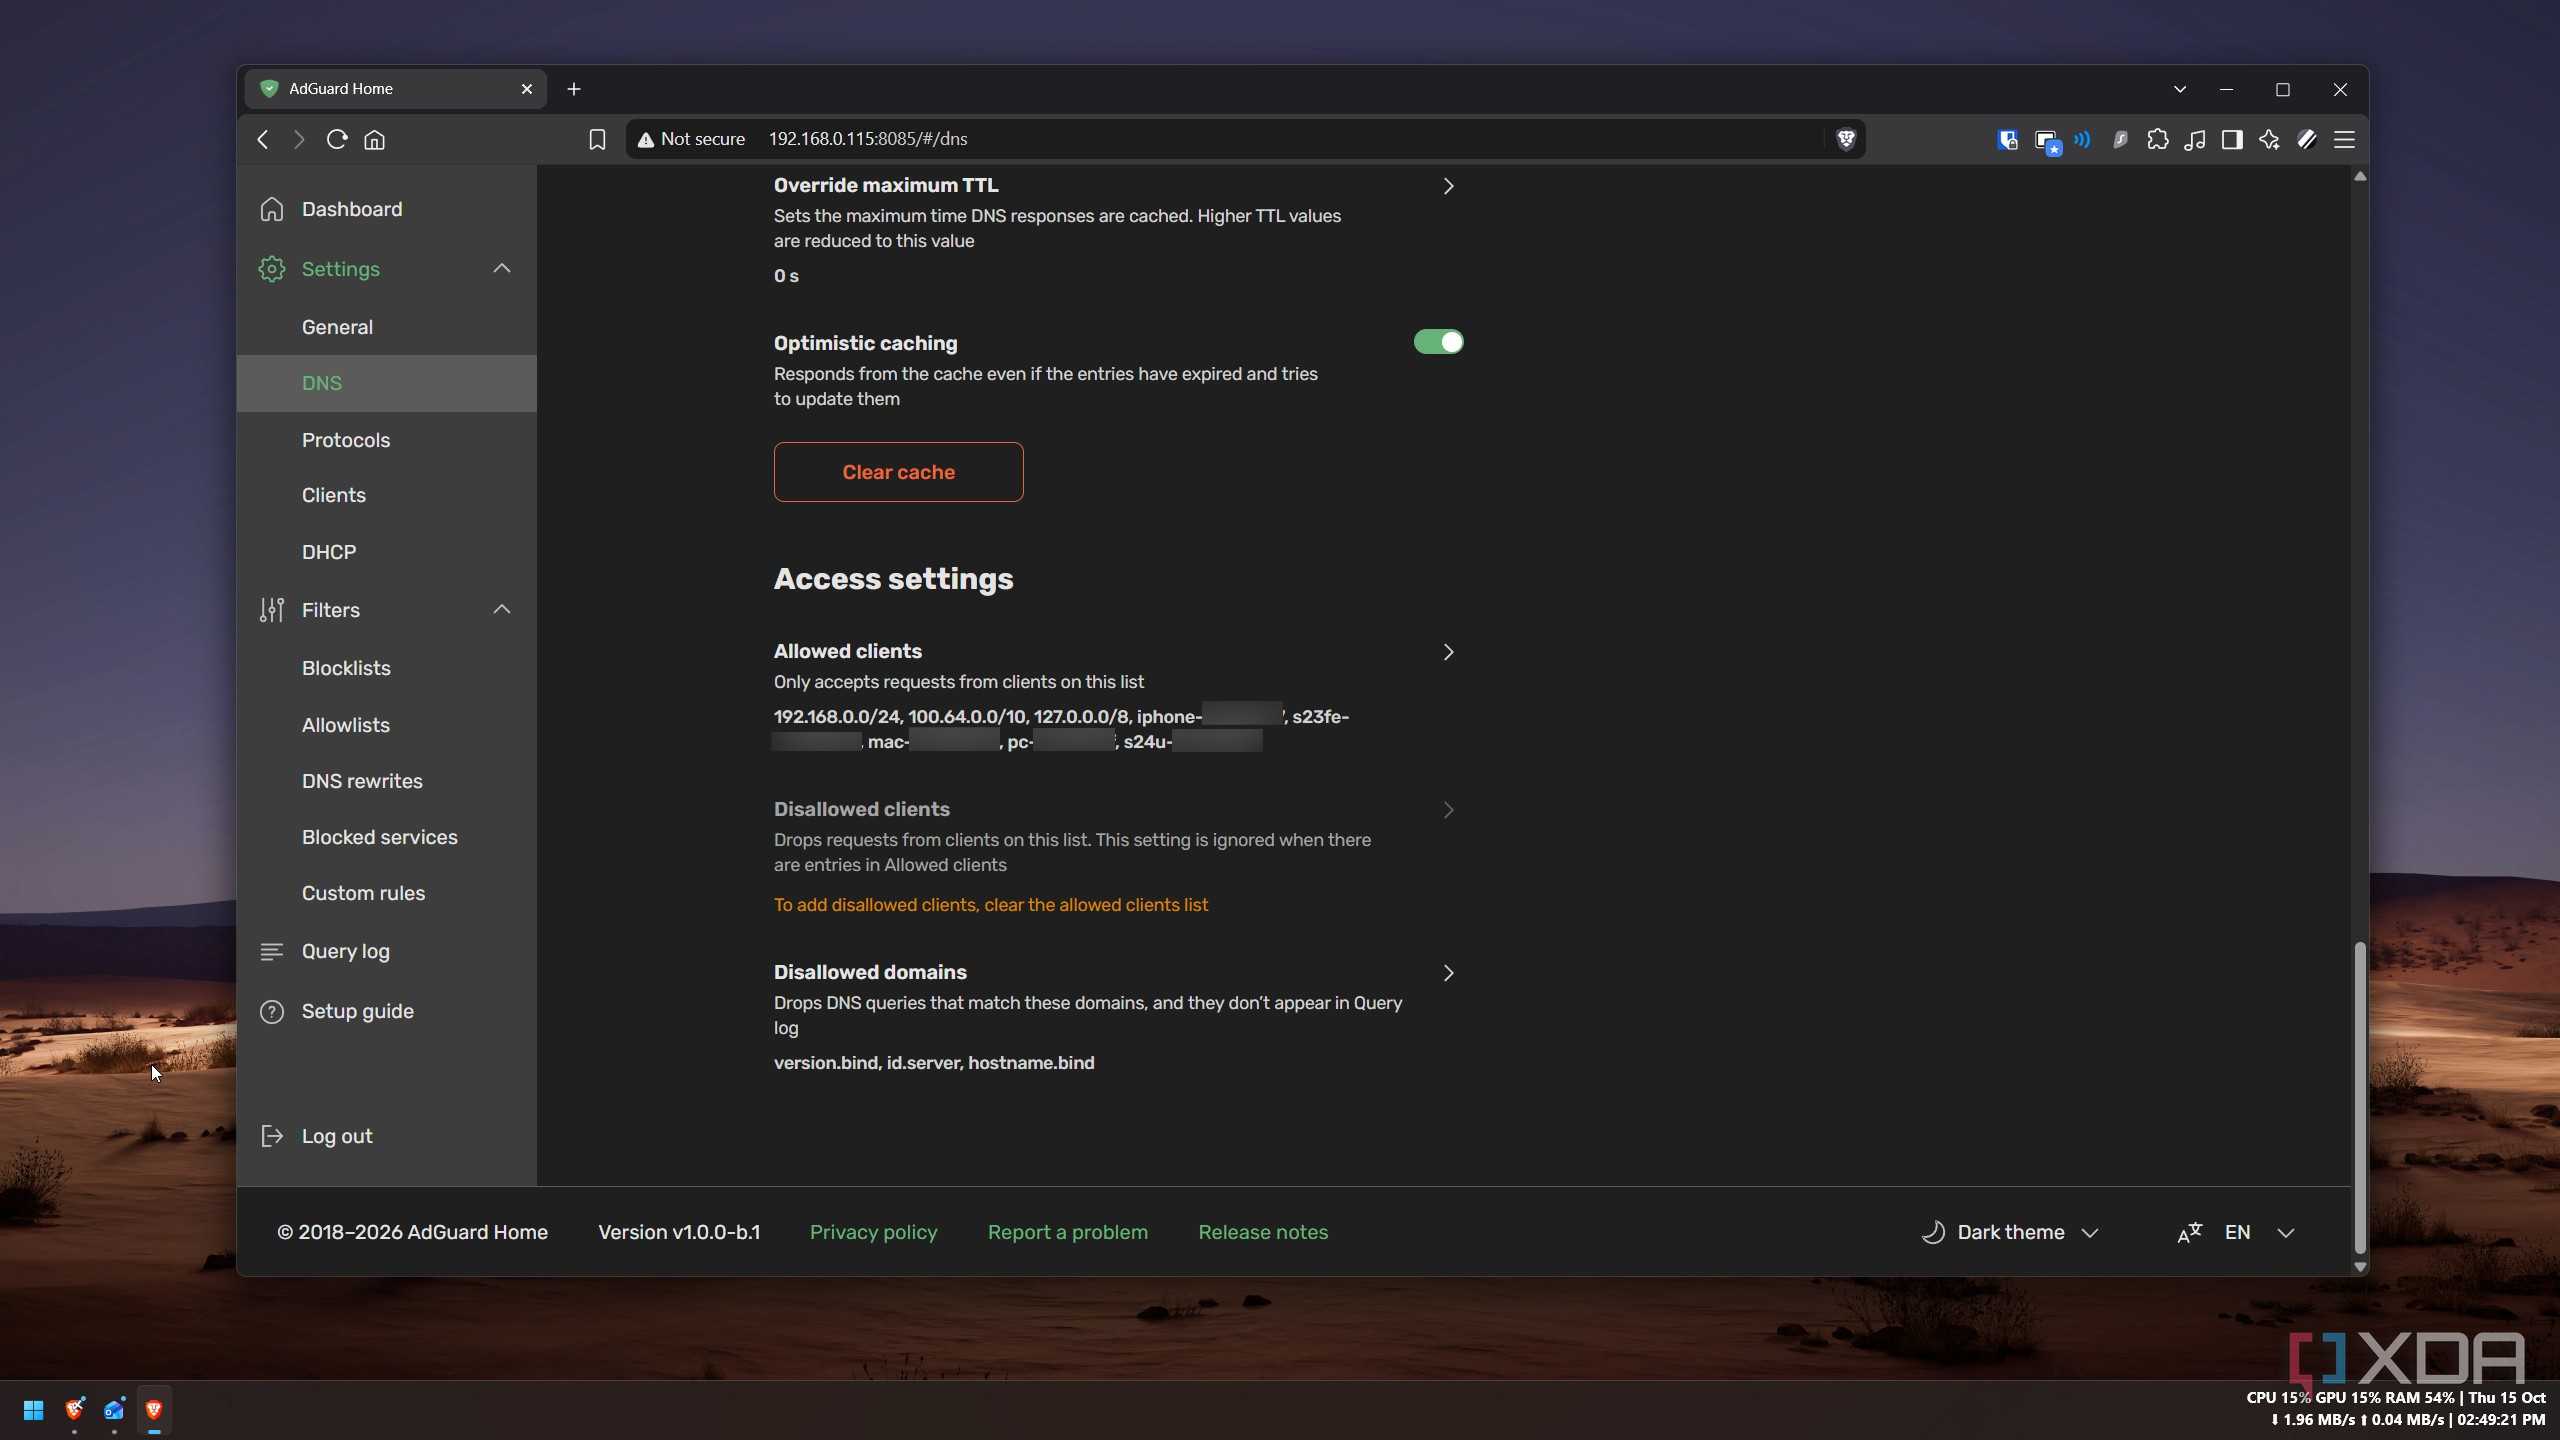
While the iPhone natively supported both DoH and DoT, I set up a DoH profile. Why DoH, if you ask? Because 443 was already exposed, and it was straightforward. Since the phone’s public IP would be changing when I’m away, I tied the iPhone (also Android) to a unique device ID. The unique device ID would also help differentiate the devices in the logs, and with Allowed clients on, it would work as the credential as well.
http://192.168.0.115:8085/apple/doh.mobileconfig?host=dns.domain.com&client_id=iphone-uniqueidAfter the iPhone, I tried to set it up on Android similarly, but Android’s system-wide Private DNS only accepted a hostname and used DoT, so DoH wasn’t an option. And for DoT to work, I had to expose another port (853) for it. Once that was done, I used a subdomain (s23fe-unique-id.dns.domain.com) as the Private DNS hostname. This extra setup reduced an extra hop DoH was doing via NPM.
The initial setup was a little messy, but after that it was simple. The DNS flow changed completely. Before the setup it was: Phone -> carrier DNS -> answer (no filtering), and now it is: Phone -> static IP -> ONT -> ER605 -> NPM (only iPhone) -> AGH -> back to the phone.
Then my own Wi-Fi broke it, and the fix came with strings attached
Mobile data was fine; my living room wasn’t

I tested mobile data on both phones, even on a different Wi-Fi network ; everything was working as expected. Ads were blocked, trackers were filtered, and I could see the requests on my AGH dashboard. But the moment I connected them back to home Wi-Fi, both phones lost internet.
After a couple of hours of fruitless troubleshooting, I found the actual issue when I ran a simple DNS lookup command for the encrypted DNS domain. The command returned my public IP, and because of my double NAT setup (ONT and ER605), the traffic kept timing out.
So, when both phones tried to reach the public IP from inside the network, because of the double NAT, the attempted hairpin connection timed out.
The fix was simple, though. I just had to rewrite the domain using AGH’s native DNS rewrite. I rewrote both dns. and *.dns. to the server's local IP address, and everything was back to normal.
But this whole setup came with a few trade-offs. At home, I set up a secondary public DNS server to fail over to when the home server or AGH was down, but the phones worked a bit differently.
Since iOS uses DNS profiles and treats it as a preferred encrypted server (not the only one), if AGH fails, it can fall back to the carrier's normal DNS. But Android’s Private DNS has two relevant modes — Automatic and Private DNS provider hostname. The second one is strict mode, and it never falls back to plain DNS. That means if AGH is down, the phone shows no internet.
Even though I have two internet connections at home, the whole setup depends on the primary ISP, which gives me a public IP address. So, if the primary ISP is down, the whole setup falls apart. Finally, this added one more responsibility on my shoulders: I will have to restart AGH once a month to pick up the renewed certificate.
It works, and I’m the one keeping it working
After all the back-and-forth setup, I can finally say that it works. The ads and trackers stay blocked at my home and wherever I travel. Now I depend on my ISP and my server for the DNS endpoint, but these trade-offs are worth it. In the end, the DNS resolver you already trust, Quad9 for me, now handles lookups instead of the carrier's DNS resolver or the public Wi-Fi’s. But note that your ISP can still see which sites you visit; the solution is ECH, which is a topic for another day.
AdGuard Home
A free, open-source, self-hosted DNS server that blocks ads and trackers across every device on your network.