Employees are bringing shadow AI into Kenyan businesses through everyday tasks such as summarising meetings, drafting documents and analysing information. The tools can save time, but they also create a security and governance problem when staff use services that their employers have not assessed or approved.
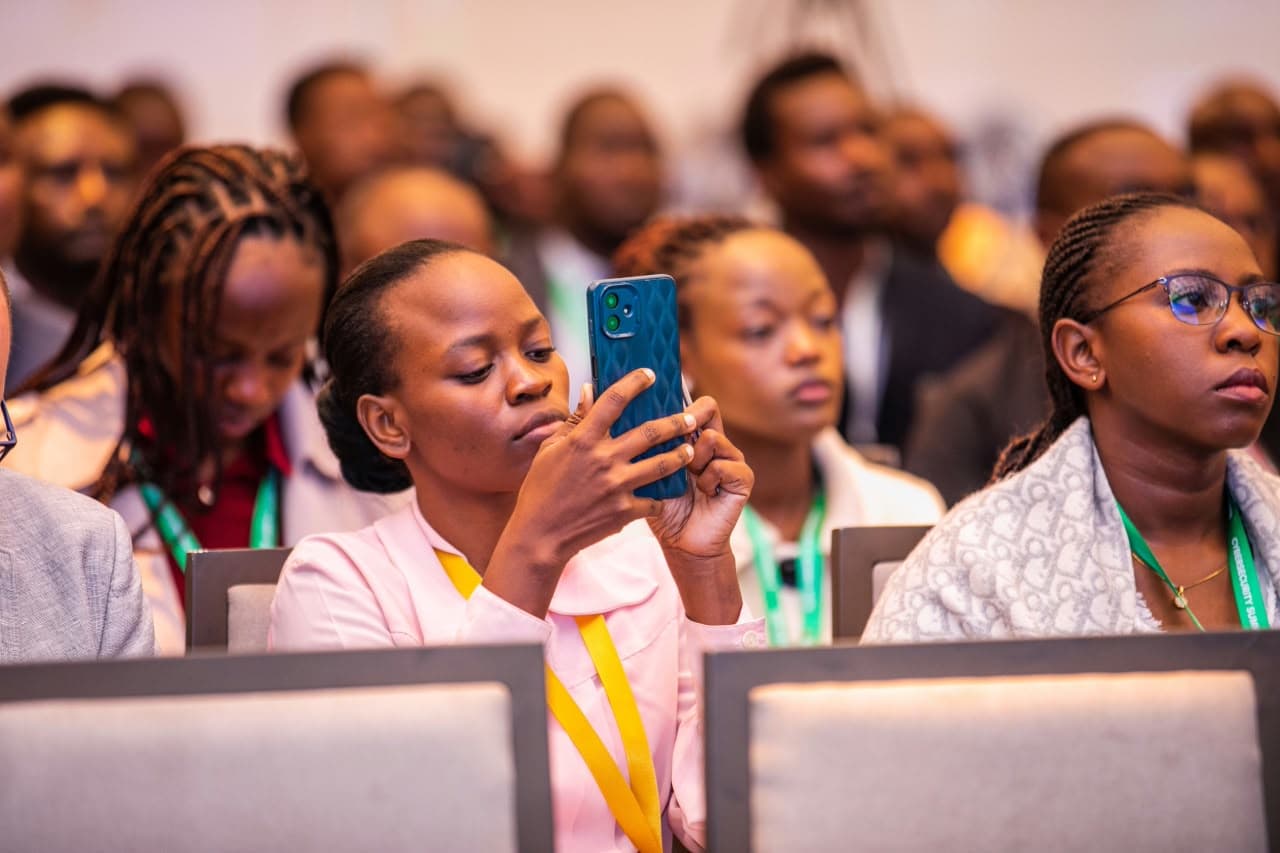
A poll conducted during a keynote by Akili AI chief executive Dr Simon Bransfield-Garth at the Safaricom Cybersecurity Summit 2026 highlighted the gap. Among roughly 150 summit attendees, 42% said they knew unapproved AI was being used in their organisations, while another 25% said they believed this was almost certainly happening. Only 6% said their organisation had a fully developed AI strategy and governance policy that had been reviewed and supported by staff training. The results reflect the views of people at the event, rather than a representative survey of Kenyan businesses.
What the summit poll revealed about workplace AI
The results point to a problem that can be difficult for management to see. Employees may begin using a public chatbot or an AI feature embedded in an existing software product without treating that decision as a new data-sharing arrangement. A staff member summarising a meeting, for example, may submit names, financial details or internal plans to a service that the organisation has not reviewed.
The risk depends on the tool, its settings, the information submitted and the organisation’s contractual and technical protections. It would be inaccurate to assume that every AI service uses every prompt to train its models, because data handling differs between products and account types. Businesses still need to understand those differences before allowing employees to process sensitive information.
How shadow AI can expose company information
AI tools can create new routes through which confidential information is copied, processed or retained. An organisation may have strong access controls for its internal systems while employees move selected data into a separate service to complete a task more quickly. If the business has no inventory of these tools, its security team may struggle to assess where the information has gone or which contractual protections apply.
The issue also extends beyond public chatbots. AI features built into productivity software, customer platforms and other business applications can process information as part of routine work. A policy that covers only one popular chatbot will therefore miss other systems employees already use.
Why blanket bans can be difficult to enforce
Blocking every AI service may appear to offer a simple solution, but it can encourage employees to find alternatives outside approved systems. It can also prevent teams from using tools that could improve customer service, reduce repetitive work or help staff analyse information more efficiently.
A more durable approach starts with visibility and clear rules. Organisations need to distinguish between low-risk tasks, such as improving the wording of non-sensitive material, and activities involving personal data, confidential records, financial decisions or other consequential work. The rules should explain which tools are approved, what information may be submitted and when human review is required.
What businesses can do now
Bransfield-Garth proposed a four-part approach: measure, manage, train and maintain evidence. Measurement means identifying the AI tools employees use, including features embedded in existing software. Management requires acceptable-use policies, risk assessments and procedures for responding to incidents. Training helps employees understand how data exposure can occur, while evidence means retaining records of reviews, training, identified risks and corrective action.
Business leaders should assign clear responsibility for these activities rather than leaving AI governance entirely to individual employees or the IT department. Legal, compliance, security, human resources and operational teams may all need to contribute, depending on how the organisation uses AI.
The immediate task is to establish what is already happening inside the business. Once organisations know which tools employees use and what information those tools handle, they can set proportionate controls without treating every AI application as either harmless or prohibited.
Real ESG impact doesn’t happen in panels alone, it happens in the rooms where financiers, operators, and policymakers actually align. Our GreenShift Forum 2026 cuts the noise, bringing together the people rewiring Africa’s sustainability and energy frameworks for one focused day in Nairobi. Secure your seat.
Go to TECHTRENDSKE.co.ke for more tech and business news from the African continent and across the world.
Follow us on WhatsApp, Telegram, Twitter, and Facebook, or subscribe to our weekly newsletter to ensure you don’t miss out on any future updates. Send tips to editorial@techtrendsmedia.co.ke
Follow Us


By George Kamau
I brunch on consumer tech. Send scoops to george@techtrendsmedia.co.ke