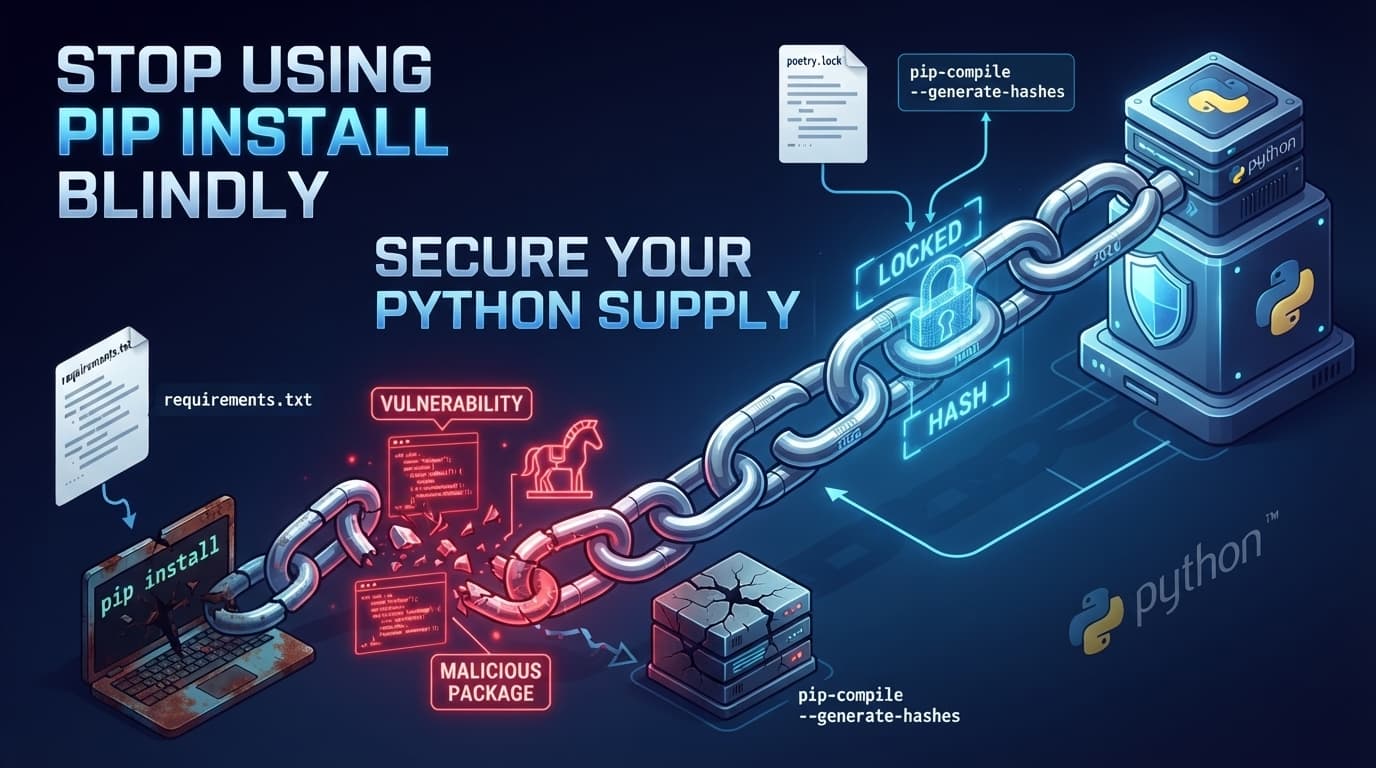
Modern software engineering moves fast. When building a new Python service or spinning up a microservice architecture, the instinct is often to fire up your terminal, type pip install, and let your requirements.txt file fill up with whatever version happens to be latest.
In 2026, the threat landscape has changed drastically. Software supply chain attacks—ranging from dependency typosquatting and malicious package updates to silent compromise of third-party repositories—have made the Python Package Index (PyPI) a primary target for malicious actors.
If you are running unpinned, unverified packages in production, your infrastructure is one rogue pip install away from a security breach. Here is how to lock down your Python supply chain and move from casual script management to enterprise-grade security.
1. The Hidden Vulnerability: Why Traditional Requirements Files Fall Short
The standard workflow of maintaining a flat requirements.txt file using pip freeze has critical architectural flaws:
- Unpinned Versions: Using loose version constraints (or no constraints at all, like
requests>=2.0) means every time your CI/CD pipeline builds a container, it pulls whatever code currently lives on PyPI. If a package maintainer's account is compromised, your next build automatically pulls malicious code. - Lack of Cryptographic Integrity: Standard requirements files do not verify package hashes. If a package is tampered with on a registry mirror or compromised upstream,
pipinstalls it blindly. - Transitive Dependency Blind Spots: You might carefully check your direct dependencies, but what about the 45 sub-dependencies they pull in? Vulnerabilities and malicious code almost always hide deep in the transitive dependency tree.
2. Modern Dependency Management: Transitioning to Poetry and Pip-Tools
To secure your application, you need deterministic builds. Modern Python tooling provides two primary ways to lock exact versions and cryptographic hashes: Poetry and pip-tools.
Using Pip-Tools for Strict Locking
If you prefer sticking close to native pip workflows, pip-tools allows you to manage abstract dependencies in a requirements.in file and compile them down to a fully locked, cryptographically hashed requirements.txt.
Example requirements.in:
fastapi==0.115.0
uvicorn[standard]==0.30.0
httpx==0.27.0
Run the compiler to generate a pinned file with integrity hashes:
Bash
pip-compile --generate-hashes requirements.in
Using Poetry for Complete Lifecycle Management
Poetry manages your virtual environments, dependencies, and publishing through a strict poetry.lock file. The lockfile records exact versions and cryptographic hashes for every single package and sub-dependency.
To add a secure dependency:
Bash
poetry add fastapi
When your CI/CD pipeline runs poetry install --sync, it guarantees that the exact bytes downloaded match the cryptographic hashes recorded in the lockfile. If a package has been modified or tampered with, the installation aborts immediately.
3. Cryptographic Verification & Hash Checking in Production
In a secure enterprise environment, relying on HTTPS alone is not enough. You can force pip to verify that downloaded packages match expected SHA256 hashes.
When building containers or running deployment scripts, enforce hash checking:
Bash
pip install --require-hashes -r requirements.txt
If a package's hash does not match what is written in your locked configuration, pip will reject it. This completely neutralizes man-in-the-middle attacks and registry-tampering incidents.
4. Automated Supply Chain Scanning in CI/CD
Security cannot rely purely on manual checks. Your continuous integration pipeline must automatically audit your dependency tree before code ever hits a staging or production environment.
Integrating Safety and Bandit
You can run automated vulnerability scanners as a standard step in your CI/CD pipeline:
YAML
# Example GitHub Actions snippet for supply chain security
jobs:security-audit:runs-on: ubuntu-lateststeps:- uses: actions/checkout@v4- name: Set up Pythonuses: actions/setup-python@v5with:python-version: '3.12'- name: Install dependenciesrun: |
          pip install --upgrade pip
          pip install safety pip-audit
      - name: Scan dependencies for known vulnerabilitiesrun: |
          pip-audit --requirement requirements.txt
Tools like pip-audit cross-reference your exact locked package versions against live vulnerability databases (like the OSV database), catching CVEs before deployment.
Summary Best Practices for 2026
- Never use unpinned requirements: Always lock minor versions and sub-dependencies using Poetry or
pip-tools. - Enforce cryptographic hashes: Leverage
--require-hashesto ensure packages haven't been altered upstream. - Automate vulnerability scans: Integrate tools like
pip-auditorSafetyinto every CI/CD pull request. - Audit your supply chain: Treat third-party packages with the same security rigor as your own proprietary code.
By hardening your Python package workflow, you protect your infrastructure, safeguard your users, and establish a truly production-ready engineering standard.