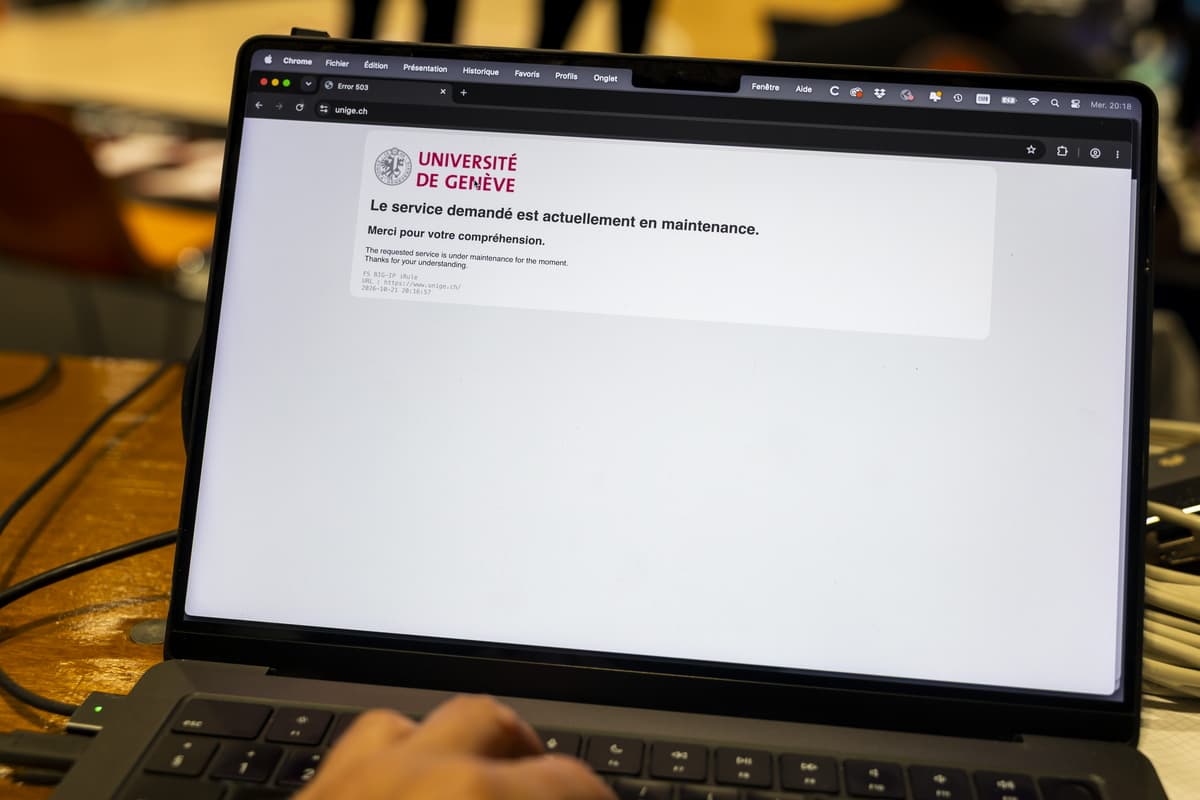
Companies and public agencies worldwide scrambled to respond after critical security flaws were found in a programming language used across much of the internet.
Developers of PHP, a programming language widely used to build websites, released an emergency update on the 21st fixing two critical vulnerabilities known as PHP2Shell, The Wall Street Journal reported.
PHP, often called the backbone of the web, powers roughly 70% of all websites, including popular platforms such as WordPress and Wikipedia's MediaWiki. The newly disclosed flaws allow hackers to execute arbitrary code remotely or take over systems without any login or authentication, according to reports.
The weakness had been flagged as a potential problem in the past, but was considered too difficult to exploit in a real attack, and no action was taken. The rapid advance of artificial intelligence hacking capabilities turned it into an immediate threat. Cybersecurity firm Calif found the vulnerability using OpenAI's GPT-5.6 Sol model, while Wiz, a Google-affiliated cybersecurity firm, independently discovered and reported the two flaws. Ami Luttwak, co-founder of Wiz, called it the most serious security vulnerability ever found by AI, and said it would have been too complex to find without AI. OpenAI said in a statement that, given the severity of the flaw and the widespread use of PHP, it assessed the issue as one of the most consequential security vulnerabilities in recent memory.
Patch Details Leak Ahead of Release, Leaving a Six-Hour Gap

The rollout of the patch has also drawn criticism. PHP developers had initially planned to release the security fix on the 22nd, but moved the schedule up by a day after related information leaked on an online message board on the 20th.
The PHP Foundation said on the 21st that Chainguard, a patch distribution company, abruptly published patched images more than six hours ahead of the official release time. With no formal update yet available, that gave hackers a six-hour head start to analyze the code, exposing users to attacks they could do nothing about. The foundation said in an official statement that Chainguard unilaterally broke the embargo and that the move disregarded weeks of work by numerous parties toward a coordinated disclosure.
PHP developers had originally intended to distribute the patch on the 22nd, but advanced the timeline by a day after details of the vulnerability began circulating online again on the 20th. The foundation also noted that another security firm, Calif, mistakenly posted and then deleted a video demonstrating an attack using the vulnerability, accelerating the development of hacking tools. The failure of coordination is all the more costly because advances in AI tools have made reverse-engineering patch code to build attack tools far faster than in the past.
It has also emerged that PHP developers detected signs of some of the flaws involved during an external security audit in 2024, but that patch work stalled amid difficulty reaching internal agreement and concerns about compatibility with existing programs.
Governments Worldwide Tell Operators to Take Sites Offline If Needed

Government agencies in some European countries, including the Netherlands and Finland, suspended website operations as a precaution, while cybersecurity authorities in Europe, Japan and Australia issued urgent update advisories.
The European Union said website operators should consider taking sites offline if applying the security patch is not feasible. In the Netherlands, several state agencies took public-facing websites offline following guidance from the National Cyber Security Centre, Reuters reported. Services were suspended at the Port of Rotterdam, Europe's largest port, as well as the government portal Overheid.nl, the Royal Dutch Football Association, major political party websites and major hospital websites. In Finland, government public network services were also taken offline as a precautionary measure, causing widespread outages. Preemptive website shutdowns have continued in Denmark and Finland as well.
U.S. authorities also urged operators to take websites offline on the 21st. The National Security Agency said on X, formerly Twitter, that it recommends all agencies and companies using PHP in their systems prepare to apply updates addressing the two critical vulnerabilities. "These vulnerabilities often provide a direct path to a server's file system or database," the NSA said, adding that if immediate updating is not possible, it recommends taking the affected systems offline until the vulnerabilities are fully resolved.
The Federal Bureau of Investigation also warned that malicious actors could execute code remotely through PHP, the programming language that powers websites and web applications. The FBI said the risk of sensitive data and networks being compromised had increased, and recommended that operators take websites offline if they cannot update immediately.
Prime Minister Sanae Takaichi said on X on the night of the 21st that the matter was extremely urgent, asking operators to check whether their websites use PHP and to prepare to apply the fix, due to be released at 11 p.m. that night, as quickly as possible. She added that if the patch cannot be applied quickly, temporarily suspending websites could be one effective way to reduce the risk. Japan's Ministry of Finance said the previous day that it had temporarily suspended some content and services on its website for emergency checks and to apply the fix.