
ⓘ France 24
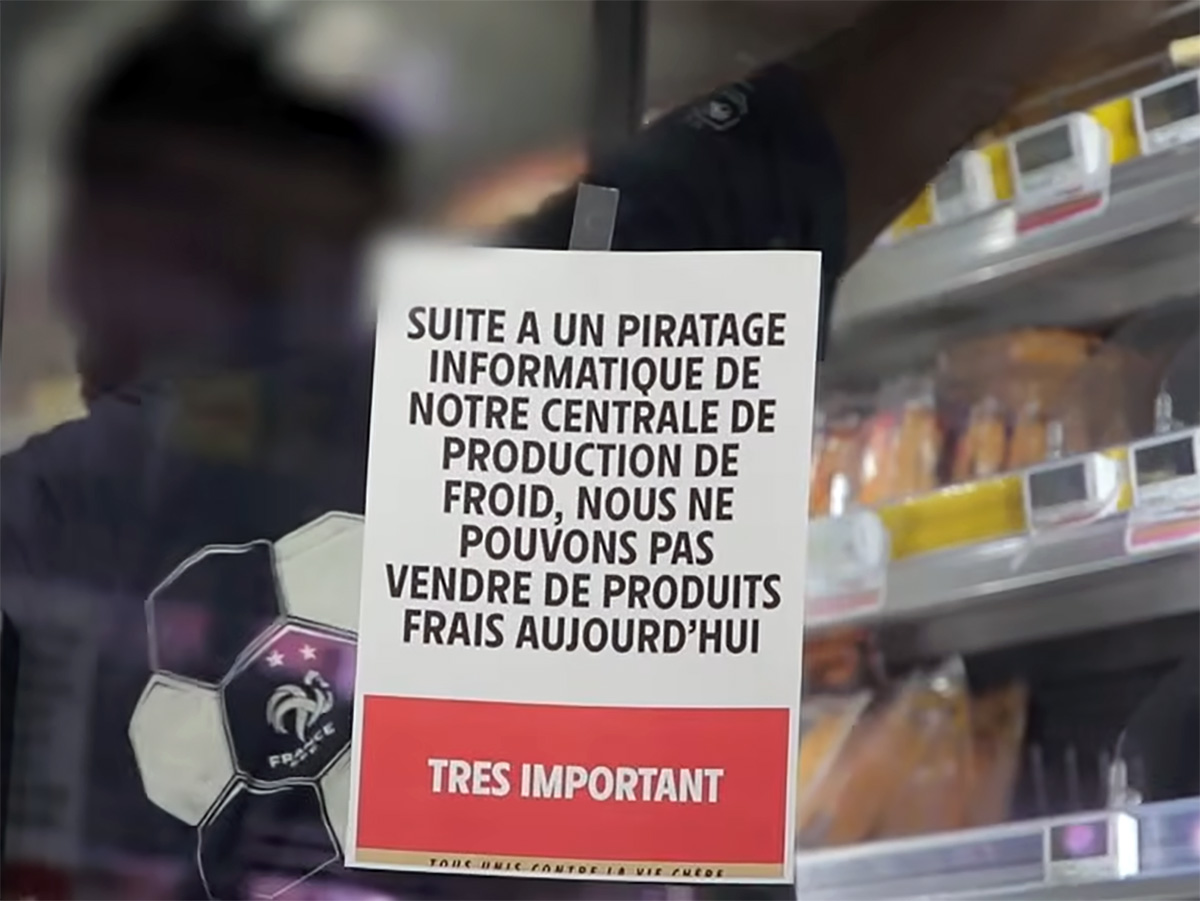
Hacking attacks on public infrastructure have taken a rather unexpected twist. This time around, the target was supermarket chain refrigerators whose controllers raised the temperature inside to spoil the food.
In what can only be described as a grave new threat to the food supply chain, malicious actors hacked the smart temperature controllers of a big supermarket chain in France, and all the food had to be thrown out.
Food waste losses amounted to tens of millions of euros, but the monetary consequences are not what put the French cyberdefence authorities on high alert.
On the night of October 11, attackers took over refrigeration controllers at hundreds of French supermarkets and pushed fridges and freezers into defrost mode, with temperatures reportedly hitting 50°C. Intermarché owner Les Mousquetaires says affected stores had to bin everything concerned, and its boss expects losses in the tens of millions of euros. Carrefour, Coopérative U, Monoprix, and E.Leclerc were also hit, though some chains say quick staff reactions saved most of their stock.
The way in was the remote controller that runs a store's cooling, mainly Danfoss AK-SM and AK-SC models that refrigeration contractors manage over the internet. Danfoss says the majority are older hardware that no longer gets updates. France's CERT-FR has since added Copeland xWeb and Dixell xWeb devices to its alert. It also warns that a factory reset on an unsupported kit is pointless, because the device will simply be compromised again. Nobody has claimed responsibility, and how the attackers got in remains unconfirmed as of the moment.
Hackers, however, target precisely such forgotten hardware with a management page sitting on the open internet, probably installed years ago by a contractor who never thought about it again. Claroty researchers warned in August about thousands of exposed Danfoss interfaces, and Danfoss itself has noted similar attacks on supermarkets in Russia and Israel back in 2022.
The food supply angle, however, makes the hack a real threat as supermarkets run on thin margins and tight stock rotation, and spoiled food can't be replaced overnight. Hitting stores in an enemy capital will lead to empty shelves, for instance, and Reuters cites an analyst saying Spain, Portugal, Poland, Germany, and Belgium saw cases too.
For now, such hacking attacks on public infrastructure feel more like a proof of concept that tests the capabilities and the reaction. In 2021, an attacker reached the Oldsmar water plant in Florida and tried to raise lye levels, and only an operator watching the cursor move stopped it. Ukraine's grid went dark for around 230,000 customers in 2015. Colonial Pipeline and meatpacker JBS ground to a halt then, too, thanks to ransomware, and the US East Coast felt the fuel shortages.
The culprit in all cases seems to be exposed, poorly protected systems with mundane fixes that often get overlooked. Cyberanalysts suggest pulling controllers off the public internet, putting remote access behind a VPN, and replacing obsolete connected gear instead of hoping for the best, even if it is still working fine.