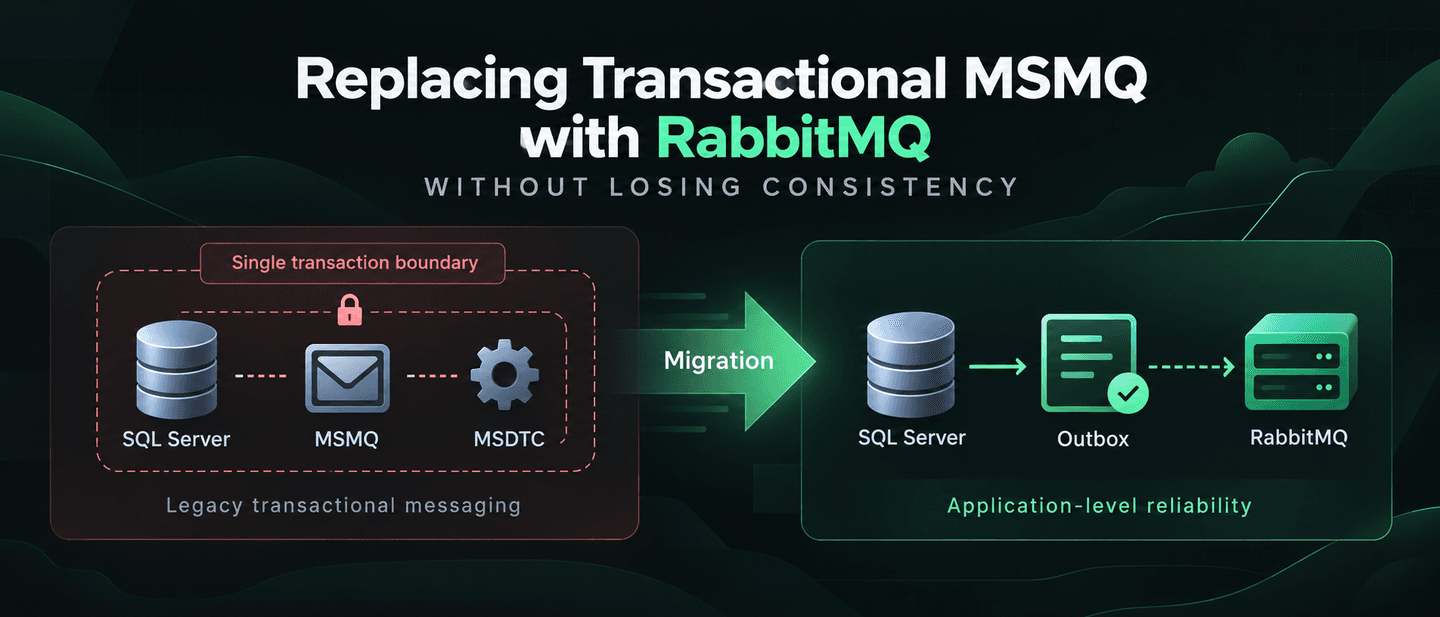
Replacing MSMQ with RabbitMQ may look like a straightforward transport migration. In applications that rely on WCF, SQL Server, and distributed transactions, however, it can also change the application's consistency model. RabbitMQ does not participate in the same ambient TransactionScope as SQL Server, so guarantees that were previously provided by the infrastructure have to become explicit parts of the application architecture.
This article compares three implementations of the same business flow: transactional MSMQ, a naive RabbitMQ replacement, and RabbitMQ with a transactional outbox. We will look at where a direct replacement breaks atomicity, why simply changing the order of database commit and message publication does not solve the problem, and how outbox, publisher confirms, retries, and idempotent consumers form a different reliability model.
Why This Migration Is Harder Than It Looks
Many long-lived .NET enterprise applications were built around Windows-centric technologies such as .NET Framework, IIS, WCF, MSMQ, and MSDTC. These technologies can still be appropriate in environments designed around them, but their platform coupling can limit future deployment and architecture options when teams move toward Linux containers, automated delivery, cloud-native infrastructure, or independently deployed services.
One of the less obvious risks in such migrations is the loss of reliability guarantees that application code previously received from the infrastructure. This article focuses on one example: replacing WCF/MSMQ transactional messaging with RabbitMQ while preserving business consistency.
Modernization Strategy: Isolate Messaging Before Migrating the Runtime
It can be tempting to treat a large modernization program as one rewrite: upgrade the runtime, replace infrastructure, change the deployment topology, and redesign transaction handling at the same time. In practice, combining unrelated changes increases the number of failure modes and makes it harder to identify which architectural assumption was broken.
The sample used in this article intentionally takes a narrower path. It remains on .NET Framework 4.8.1 and changes only the messaging strategy. Once the application no longer depends on WCF/MSMQ transactional messaging, a later migration to modern .NET becomes a separate step.
The sample exposes the same business flow through three messaging modes:
- msmq - the legacy WCF/MSMQ baseline with distributed transaction support
- rabbit-naive - a direct RabbitMQ replacement that preserves the call site but not the transaction semantics
- rabbit-outbox - RabbitMQ publishing through a transactional outbox
At the application boundary, the code depends on a deliberately small abstraction:
internal interface IMessagePublisher
{
    void Publish(MessageEnvelope message);
}
The business flow can be simplified to:
Begin TransactionScope
  Insert business record into SQL Server
  Publish BusinessRecordCreated message
Complete transaction
Only the implementation of IMessagePublisher changes. Keeping the application flow stable makes the consistency differences easier to observe and keeps the sample focused on the migration problem rather than on unrelated refactoring.
The msmq-rabbitmq-consistency repository contains the sample application and the three messaging modes used throughout the article. Keeping the code next to the narrative makes it possible to reproduce the behavior discussed in the following sections and compare the implementations directly.
Legacy Baseline: WCF and Transactional MSMQ
The baseline uses WCF over a transactional MSMQ queue. In this architecture, SQL Server and MSMQ can enlist as durable resources in a transaction coordinated by System.Transactions and MSDTC. Microsoft documents System.Transactions as supporting SQL Server, MSMQ, and escalation to MSDTC when multiple durable resources participate.
Conceptually, the producer performs:
Begin TransactionScope
  Insert row into SQL Server
  Send message to transactional MSMQ queue
Complete transaction
If both resources are correctly enlisted and the TransactionScope completes, the database change and the message send are committed together. If the application fails before completion, both can be rolled back.
The consumer side can also use a transactional receive. WCF can receive an MSMQ message inside a transaction and execute database work in the same local handling transaction. If message handling fails, the queue receive is not committed and the message can be delivered again.
An important nuance is that the producer and consumer do not share one end-to-end transaction. The sender has a transaction around its local database write and queue send; the receiver has a separate transaction around queue receive and its own resource updates. WCF/MSMQ hides much of this coordination from business code, which is one reason the programming model feels deceptively simple.
Why a Direct RabbitMQ Replacement Changes the Consistency Model
The first migration attempt can look almost identical to the MSMQ implementation: keep TransactionScope, save the business record, and publish to RabbitMQ.
Begin TransactionScope
  Insert row into SQL Server
  Publish message to RabbitMQ
Complete transaction
The code shape is similar, but the semantics are not. The SQL operation is controlled by TransactionScope; the RabbitMQ publish is not. The application now performs two independent writes to two different systems.
Failure order A: publish before the database commit
Begin TransactionScope
  Insert row into SQL Server
  Publish message to RabbitMQ
  Application fails before transaction commit
Rollback SQL transaction
RabbitMQ may already have accepted the message while the SQL transaction later rolls back. A consumer can therefore observe an event for a business record that never becomes committed. Even when the SQL transaction eventually commits, a fast consumer may receive the message before the corresponding database change becomes visible to it.
Failure order B: commit the database first
A natural reaction is to move publishing after the database commit. That prevents a message from escaping a transaction that later rolls back, but it creates the opposite failure window:
Commit SQL transaction
Application crashes or RabbitMQ is unavailable
Publish message fails
Now the business state is committed, but the event that should describe that state change is missing. Retrying the whole business operation may be unsafe because the database update has already succeeded.
The dual-write problem: Publishing before the commit can create a message without committed business data. Publishing after the commit can create committed business data without a message. Changing the order does not make two independent resource updates atomic.
This is the critical migration gap. Replacing MSMQ with RabbitMQ is not merely a change of transport API; it changes the consistency model of the application.
A Production Symptom: Waiting for the Database
This failure mode is not only theoretical. I have encountered production code where a consumer compensated for the race by repeatedly querying the database, sleeping for a fixed interval, and retrying until the record referenced by the message became visible.
Such a workaround can hide one particular timing problem - message delivery before the producer transaction becomes visible - but it does not restore atomicity. If the producer transaction later rolls back, the expected row will never appear. Even when it commits, correctness now depends on timing, retry intervals, and timeout policy rather than on an explicit consistency guarantee. The workaround treats a symptom of the changed consistency model instead of addressing the dual-write problem itself.
Transactional Outbox: Move the Reliable Write Into the Database
The transactional outbox changes the problem instead of trying to make RabbitMQ participate in the SQL transaction. The application writes both the business change and a description of the outgoing message in the same database transaction.
Begin local database transaction
  Insert business record into SQL Server
  Insert message into OutboxMessages
Commit transaction
Because both writes are in the same database, they share one local transaction boundary. If the transaction rolls back, neither the business row nor the outbox row remains. If it commits, both are durable.
A separate dispatcher reads committed outbox rows and publishes them to RabbitMQ:
Read unpublished outbox records
Publish each message to RabbitMQ
Wait for broker confirmation
Mark the outbox record as published
The database becomes the source of truth for the business operation and for the intent to publish. RabbitMQ delivery happens later, outside the business transaction. The architecture is now explicitly based on eventual consistency rather than pretending that the broker participates in the database transaction.
The Dispatcher Gap and At-Least-Once Publishing
The outbox removes the atomicity gap between business data and the decision to publish, but the dispatcher still performs two operations: send the message and record that the send succeeded. That creates a smaller but unavoidable failure window.
Dispatcher reads an unpublished row
Dispatcher publishes the message
RabbitMQ confirms the publish
Dispatcher crashes before marking the row as published
Application restarts
Dispatcher publishes the same row again
The message is not lost, but it may be published more than once. For that reason, a production outbox is commonly designed for at-least-once publication rather than relying on an end-to-end exactly-once assumption.
Publisher confirms are important here. A successful client method call or a socket write alone is not sufficient evidence that the broker durably accepted a message. RabbitMQ documents publisher confirms specifically as a publisher-side data-safety mechanism.
A robust dispatcher therefore retries failed sends and marks an outbox row as published only after the required broker confirmation. The trade-off is duplicate delivery, which moves the next reliability requirement to consumers.
Idempotent Consumers and the Inbox Pattern
If the same logical message can arrive more than once, consumers must ensure that repeated delivery does not repeat the business effect.
The sample uses a ProcessedMessages table keyed by MessageId. The business update and the processed-message marker are written in the same local database transaction:
Begin local transaction
  If MessageId already exists in ProcessedMessages:
    Commit
    Acknowledge broker message
    Return

  Apply business changes
  Insert MessageId into ProcessedMessages
Commit
Acknowledge broker message
If the consumer commits its database transaction and crashes before acknowledging RabbitMQ, the broker can redeliver the message. On the next attempt, the consumer finds the existing MessageId and skips the business effect.
This mechanism is often described as an inbox or duplicate-detection pattern. Storing MessageId is not the only possible idempotency strategy - some operations are naturally idempotent - but the important architectural requirement is the same: a retry must not corrupt business state.
This is the core shift away from the MSMQ/MSDTC model. Reliability is no longer obtained by coordinating every resource in one distributed transaction. It is assembled from local atomic transactions, durable intent, retry, broker acknowledgements, and idempotent processing.
Production Considerations
The dispatcher in a teaching sample should remain intentionally small. A production implementation has to address several additional concerns:
- row claiming or locking when multiple dispatcher instances run concurrently
- retry policies with backoff and a clear policy for permanently failing messages
- RabbitMQ publisher confirms before an outbox record is considered dispatched
- message ordering where business semantics require per-aggregate or per-stream ordering
- dead-letter or poison-message handling
- metrics, tracing, alerting, and visibility into outbox backlog
- cleanup or archival of old outbox and inbox records
- message schema evolution and serialization compatibility
- batching and throughput controls so the outbox does not become a database bottleneck
- a documented idempotency strategy for every consumer with non-transactional side effects
For example, multiple workers may claim rows in parallel to improve throughput, but they should avoid uncontrolled concurrent publication of the same record. If ordering matters for a particular entity, parallelism must be constrained accordingly. A failed broker publish should be retried with backoff, while a confirmed publish should not be marked as sent until the confirmation has been observed.
These details are deliberately outside the minimal implementation. The sample is intended to explain the architecture, not to become another messaging framework.
Framework-Assisted Implementations
Production systems rarely implement every reliability mechanism from scratch. Mature .NET messaging frameworks such as MassTransit, NServiceBus, and Wolverine provide built-in support for outbox/inbox patterns, retries, duplicate detection, and related operational concerns.
These frameworks do not restore the old MSDTC-based transaction model. The underlying architecture is still different: business data and the intent to publish are committed locally, while message delivery happens later and may be retried.
The companion repository includes a .NET 8 example using MassTransit with RabbitMQ and EF Core to demonstrate a framework-assisted outbox/inbox implementation.
The manual implementation remains useful because it exposes the actual failure windows and trade-offs. Once those mechanics are understood, a framework can automate much of the infrastructure without hiding the consistency model itself.
A Practical Staged Migration Path
One possible migration sequence is:
- Identify where business transactions currently depend on transactional MSMQ behavior.
- Introduce a messaging abstraction so business code does not depend directly on WCF/MSMQ.
- Replace direct MSMQ publishing with RabbitMQ plus an outbox-based reliability model.
- Adopt a mature messaging framework where its operational features justify the dependency.
- Migrate the application runtime and deployment model to modern .NET as a separate iteration.
This order is not universal. Some systems can migrate the runtime first; others are better candidates for a strangler approach or for extracting new services around a stable legacy core. The important principle is to make the reliability model explicit before changing infrastructure that used to provide hidden guarantees.
Conclusion
Enterprise modernization is rarely a sequence of mechanical package upgrades. Infrastructure choices encode behavioral guarantees, and changing those choices can silently change application correctness.
The WCF/MSMQ baseline in this article could coordinate SQL Server and a transactional queue through System.Transactions and MSDTC. A direct RabbitMQ replacement preserves the shape of the code but not that atomicity. Publishing before the database commit risks messages for rolled-back state; publishing after the commit risks committed state without a message.
The transactional outbox resolves this dual-write problem by moving the reliable decision to publish into the same local database transaction as the business data. The cost is a different consistency model: asynchronous dispatch, eventual consistency, retries, and possible duplicate delivery. Idempotent consumers are therefore part of the design, not an optional optimization.
The broader lesson is not that distributed transactions are universally wrong or that every legacy system must be rewritten. It is that modernization must preserve business correctness while the technical foundation changes. When a platform-level guarantee disappears, the replacement architecture must make that guarantee - or its new equivalent - explicit.
For many long-lived enterprise applications, separating the replacement of transactional messaging from the runtime migration can reduce risk and make the transition easier to test. It turns a large rewrite into a sequence of smaller architectural changes whose failure modes can be understood independently.