HIGH-RISK VULNERABILITIES: PHP, Go and Node.js issued updates after finding security loopholes, such as the ability to remotely execute code and risks related to stolen keys
By Shelley Shan / Staff reporter


The Administration for Cybersecurity yesterday urged government agencies and businesses to immediately install security updates for PHP, Node.js and Go after developers disclosed vulnerabilities that could allow attackers to remotely execute code or intercept digital certificates.
All three are open-source software: PHP is a server-side scripting language, Node.js is a JavaScript runtime environment and Go is a programming language.
Emergency safety updates for PHP and Node.js were issued on Wednesday, while updated versions for Go were issued on Monday, the agency said.
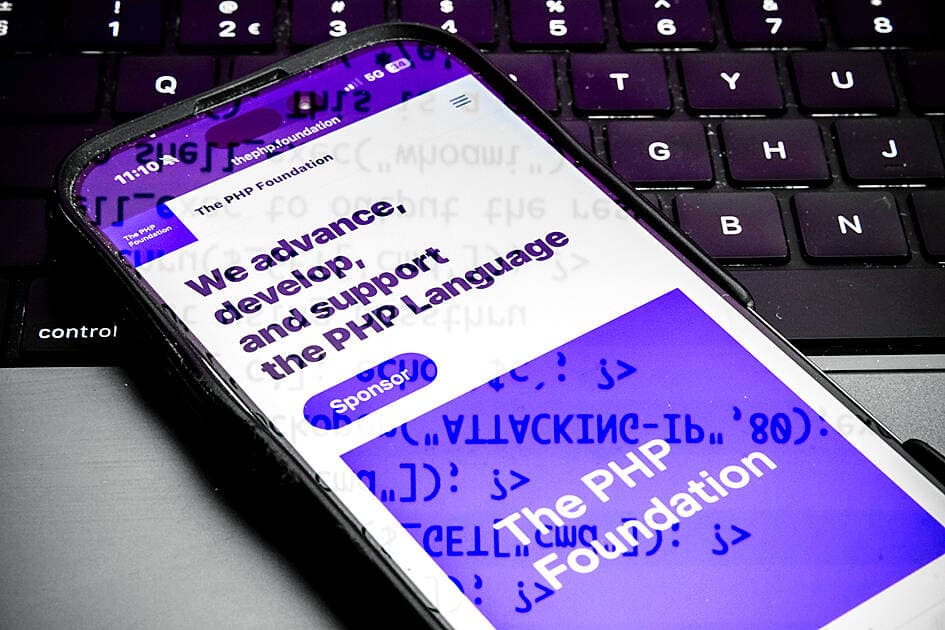
The Web site of The PHP Foundation is displayed on a mobile phone in Mierlo, Netherlands, on Wednesday.
Photo: EPA
The PHP safety team identified two security loopholes, with the vulnerabilities rated 9.2 out of 10 under the CVSS v4.0 scoring system, it added.
PHP is used extensively for Web sites, content management systems and administrative interfaces, the agency said, adding that the loopholes could allow hackers to remotely execute arbitrary code without authentication.
Systems such as WordPress, Drupal, Joomla and Magento also rely on PHP, it added.
In response to the potential threat, the agency said it has notified concerned organizations through cybersecurity alerts, the National Information Sharing and Analysis Center, and the Taiwan Computer Emergency Response Team/Coordination Center.
Government agencies and businesses are advised to scrutinize all PHP-based systems and related packages, check their versions and apply patches in accordance with vendor advisories, it said.
After updating, they should review system logs and unusual access, and verify the security of involved accounts and credentials if suspicious activity is detected, it added.
Node.js issued three updated versions after patching 10 loopholes, four of which were rated as high-risk vulnerabilities.
The main security loophole affects the Brotli decoder and involves an out-of-bound write that could cause memory corruption and potentially lead to remote code execution, it said.
Other issues addressed included TLS certificate validation bypasses, DNS resolution errors and permission model bypasses, the agency said.
“We urge organizations to check their servers and docker image, and upgrade to secure versions as soon as possible,” it said.
Go offered two updated versions following a recent security incident in an Indian intermediate certificate authority, which exposed eight known private keys.
The stolen keys could be used by hackers to launch man-in-the-middle attacks, the agency said.
The new Go versions add the affected intermediate certificates to a blocklist to reduce the risk of abuse of the certificate trust chain, it said.
Developers using the programming language must recompile and redeploy applications after updating the Go toolchain for the certificate-blocking mechanism to take effect, the agency said, adding that updating only the development or runtime environment is not sufficient.