
By: John Leicester And Mike Corder, The Associated Press Posted:
- Read Later
PARIS (AP) — France’s cybersecurity authority has warned that a cyberattack targeting supermarkets may still be ongoing as stores restocked Wednesday after the attack sent refrigerator temperatures soaring, raising concerns about the security of vital food supply chains.
Read this article for free:
To continue reading, please subscribe:
*First annual payment billed as $205.00 + GST for one year. This annual subscription will automatically renew at $233.00 + GST every 52 weeks (10% off the regular annual price of $259.35). Offer available to new and qualified returning subscribers only. Cancel any time.
PARIS (AP) — France’s cybersecurity authority has warned that a cyberattack targeting supermarkets may still be ongoing as stores restocked Wednesday after the attack sent refrigerator temperatures soaring, raising concerns about the security of vital food supply chains.
Read unlimited articles for free today:
PARIS (AP) — France’s cybersecurity authority has warned that a cyberattack targeting supermarkets may still be ongoing as stores restocked Wednesday after the attack sent refrigerator temperatures soaring, raising concerns about the security of vital food supply chains.
The agency said Tuesday night that the attacks were “likely still underway.” It urged stores to reconnect refrigerators to the internet only through a secure VPN connection or protected network, install firmware updates and change passwords.
Attackers remotely took control of refrigeration systems in hundreds of supermarkets and independent stores across France in the early hours of Monday. Temperatures reached 50 degrees Celsius (122 degrees Fahrenheit) for about six hours, forcing stores to discard fresh and frozen goods. The Intermarché supermarket chain reported losses of “tens of millions of euros” in a single day.
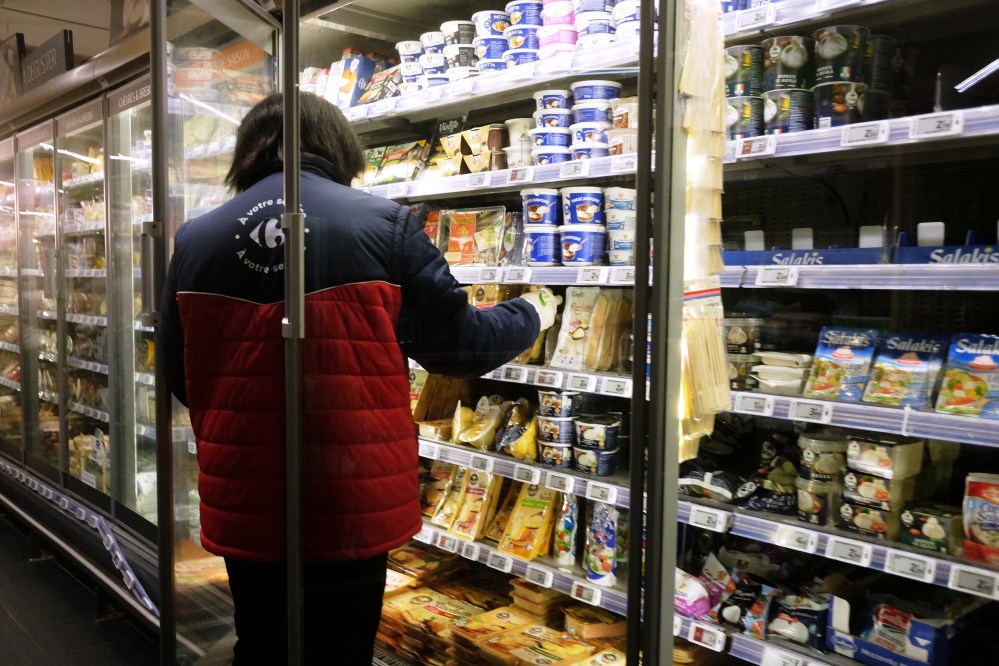
In the Netherlands, a major supermarket chain was restarting systems it had shut down as a precaution amid what parent company Ahold Delhaize called a “cybersecurity incident.” The incident halted home deliveries and disrupted some supplies to its extensive network of stores across the country.
Authorities in both countries were investigating the cyber incidents, which exposed vulnerabilities in some older refrigeration management systems and in the countries’ highly efficient food supply chains.
Cybersecurity authorities and Europol investigate
The Dutch National cybersecurity Center said several cyber incidents had affected Europe’s food sector, but it saw “no reason at this time to believe that these incidents are linked.”
The European Union’s police agency, Europol, confirmed to The Associated Press that it was in contact with authorities in the affected countries but declined to give details, citing an ongoing investigation.
No perpetrators have been publicly identified, and no claims of responsibility have been made public.
François Deruty, a former operations director at the French Cybersecurity Agency, said those responsible could range from sophisticated state-sponsored actors to a disgruntled French student. Protests by high school students angry about dilapidated, understaffed schools have roiled France since mid-September.
“I still can’t determine whether it’s being directed by someone or whether it’s an individual trying to take advantage of the prevailing chaos to show off their skills or send a message,” said Deruty, who is now chief intelligence officer at cybersecurity company Sekoia.
“I’m somewhat struck by the timing and the fact that politicians already have enough issues to deal with in France right now,” he added. “This adds another — one that not everyone will necessarily understand technically, but that resonates with all citizens in their everyday lives.”
An early morning alarm saved one Paris supermarket’s fresh supplies
A 4 a.m. alert sent to one of Antony Bohne’s suppliers saved most of his fresh fruit and vegetables. For his frozen food, it was already too late — his freezers’ temperature had already spiked to nearly 40 degrees Celsius (104 degrees Fahrenheit).
“Unfortunately, we couldn’t save those products,” said Bohne, director of Intermarché La Villette in Paris.
In the Netherlands, trays usually brimming with fresh tomatoes lay empty on Wednesday in an Albert Heijn supermarket on the outskirts of The Hague. Elsewhere in the store, staff were busy stocking shelves, and most products were in plentiful supply.
Pieter Zwaan, a senior researcher at the respected Clingendael Institute, recently co-authored a report on food supplies in the Netherlands, where supermarkets rely on “just in time” deliveries multiple times each day to keep shelves filled.
“Without IT and electricity it is impossible to order and deliver product to supermarkets” so frequently, he said.
To mitigate the risks of a prolonged supply chain disruption, the report recommended Dutch households build up reserves that would keep food on the table for eight days — the current government recommendation is a three-day stockpile.
In France, the hack is seen as a cybersecurity wake-up call
French Finance Minister Roland Lescure said that about 700 of the country’s 10,000 supermarkets were affected. He said there was no risk to France’s food supplies but acknowledged that the attack “touches the heart of our food security” and called it a “wake-up call for everyone.”
Deruty said that software vulnerabilities exploited in the hack in France “are an accident waiting to happen” and that “people simply hadn’t patched their equipment” with security updates.
While awareness of cyber risks has grown considerably in recent years, it still hasn’t filtered down to everybody.
“There are still people who will be surprised and say: ‘I run a franchise store. Why would I be a target for a cyberattack?’” Deruty said.
French attack targeted older systems
The French cybersecurity agency said Tuesday it was “aware of numerous compromises” involving refrigeration system remote control modules made by Danish company Danfoss as well as U.S.-based Copeland.
Danfoss has said that most affected systems in France were older products that no longer received software or security updates, and that it is working with affected customers to limit the damage.
In an August report, U.S. cybersecurity firm Claroty identified vulnerabilities in the Danfoss AK-SM 800A and Copeland XWeb Pro platforms, which are used to manage refrigeration infrastructure in supermarkets, warehouses and other facilities.
For example, Claroty said “numerous controllers” using the Danfoss system were directly accessible from the public internet, leaving them wide-open for cyberattacks. But it noted that Danfoss and Copeland had since fixed the vulnerabilities.
Copeland said Tuesday that a vulnerability had been identified in “a discontinued, end-of-life generation of controllers,” and that it was working with impacted customers.
___
Corder reported from The Hague, Netherlands. Associated Press Business Writers Dee-Ann Durbin in Detroit and Barbara Ortutay in San Francisco contributed.
- Read Later