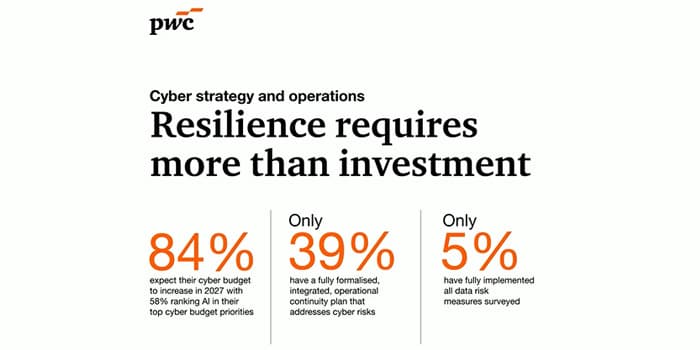
Organisations are doubling down on their cyber investment amid rapid advances in AI, with more than four-fifths [84%] of security and finance leaders expecting cyber budgets to increase – up from 78% last year – according to PwC’s 2027 Global Digital Trust Insights Survey.
A spokesperson said, “The survey, which captured the views of almost 4,000 business and tech executives across 71 countries and territories, finds that as frontier AI models are rolled out, almost two-thirds [58%] of security leaders rank AI in their top cyber budget priorities for the year ahead.
“This comes as less than two-fifths [39%] of security, risk and operations leaders have a fully formalised and integrated operational continuity plan that specifically addresses cyber risks altogether.
“When asked specifically about the cyber threats organisations are least prepared to address, half [50%] of security leaders identify attacks targeting AI systems amongst their top threats – ahead of cloud-related threats [40%], third-party breaches [34%] and ransomware [33%].”
Chris Mills, Partner, Risk Advisory, PwC Bermuda, said: “Cybersecurity needs to be embedded in C-suite decision-making from the outset. The survey shows that many organisations remain underprepared for an increasingly complex and fast-changing cyber landscape. Organisations that strengthen cyber readiness today will be better equipped to adapt, innovate and compete with confidence.”
Anthony Fellowes, Director, Digital, PwC Bermuda stated, “AI is reshaping both sides of the cyber equation. While it introduces new risks and broadens the attack surface, it also has the potential to significantly enhance how organisations defend themselves. The challenge is not whether to adopt AI, but how to do so in a way that builds confidence, strengthens security and delivers meaningful business outcomes.”
Cyber resilience will require C-suite elevation
The spokesperson said, “Even in the face of rising frontier AI vulnerabilities, companies have only implemented, on average, three out of seven key data-risk measures across their organisations. What’s more, only 5% of those surveyed have fully implemented every data risk measure surveyed – down from 7% last year.
“While one-third [33%] of CEOs and security and risk leaders say their organisations have established dedicated AI roles, including a chief AI officer or AI board, less than half strongly agree that cyber risk is a standing agenda item at the board level [47%] or at executive leadership meetings [45%].
Unlocking AI’s defensive potential
“As cyber-attacks accelerate beyond human speed, AI is becoming an essential force multiplier for security teams. However, trust remains low – particularly around using autonomous AI agents.
“This comes as compromise by autonomous botnets [53%], adversarial attacks [52%], and data poisoning [52%] rank among the top AI-enabled attacks that security and risk leaders say they are least prepared to address.
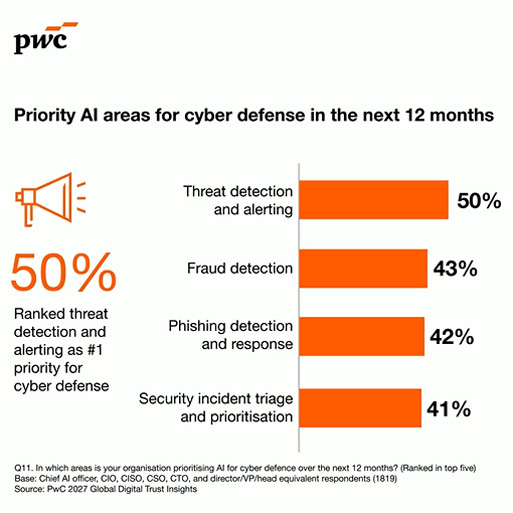
“While security leaders rank threat detection and alerting [50%] and phishing detection and response [42%] among the top priority AI areas for cyber defence – roughly only one-fifth [22%] would authorise fully autonomous execution by AI agents for cyber defence.
“Rapid advances in AI, however, are proving problematic. More than half [55%] rank reliability and maturity of AI technology among their top three barriers to increasing AI agent autonomy in security operations, while 46% cite accountability and explainability in AI decision-making.
“Nearly half of CISOs [44%] identify workforce skills in AI oversight and governance as one of their top barriers to increasing AI agent autonomy.
Bolstering cyber resilience in the age of AI
“As organisations contend with a new frontier of cyber risks, they are taking action.
“More than half [54%] of security and risk leaders are adopting multi-cloud or hybrid cloud strategies, while others are strengthening regional data and tech redundancy [47%] and localising infrastructure within specific jurisdictions [37%] to reduce concentration risk across their value chain.
“As geopolitics shapes the cyber risk landscape, half [50%] are also making changes to vendor, third-party and supply chain risk management.
“As cyber budgets take centre-stage, some companies are bringing in managed services to help – with artificial intelligence [53%] the leading focus area as organisations confront a shortage of specialist cyber and AI talent.
“If organisations are to insulate their businesses against rapidly evolving AI and cyber threats, they must:
- Strengthen cyber governance, accountability and risk decision-making;
- Protect critical operations and build cyber resilience;
- Secure data, AI and emerging technology;
- Manage ecosystem, third-party and technology concentration risk;
- Use trusted technology and data to create enterprise value;
- Build the model to effectively leverage agents to defend against agent-enabled attacks.”
Read More About
#BermudaBusiness #CyberSecurity
Category: All, Business, technology