The South Korean government has launched an emergency response after a critical security vulnerability was found in PHP, a programming language used by a large share of websites worldwide.
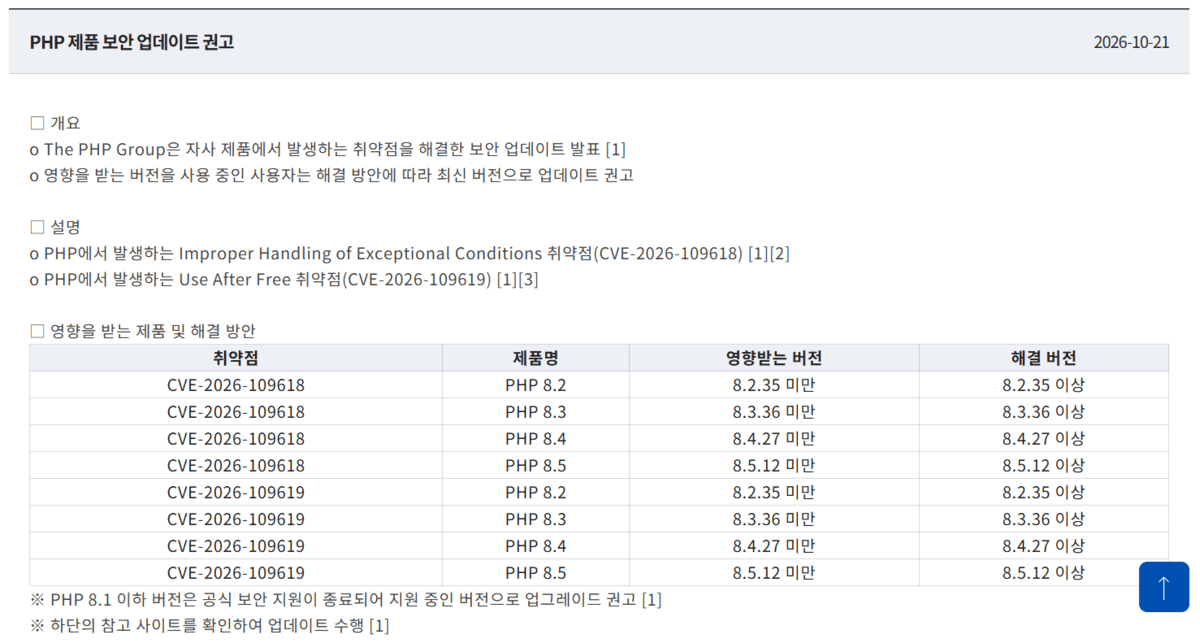
The Ministry of Science and ICT (MSIT) and the Korea Internet & Security Agency (KISA) on the night of the 21st asked members of the Cyber Threat Analysis & Sharing system (C-TAS), which includes about 5,900 institutions and companies in Korea, as well as roughly 30,000 firms required to report a chief information security officer (CISO), to take security measures against the PHP vulnerability, according to relevant government agencies on the 22nd.
The vulnerability disclosed by PHP could allow an attacker to run arbitrary code from outside or take control of a system without any login or authentication, officials said. PHP developers released a new version on the 21st that urgently fixes the two related vulnerabilities.
"We understand that many websites in Korea are also using PHP," an MSIT official said. "We have notified the companies concerned of security measures, and we are reviewing support such as emergency patching for small and medium-sized enterprises."
About 75% of websites whose programming language can be identified use PHP, according to web technology survey firm W3Techs. WordPress, used by about 43% of all websites, also runs on PHP. The vulnerability was reportedly discovered by cybersecurity firm Calif using OpenAI's artificial intelligence model GPT-5.6 Sol.