
The sovereign AI market is growing fast, but many providers cannot prove their sovereignty claims. A new report from research firm Omdia found that 28% of providers disclose no proof of sovereignty at all. Some even expect enterprises to pay for their own audits to verify the claims.
Sovereign AI refers to AI infrastructure that a country or organization fully controls within its own borders. This includes the data, models, compute resources, and network pathways. The goal is to keep sensitive information under local jurisdiction and free from foreign government access.
Omdia evaluated 35 sovereign AI providers across 20 countries for its report, “Sovereign AI: A Playbook for Success.” The researchers examined terms of service, SLAs, data processing agreements, privacy practices, and certifications. Their findings reveal a market where “sovereign” often functions as a marketing label rather than a verified standard.
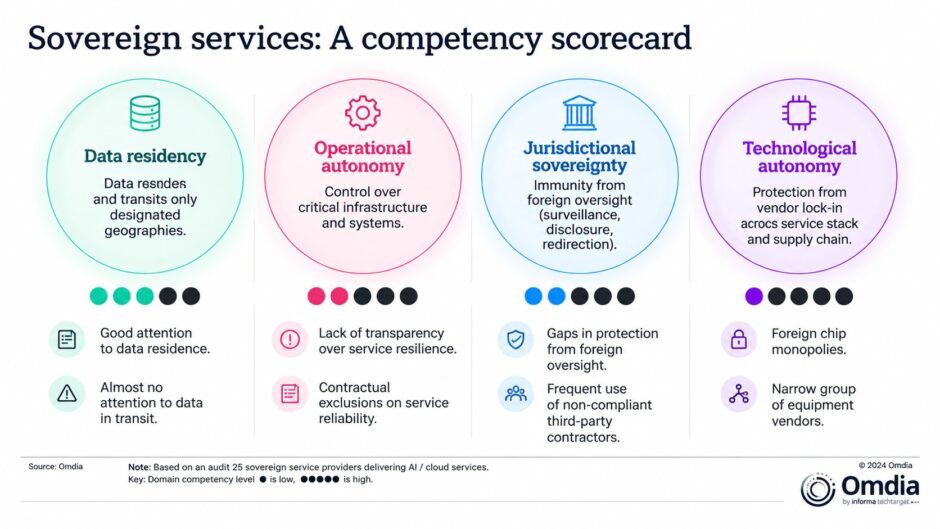
“No one is regulating who can call themselves a sovereign AI provider, and it shows,” said Camille Mendler, Research Director at Omdia. She also stressed that “local hosting is not sovereignty,” since data in transit must also remain under sovereign control.
The contract terms tell an equally concerning story. Eight in ten contracts state that network resilience falls outside the provider’s control. In addition, two-thirds of providers limit compensation for failures to service credits alone. “Best efforts” language appears throughout most agreements. As a result, enterprises carry most of the risk when things go wrong.
The global sovereign AI market stood at $41.1 billion in 2025 and could reach $258.7 billion by 2035 at a 20.2% compound annual growth rate. Government data residency rules and national compute procurement programs drive much of this growth. However, the rapid expansion has also attracted providers whose capabilities do not match their claims.
Interestingly, US-headquartered AI providers currently offer better transparency and contract terms than most local sovereign providers. India stands as a notable exception. Meanwhile, up to 45% of large enterprises plan to add or replace a supplier for sovereignty reasons within 18 months.
Small and medium-sized businesses face the greatest risk. Most lack the IT teams needed to properly examine sovereignty claims. Omdia recommends that providers invest in certification and trust centers to close this gap. The report also suggests publishing separate SLAs for connectivity and AI services.