
Staff Reporter
Published:
Photo by TECNIC Bioprocess Solutions on Unsplash
Blocking a tool removes it from your logs, not from your business.
Singapore has spent this year getting serious about how artificial intelligence (AI) gets governed. Infocomm Media Development Authority (IMDA) launched its Model AI Governance Framework for Agentic AI in January 2026, laying out what responsible deployment looks like now that software has moved from answering questions to taking actions on our behalf.
Yet walk into most Singapore offices, and the actual AI policy is still a blocklist.
That is not a fringe approach. A ThreatLabz 2026 AI Security report, which analysed nearly a trillion enterprise AI and machine learning transactions in 2025, found organisations blocked close to four in ten of them outright — and the tools employees use most were also the ones most heavily restricted.
I understand the instinct: if you can't govern it, block it. But leaders need to be honest about what a block actually buys them. Block an AI app on the corporate network, and a motivated employee pulls out a personal phone, photographs the screen, and pastes it into a consumer tool on a network you don't control. The data still leaves the building. You've just lost the ability to see it go.
PagerDuty's Shadow AI survey, published in June 2026, found two-thirds of office professionals had used AI tools at work they believed were not permitted. The block stopped none of it. It only stopped you from seeing it. Don't mistake a quieter log for a smaller problem.
Employees aren't being reckless. They're being efficient.
Motive matters, because it changes the fix. Nobody reaches for an unsanctioned AI tool to undermine their employer — they reach for it because the work gets done faster. When the sanctioned option is slower, more restricted, or doesn't exist at all, the personal device becomes the path of least resistance.
Singapore makes this especially acute. This is one of the most connected workforces anywhere, hybrid work is the norm, and nearly every employee carries a highly capable device that sits entirely outside corporate control. Singaporeans are also unusually bullish on AI: in a global study by the University of Melbourne and KPMG, more than eight in 10 here said they expect it to deliver real benefits.
Put a workforce that genuinely wants these tools next to an easy route around every control you have, and you get exactly what you'd expect.
That's a real problem, and worth solving. But it's not the whole problem. There's a bigger one hiding behind it: data can leave the building without a single employee getting involved.
The AI you already approved
The ThreatLabz report also found that one of the fastest-growing sources of enterprise AI risk isn't the tools people go looking for. It's the ones already humming inside software you bought years ago: summaries in the service desk, recommendations in the CRM, drafting in the productivity suite. These features were never classified as “AI applications,” so a filter built to catch AI applications never sees them. They arrive switched on, inherit whatever permissions you already granted, and read your business content as a matter of routine.
You cannot block your way out of this one. There's nothing separate to put on the list — the only thing left to block is the application itself, and nobody is switching off the CRM to keep AI out of it. In both cases, you're policing a category of tool whilst your data moves somewhere that category doesn't describe.
Most AI incidents aren't AI incidents
Controlling tools can't stop data from leaving. Controlling your data can. Which lands us on the least glamorous problem in enterprise IT: data classification.
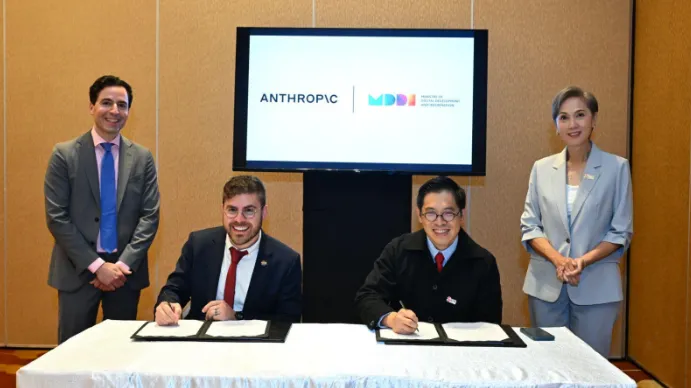
Consider what happened to Anthropic earlier this year. Nearly 3,000 of its own unpublished documents — including a draft announcement for an unreleased model — sat at publicly reachable web addresses. There was no attack, no adversarial prompt, no attacker of any kind. Anthropic's content management system gave every uploaded file a public URL by default unless someone manually marked it private. Nobody had.
If a company that builds frontier AI can lose control of its own material to a default setting, the problem was never AI. Had those documents been classified as restricted, the system's default would never have decided their fate — the protection would have travelled with the file. You can't protect what you haven't identified.
The realistic middle path
The choice isn't between blocking everything and permitting everything. Three things matter far more than where you draw that line.
Start with visibility. Find out what AI is actually running in your environment — which is rarely what was formally approved. That means the features quietly switched on inside platforms you already pay for, and the consumer tools people reach for on their own. You can't govern an inventory you don't have, and most organizations have never taken one.
Then classify. Decide which data is genuinely sensitive, which is routine, and which must never leave the organization. Much of this is automated now, so start with your highest-risk repositories, not your largest ones. Once data carries its own classification, the protection moves with it — whichever tool it ends up in, and whoever puts it there.
Then put guardrails on the tools you do sanction. Inspect what goes in and what comes out, so sensitive material gets caught in the prompt rather than discovered afterward. Build an assistant that holds its shape when someone tries to talk it into stepping outside its job — because people will try, so you have to design for it.
Get those three right, and the number of unsanctioned tools matters far less: you can see them, and the data is carrying its own rules wherever it goes. Then make the sanctioned option fast enough that the personal phone stops being the quicker route.
Convenience decides this fight — and it can decide it in your favour. Productivity isn't the enemy of governance here. It's the mechanism.
Join Singapore Business Review community
Also Read
Join Singapore Business Review community
A NOTE FROM SINGAPORE BUSINESS REVIEW
Reaching the people who run Asia's businesses is harder than it used to be.
Inboxes are crowded. Attention is short. The executives you most want to reach — the founders, CFOs, and operators who actually move budgets — are the hardest to find through the usual channels. If you're building a company, a category, or a reputation, you already know this.
We've spent twenty years building the room they read. Singapore Business Review is where senior decision makers in Singapore and across Southeast Asia come for business coverage they can't get elsewhere — in print, online, and in person at the summits and roundtables we host across seven markets.
If you have something these readers should know about — a point of view worth publishing, a product worth their attention, an event worth their time — we'd like to hear what you're trying to do.