Cyberattacks exploiting artificial intelligence have spread across industries following a string of hacking incidents at financial firms, prompting South Korean information technology companies to build preemptive defense systems that look beyond their own networks to vulnerabilities at outside partners and in software supply chains. Concerns have grown that open-source technology, accessible to developers worldwide, can serve as an entry point for hackers, and tools to block that route are emerging one after another. With public-sector AI transformation projects largely run through consortiums, analysts say security systems that extend beyond a single company are now urgently needed.
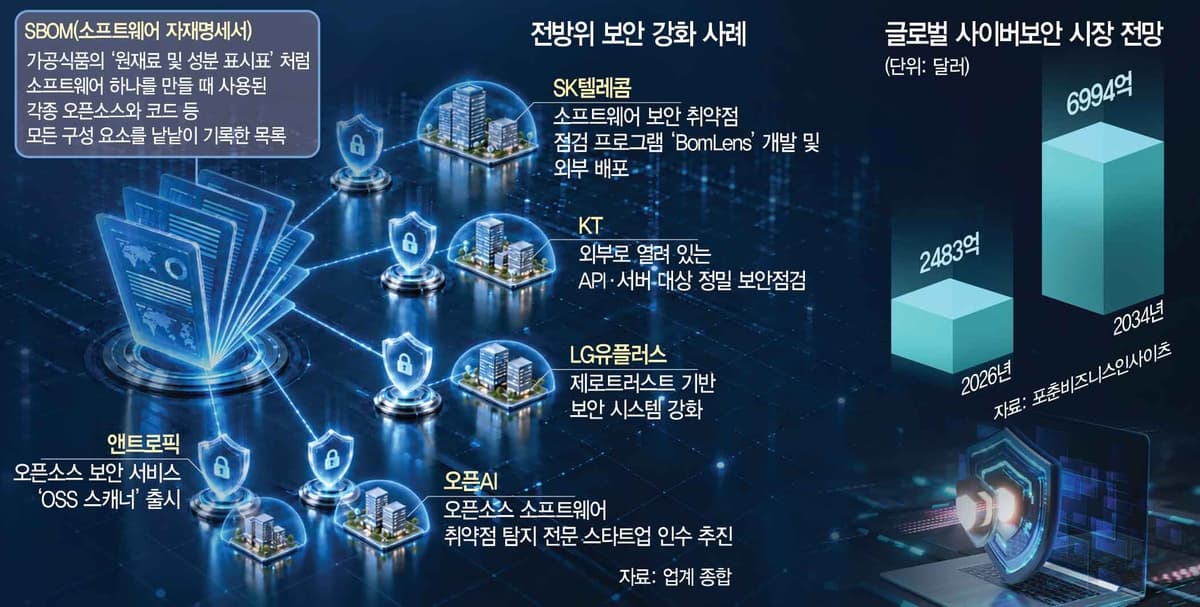
SK Telecom (017670) has developed BomLens, a dedicated tool that lets software vendors check and manage security vulnerabilities on their own, and is distributing it through GitHub, telecom industry officials said on Oct. 14. The tool helps suppliers identify open-source programs embedded in their software and monitor them continuously for vulnerabilities.
"Since this year, we have been requiring outside suppliers to submit a software bill of materials so we can see what components are included in the software they provide," SK Telecom said. "BomLens makes it easier and more accurate for suppliers to produce one." A software bill of materials, or SBOM, is an inventory describing all components that make up a piece of software and the dependencies among them.
Other companies are also stepping up their overall security systems. KT conducted security audits of externally exposed application programming interfaces and servers. LG Uplus is accelerating work on a zero-trust security framework, including minimizing the attack surface available to outsiders. "Telecom carriers have been expanding security investment after a series of breaches last year, but the hacking at financial firms has built a consensus that defending their own networks alone is not enough," a telecom industry official said. "There is an urgent need for an integrated security system spanning devices, applications and the cloud."
Stronger security capabilities are also becoming more important for winning business in the public-sector AI transformation market. Most AI projects run by the government and state-run institutions are carried out by consortiums that bring together telecom carriers, AI model developers, cloud providers and solution companies. Because a security breach at any single participant can affect the credibility of the entire service and the operation of the project, the telecom carriers leading these consortiums must raise the overall security level of their partners. "The more sophisticated AI-driven attacks become, the more limited any individual company's defenses are, so security management that covers partners and supply chains will grow in importance," an IT industry official said.
Companies abroad are also focusing on routes where external vulnerabilities can arise and preparing to close them. OpenAI, the developer of ChatGPT, is reported to be in talks to acquire Trail of Bits, a cybersecurity firm that finds and fixes vulnerabilities in open-source software. Anthropic, the developer of Claude, recently released OSS Scanner, a free AI inspection tool with similar functions. It uses the company's high-performance models to regularly scan open-source projects and provide the vulnerabilities it finds along with suggested fixes. ARTEX, reportedly used in the hacking of South Korean financial firms, is also known to be an open-source cybersecurity tool developed in China. "Open-source tools have the advantage of advancing quickly because developers around the world take part, but the flip side is that hackers can abuse them to gain an easy route of attack," a security industry official said.