
If you’re of a certain age, “PHP” may invoke memories of early web development in the 1990s. In the decades since, the scripting language has hummed along in the background, used by popular platforms like WordPress. But just this week, it suddenly got an enormous spotlight as the internet lit up with alarm over two high-risk vulnerabilities.
If you’re not a server administrator, you may be wondering what the danger really is. In fact, if the admins for the websites you use or run were quick enough, you may have not noticed a thing.
So what is PHP? And does it affect you? Here’s what you need to know.
What is PHP?
PHP is known as a general-purpose scripting language often used in web development. Run on a server, it allows websites to handle complex actions without having to embed instructions or content within pages. Examples of dynamically generated output include showing the current calendar date, HTML and PDFs, and even JSON and XML files for caching purposes.
Many websites use server-side languages to serve content, and of those that do, some sources (like W3Techs) estimate that almost 70 percent rely on PHP. Across the broader internet, W3Techs believes around 40 percent of all websites (yep, all!) run on WordPress—a major adopter of PHP.
Why did PHP blow up in the news?
On October 20, 2026, the PHP Group (which maintains PHP) released an alert for coming security updates, designed to patch two very high-risk vulnerabilities later named as CVE-2026-109618 and CVE-2026-109619. Both enable an attacker to run remote code, carry a severity rating of 9.2 of 10, and affect “all PHP installations serving web requests,” according to the PHP Group.
The advisory set off a flurry across the web, with server administrators hurriedly preparing for the patched versions of PHP. When details of the two vulnerabilities released the next day on October 21, sites across the web began going offline temporarily as PHP upgrades were completed—including government websites in the Netherlands, France, and Germany.
Why is this a big deal?
Two main reasons: The number of affected sites, and how fast vulnerabilities can now be exploited.
Hypothetically, if left unpatched, over half the internet was at risk for hacking. Simultaneously, in the current AI-era, exploits can be deployed rapidly—sometimes in mere minutes.
In the pre-AI era, vulnerabilities could take days, weeks, or even months before an exploit was seen, and the proliferation of such attacks also spread more slowly. Their discovery also took longer. And AI didn’t just accelerate the threat—it helped researchers uncover these vulnerabilities in the first place.
That last point is especially notable. Researchers at Wiz used frontier AI models including Google’s Gemini 4 Argon and OpenAI’s GPT-5.6 Sol while uncovering the flaws and developing working exploits. According to Wiz, AI helped turn vulnerabilities that had lurked in PHP for more than a decade into something a single researcher could exploit in a week—a task the company estimates could previously have taken a world-class security team months. That’s the double-edged sword here: AI can help defenders uncover dangerous bugs before attackers do, but it’s also rapidly lowering the time and expertise needed to turn obscure flaws into working attacks.
Which PHP updates include the security patches?
The PHP Group has only directly issued patches within versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35. If a website relies on an older version, they must receive the necessary security fixes through a vendor who helps maintain that older version.
How will I be affected?
Some websites may go or remain offline until on a secure version of PHP. But as of afternoon in the U.S., many are operating normally. You should be able to visit sites as usual.
If you manage a website using PHP, verify it’s updated to one of the patched PHP versions. You may actually have to do nothing—some consumer web hosts are quietly handling this work in the background. (When I helped check a volunteer group’s settings, not only had the WordPress site been upgraded to 8.3.36, but a message from the support team said it was globally applying updates, and had also configured its firewall to block exploit attempts.)
For those of a nerdier bent—say, running PHP as part of a NAS, Raspberry Pi, or other setup—you should put on your server admin hat and ensure a proper update.
Do I need to protect myself against unpatched websites?
In a general sense, yes. Even with a server’s (or other service’s) firewall defenses in place, a website using an unpatched version of PHP could be attacked and used to run remote code, meaning it could:
- Spread malware
- Steal data from the server
- Delete data on the server
When browsing the internet, your best defense is the same standard advice. Keep your browser and antivirus software up-to-date, and also, only share necessary info about you with websites.
If you’re storing data on a site, ensure you have backups of that data—just in case.
How do I know if my WordPress site is safe?
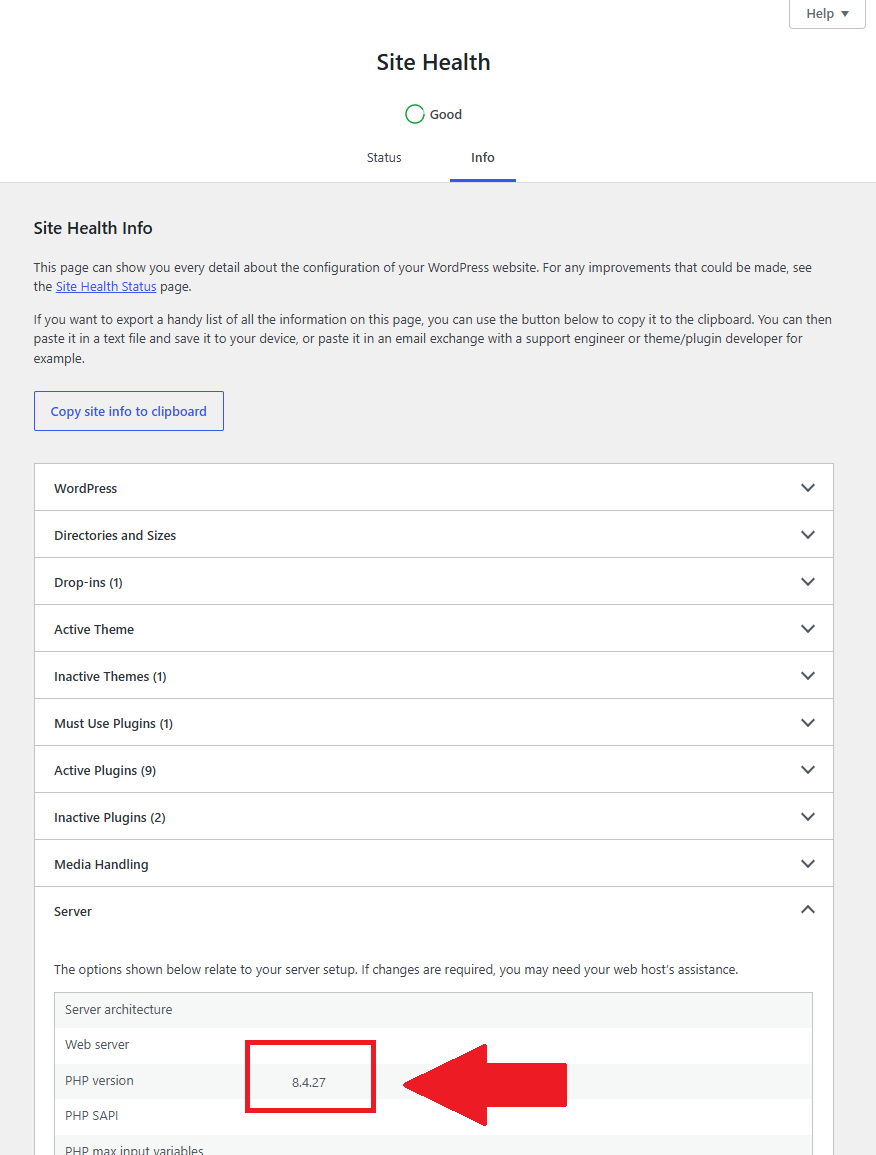
Your webhost may show the full details of your PHP version in the general management dashboard. If not, check within WordPress’s admin dashboard.
In the left-hand navigation bar, look for Tools, then choose Site Health. You’ll see two tabs in the main part of the screen. Select Info, then choose the Server section. A drop-down screen should reveal your PHP version.
PCWorld