Copyright protected content copied from PhoneWorld website.
Pakistan’s National Computer Emergency Response Team (National CERT) has issued a cybersecurity advisory warning public and private organizations about growing security risks associated with third-party vendors, suppliers, and external service providers.
According to the advisory, businesses and government institutions could face serious cyber threats if their external partners fail to maintain adequate security measures. Even organizations with strong internal cybersecurity systems may remain vulnerable if attackers exploit weaknesses in a trusted vendor’s network or software.
National CERT warned that third-party service providers often have access to an organization’s systems, sensitive information, and security credentials. If these access points are not properly secured, cybercriminals could use them to infiltrate internal networks, steal confidential data, or compromise digital operations.
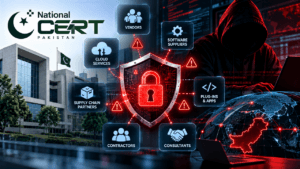
The advisory identifies potential sources of risk including cloud service providers, software vendors, third-party applications, plugins, contractors, consultants, manufacturers, distributors, and supply chain partners.
These external relationships have become increasingly important as organizations rely on cloud platforms, outsourced IT services, and integrated software solutions. However, vulnerabilities in any connected system could create security risks for an entire organization.
How Third-Party Vendors Can Become a Cybersecurity Threat
National CERT highlighted that attackers may target smaller vendors or business partners with weaker cybersecurity controls rather than attempting to breach a heavily protected organization directly.
Once a third-party provider is compromised, attackers could potentially exploit existing access privileges to reach the systems or information of the organization it serves.
The advisory also raised concerns about sensitive information being shared with external companies without adequate safeguards. Such practices could expose confidential business records, personal information, or security credentials to unauthorized individuals.
Software applications, plugins, and cloud-based tools were identified as additional areas of concern, particularly when vulnerabilities remain unaddressed or access permissions are not properly managed.
According to National CERT, an organization’s cybersecurity depends not only on its internal security infrastructure but also on the protection measures adopted by vendors and business partners.
National CERT Recommends Five Security Measures
To reduce the risk of third-party cyberattacks, National CERT advised public and private organizations to strengthen their vendor security practices:
- Enforce security requirements: Ensure third-party service providers follow appropriate cybersecurity requirements and controls.
- Assess vendors before engagement: Evaluate vendors’ cybersecurity measures before granting access to systems or sensitive information.
- Limit third-party access: Give external providers only the permissions needed for their assigned work.
- Monitor vendor activities: Regularly review third-party activities and access to detect suspicious behaviour or security violations.
- Review incident response procedures: Regularly review cyber incident reporting and response plans to ensure timely communication and coordinated action following a breach.
National CERT emphasized that weaknesses in a single external service provider could undermine the cybersecurity defences of an otherwise well-protected organization.
The advisory highlights the need for Pakistani businesses and government departments to assess external technology partners, control access to sensitive systems, and maintain oversight of third-party cybersecurity practices.
Also read:
Pakistan’s 5G Rollout Faces Fresh Uncertainty After Right of Way Bill Withdrawal
The post National CERT Warns Pakistani Organizations of Cyberattacks Through Third-Party Vendors appeared first on PhoneWorld.