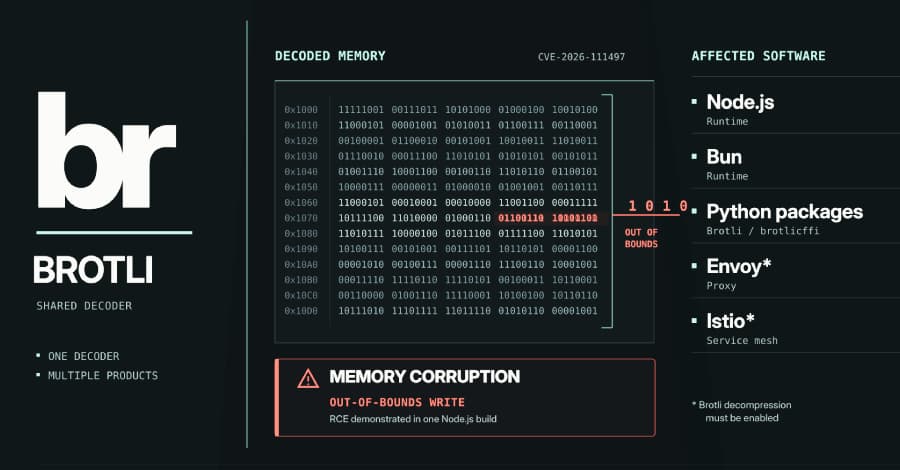

A memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli.
Tracked as CVE-2026-111497, the flaw allows crafted compressed data to overwrite past the end of a buffer and corrupt a program's memory, potentially causing a crash, a memory leak, or the execution of attacker-controlled code.
Imperva researchers have shown that code can run on one unpatched Node.js build. The same has not been demonstrated on the other software, and no real-world attacks have been reported.
The flaw was first disclosed on October 21, when Node.js and Google shipped fixes, and more have followed product by product since. Because the bug is in Google's decoder and each program ships its own copy of it, every one has to update that copy on its own.

Brotli is a compression format from Google, used across the web to shrink pages and other traffic. The bug is in the C code that unpacks a Brotli stream, so it travels into anything that reuses that code, from language runtimes to proxies to Python packages.
Which Software Is Affected
| Product | Affected | Fixed in | Exposed when |
|---|---|---|---|
| Google Brotli (C library) | 1.0.3 to 1.2.0 | 1.0.10, 1.1.1, 1.2.1 | code decodes untrusted Brotli |
| Node.js | 22.x, 24.x, 26.x before the fix; 20.x and older (end of life) | 22.23.4, 24.22.1, 26.12.1 |
fetch() of a br response, or Express or body-parser br bodies
|
| Bun | 1.4.3 and earlier | 1.4.4 |
fetch() of a br response, or node:zlib
|
| Envoy | 1.39.2, 1.38.5, 1.37.7, 1.36.11 | 1.40.0, 1.39.3, 1.38.6, 1.37.8, 1.36.12 | only if the Brotli decompressor is configured |
| Istio | 1.31.0 to 1.31.1, 1.30.0 to 1.30.5, 1.29.0 to 1.29.8 | 1.31.2, 1.30.6, 1.29.9 | only if Brotli decompression is enabled |
Python Brotli
|
1.2.0 and earlier | 1.2.1 |
installed, and an HTTP client decodes br
|
Python brotlicffi
|
1.2.0.x and earlier | 1.2.1.0 |
installed, and an HTTP client decodes br
|
| cdxgen | standalone binaries and images, 13.4.0 and 12.8.8 and earlier | 13.5.0, 12.8.9 | standalone binary or image scanning untrusted input |
A program is exposed only if it decodes Brotli data that someone else controls. For Node.js and Bun, that happens when the built-in fetch() reads a response sent with Content-Encoding: br, or when request-body code such as Express 5 and body-parser 2 unpacks a Brotli upload. A plain Node.js HTTP server does not decode request bodies on its own.
Envoy and Istio are affected only when Brotli decompression is enabled, for example, through an Envoy filter. Where it is off, the flaw cannot be reached.
In Python, the risk comes from the Brotli or brotlicffi package being installed at all. Once either is present, HTTP clients such as requests, urllib3, httpx, and aiohttp decode Brotli responses on their own, so an application can be exposed without ever importing Brotli in its own code.
A web application firewall helps only so far. Vercel, which added firewall rules on the day of disclosure, said those rules do not cover "responses your functions fetch from other servers." For that path, only updating the runtime or library closes the hole.
How far the flaw can be pushed depends on the software. Imperva's Red Team, which calls its work Node2Shell, ran attacker-supplied code on an unmodified Node.js 24.22.0 build for Linux on ARM64, delivering it both as a fetched response and as an Express request body. The exploit took several tries, has not been released, and was not tested on other builds.
OpenAI, whose Codex Security team reported the flaw, describes it as enabling unauthenticated remote code execution in Brotli and lists Node.js, Bun, and Envoy as affected software. In its account, the flaw works both ways:
an unpatched server that accepts compressed input could be taken over by a malicious client, and an unpatched client that accepts compressed input (such as "curl --compressed") could be taken over by a malicious server.
No in-the-wild exploitation has been reported. CISA's October 23 assessment recorded exploitation as "none" and automation as "no," and Red Hat said there is no reliable public proof-of-concept for running code.
Severity ratings differ by who is scoring. Google, which assigned the CVE, rates it 9.2, or critical, on the CVSS 4.0 scale. Node.js calls it high, and Red Hat rates it 8.1, or important.
The fix has an unusual history. The change that closes the flaw was added to Brotli's source code on February 27, but no new Brotli release carried it until October 21. OpenAI said the root cause "was actually fixed in the Brotli source code in February, but it wasn't known at the time that it gave rise to a security vulnerability and there was no more recent release of Brotli."

Node.js credits Khai Tran and Sylvie Mayer of OpenAI's Codex Security for reporting the flaw, and maintainers Matteo Collina and Antoine du Hamel for the fix.
What to Do Now
Update to a fixed version from the table above, then restart the service and rebuild any container image, because a running process keeps the old decoder until it restarts.
Where you cannot update yet, stop decoding untrusted Brotli. OpenAI's disclosure page and the security firm Aikido both recommend:
- Reject incoming requests with Content-Encoding: br before any proxy or parser decodes the body.
- Turn off automatic Brotli decoding in HTTP clients, and reject Brotli responses before they are decoded.
- In Python, uninstall the Brotli and brotlicffi packages so clients fall back to gzip and deflate.
Dropping br from the Accept-Encoding header does not help on its own, because a server can send Brotli whatever the client asks for. For Node.js, no workaround has been published, so updating the runtime is the only fix.
System packages are being fixed at different times. Debian fixed its brotli package for Debian 13 (trixie) on October 23 in version 1.1.0-2+deb13u1. Amazon Linux 2023 still listed its brotli and Node.js 24 packages as pending a fix as of October 22.
Dependency scanners may not flag the Python packages yet. The CVE record names Google's Brotli repository, not the PyPI packages, and GitHub's advisory still lists no affected package, which is what Dependabot reads. Advisory entries for the two Python packages, PYSEC-2026-4322 and PYSEC-2026-4323, were added on October 23, so check the installed versions manually as well.
Found this article interesting? Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.