If you thought that AI agents going rogue – they didn’t, if you really think about it – and their ability to jump from device to device while figuring out unfamiliar ones on their own was bad news, it gets worse: they’re simply the harbinger of what’s to come. A recent report pointed out that there are hackers who have perhaps taken inspiration from the episode, and have just decided to prompt their way into over 100 companies, with the total number of attempts going over 1,200. Making matters worse, these attempts were facilitated by a tool called Cairn.
Researchers at Norforge highlighted three clusters of AI threat activity, with each cluster likely representing one individual or group of threat actors. This includes one that prompts in Chinese, which some reports highlight as noteworthy for its prompts containing less than 100 Chinese characters. That said, due to the way the language works, this is about equivalent to using under 100 English words, so your mileage may vary as to whether that’s impressive or not.
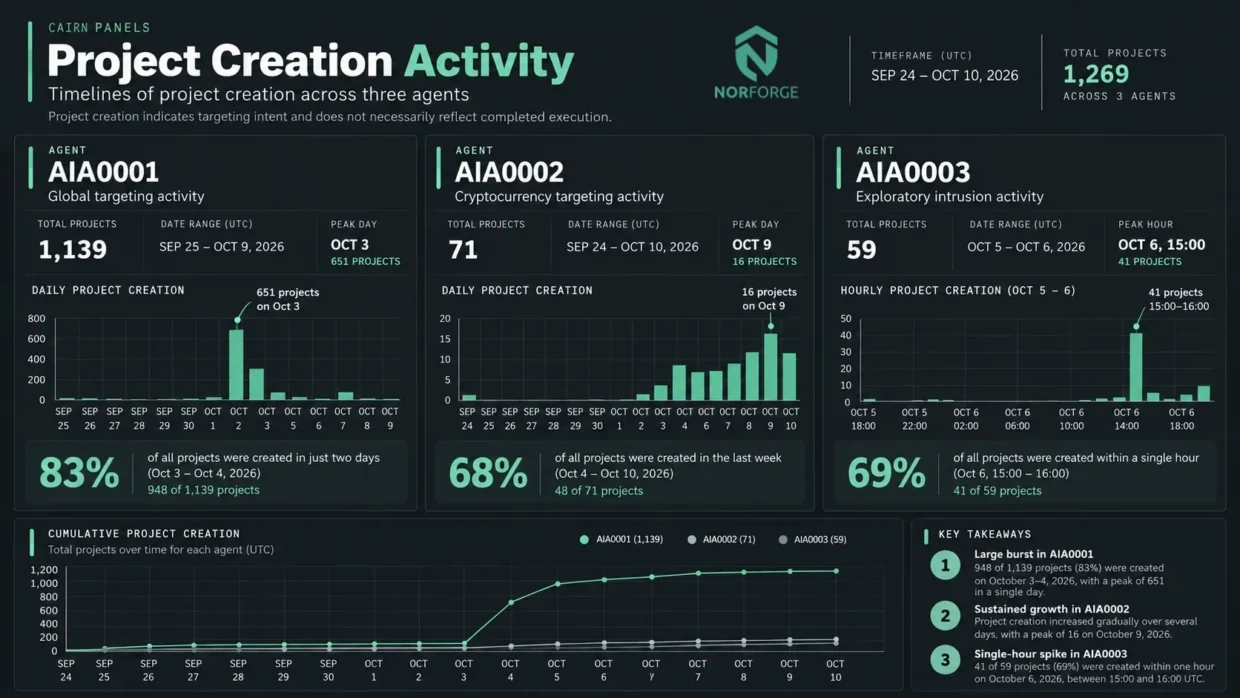
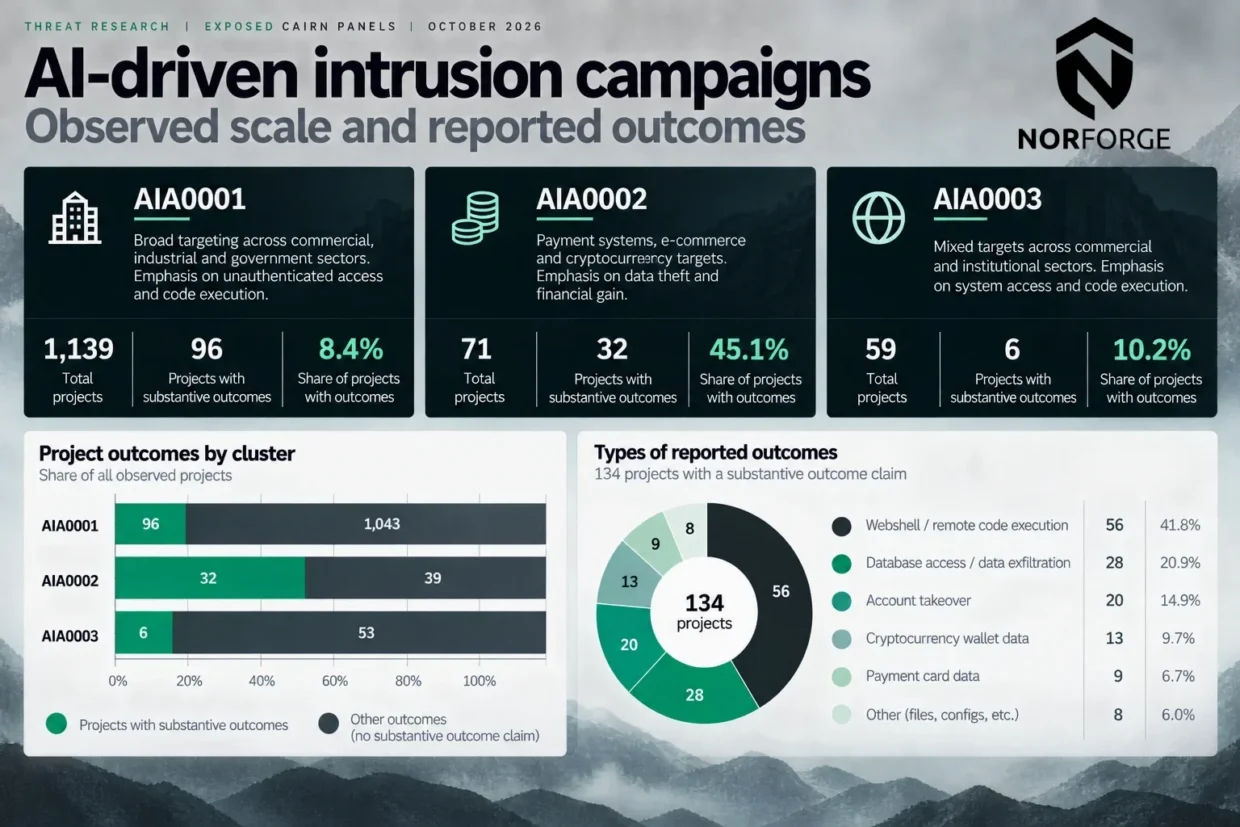
At any rate, these three clusters of AI threat activity let their AI agents do their thing once the prompt is done. While there is one notable “project” that ran for over five days, the average attack ran for less than 23 hours, with an average success rate of about 10%. The aforementioned Chinese cluster was by far the most active, constituting 1,139 of the 1,269 attack projects tracked. Victims of these hacks include farming equipment maker John Deere, home appliance company SharkNinja, and engine manufacturer Cummins, according to Reuters.
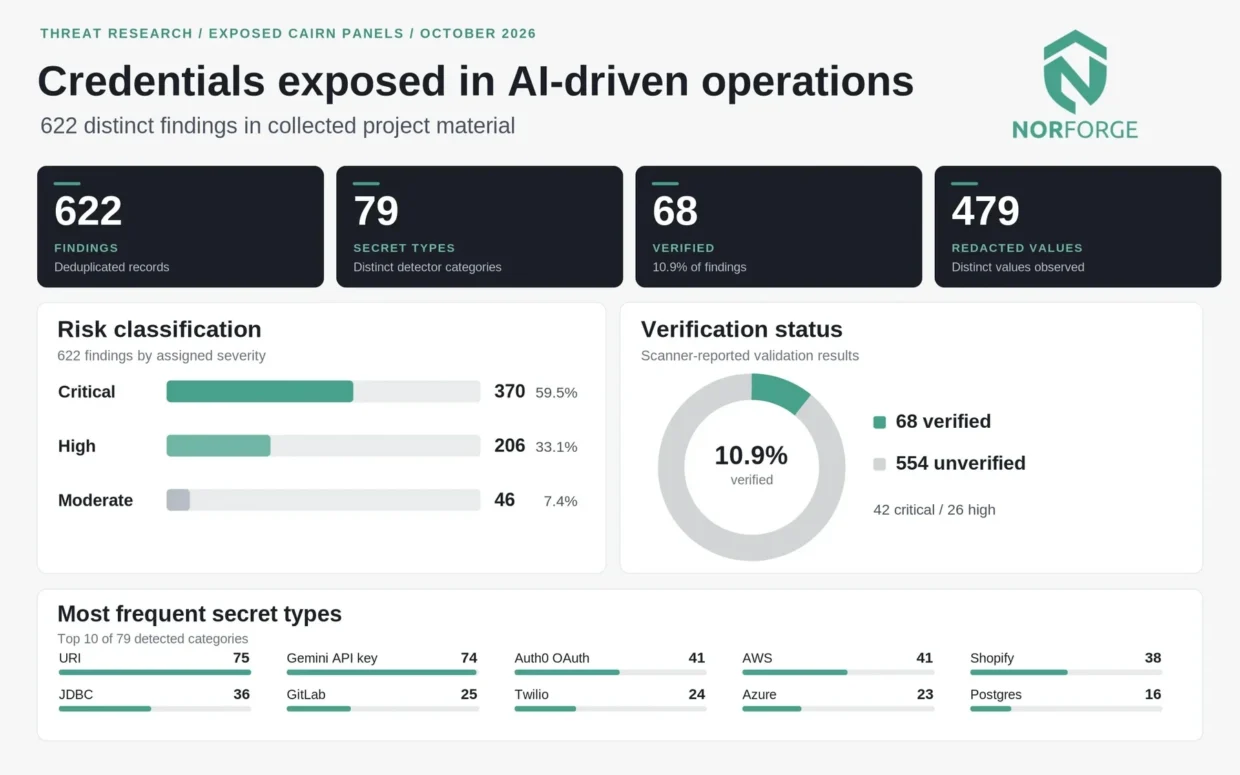
Norforge adds that, in the attackers’ rush to gain quick results, they have compromised their own operational security, inadvertently exposing their targets to a far larger attack surface than they probably intended. This is because all of the attack projects were listed on Cairn panels while being completely unprotected. This, in turn, means that “controls for starting and stopping projects, interfering with ongoing operations, inserting new data, redirecting agents to different targets, and restarting old projects” are all visible. Though it is worth mentioning that the researchers did not rest to see of they actually work without authorisation.
Norforge says that it is attempting to get the offending Cairn panels taken down. The creator of Cairn, who goes by @le1xia0, said on X that the platform was never a hacking tool, and if someone uses it for that, it’s “entirely up to the user”.
(Source: Norforge, Reuters, @le1xia0 / X)
The post Hackers Use AI Agents To Make Over 1,200 Break-In Attempts On Over 100 Companies appeared first on Lowyat.NET.