Police referred a series of artificial intelligence-driven hacking attacks on South Korean financial institutions to the Major Crimes Investigation Agency, but the agency declined to open an investigation, saying police had already carried out much of the work. The decision has intensified debate over how investigative duties are divided, since police had classified the case as a major crime only after obtaining a formal interpretation from financial regulators. Within the police, officials question whether the agency, which has yet to build out its own investigative system, is taking only cases it can handle immediately.
The Seoul Metropolitan Major Crimes Investigation Agency notified police on Oct. 23 that it would not open an investigation into the financial-sector hacking case, according to police and legal sources on Oct. 25. The decision came three days after the agency received the referral. The agency said it took into account that police had already secured and analyzed access logs and requested international cooperation from the U.S. Federal Bureau of Investigation, among other steps.
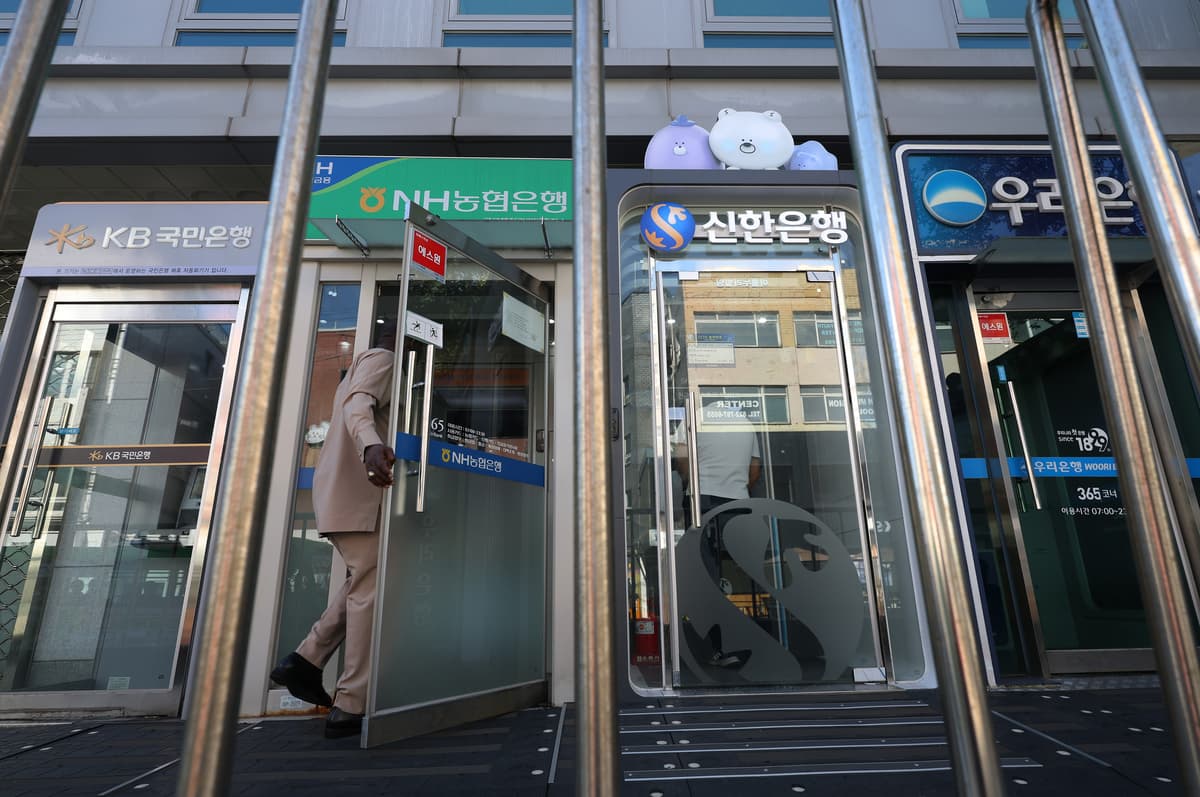
Police launched a formal investigation on Oct. 5 on suspicion of violating the Information and Communications Network Act, after a run of AI-driven hacking attacks on commercial banks and other financial firms. A dedicated team of 28 officers across four cyberterror investigation units was assembled under the head of the National Police Agency's cyberterror response division, a senior superintendent. As of Oct. 14, 16 financial companies had been identified as victims, including KB Kookmin Bank, Shinhan Bank, Hana Bank, BNK Busan Bank, Yegaram Savings Bank, Welcome Savings Bank and Hyundai Capital.
Given the gravity of the case, police pursued the investigation while also weighing whether it met the criteria for referral to the agency. In cyber cases, a referral may be warranted if the victim institution qualifies as national critical infrastructure, such as the Korea Financial Telecommunications and Clearings Institute or the Korea Exchange, or if the breached system qualifies as electronic financial infrastructure. Because the affected financial companies do not fall under national critical infrastructure, police asked the Financial Services Commission for a formal interpretation of whether the breached systems constitute electronic financial infrastructure.
Around Oct. 20, the commission replied to the National Office of Investigation that the systems could qualify as electronic financial infrastructure under the Electronic Financial Transactions Act. Police then added a charge of violating that act and referred the case to the agency.
The agency, however, decided against opening an investigation within three days, well short of the seven-day statutory deadline for the determination. It concluded that leaving the case with the existing investigative body would be more efficient, given how far police had progressed and the international cooperation already under way. The case will therefore remain with police.

In a statement, police said they had "continued the investigation without any gap even after referring the case to the agency," adding that they would "pursue the suspects through a thorough investigation, with the same sense of responsibility as before." Internally, the mood is different. There is considerable frustration that the agency declined, on grounds of efficiency, a case that police had judged might constitute a major crime after obtaining a regulatory interpretation. Officers note in particular that investigative work has been concentrated on police since the agency's launch, and that police must now handle a large-scale financial hacking case on their own as well.
Some attribute the agency's decision to its limited investigative capacity. The post of head of the cybercrime investigation division at the Seoul agency is currently vacant. Forensic equipment needed for digital searches and seizures has yet to be transferred, as the Public Indictment Service (gongsocheong), the newly created indictment-only body, is still using it to wrap up existing cases. The Korea Information System of Criminal Justice Services, known as KICS, is also not fully operational, leaving some tasks to be handled by hand. As a result, the agency lacks both the staff and the equipment to take on hacking cases that require advanced expertise and international cooperation. Legal observers have also questioned whether the agency is avoiding cases with a heavy investigative burden and selecting those that can yield results quickly.
A senior police official in Seoul said: "In the end, isn't it that the agency found the consequences it would have to answer for too burdensome, and so decided not to open an investigation? We know the agency's investigative system is not properly in place, but the problem starts with an investigative body launching before it had even finished basic preparations."
Compounding the issue, no institutional mechanism yet exists to mediate such disputes between investigative bodies. Since the debate over abolishing the prosecution service and restructuring investigative agencies began, officials have pointed to the need for a body to resolve jurisdictional conflicts among police, the agency and others. But the investigative authority coordination council created under the revised Criminal Procedure Act will not take effect until February. For now, police, the agency and the Corruption Investigation Office for High-ranking Officials coordinate case matters through hotlines, without a separate consultative body.
A police official with experience in cybercrime investigations said: "This case exposes the agency's lack of investigative capacity — a cyberterror case of national importance was classified as a major crime after a formal interpretation from financial regulators, and the agency still declined it simply because police had investigated it first. With no body to adjust jurisdiction among investigative agencies, the agency could repeatedly push burdensome cases onto police."
