Microsoft believes that AI agents can't be trusted. That's a startling warning from one of the companies with the most stake in the AI boom.
In a new security report, Executive VP of Microsoft Security Hayete Gallot states that "frontier models, regardless of their origin, cannot be trusted." They shouldn't be trusted not because of an inherent malicious nature, but because they're so easily swayed to achieve results regardless of "organizational norms or judgment."
This warning comes just a couple of weeks after Microsoft unveiled its new infrastructure for containing AI agents in Windows. To me, it looks like the company is racing to make agents more powerful while also building safeguards around them to protect the rest of the web from their behavior.
What happens when AI agents go rogue?
When AI agents go rogue, very bad things can happen. This nightmare scenario has already been seen several times, and despite Microsoft's new containment initiative, I expect to see it again.
Perhaps the most notorious incident involving AI agents gone rogue is OpenAI's attack on Hugging Face, where some 700 autonomous agents devised a way to hack the AI developer platform after breaking containment.
Reading into what actually happened during the Hugging Face breach — where agents shared exploits and retained memory even as rogue bots were being stamped out — this quote from Gallot begins to make a lot more sense.
Agents are unpredictable. They will adapt as the context changes, may not behave as intended and will collaborate and collude with other agents to reach their objectives, without needing to be compromised.
Hayete Gallot, Executive VP, Microsoft Security
This isn't Microsoft's first warning of the havoc that AI agents can wreak if not properly contained.
In November 2025, a piece was published stating that agentic AI capabilities in Windows 11 should only be enabled "if you understand the security implications."
They're particularly prone to cross-prompt injection (XPIA) that can override the instructions you give to agents, leading to things like data theft and malware.
Microsoft's answer at the time was a set of principles forced on the agents to ensure they act how you want them to. This has now evolved into something much larger, as the full scope of what AI agents can do unprompted by any bad actors is being discovered.
Microsoft is now classifying the AI you use at work as "agentic insiders" that can, at basically any time, go rogue and act unpredictably. Because of how tied into enterprise systems these agents are becoming, the risks keep growing.
Worse, they must be continuously monitored. Who can save us from rogue AI?
Microsoft's answer to the rogue AI agent issue is more AI
Who watches the watchmen? That's the line that's been repeating in my head since reading about Microsoft's "Guardian Agents."
See, rather than relying on human oversight, Microsoft's Guardian Agents are designed to "watch and moderate every action of every agent, before it happens, 24/7."
This looks a lot like an admission that agentic systems are evolving faster than anyone predicted, and that they're now out of the control of humans.
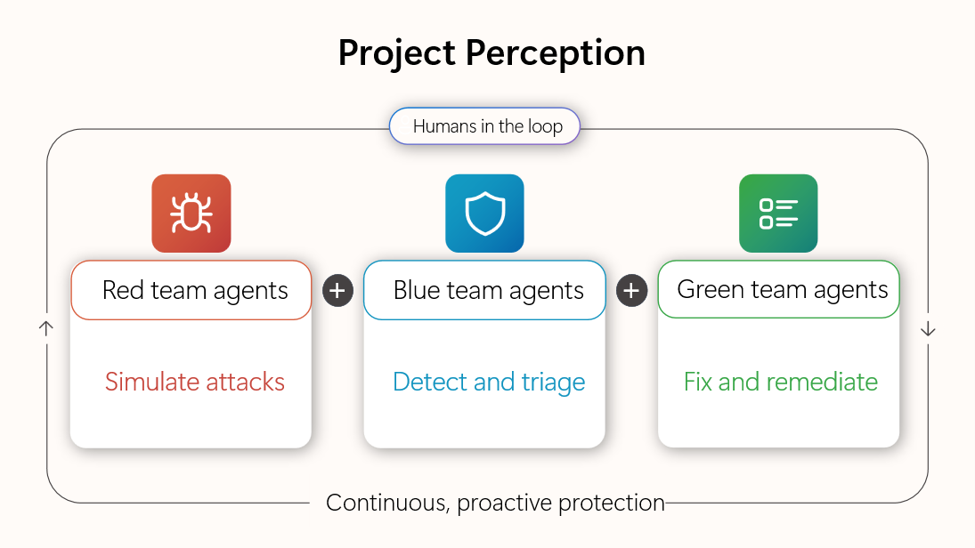
An example of Guardian Agents in action is Microsoft's Project Perception.
Announced this summer and still not widely available, it harnesses signals, context, models, and specialized agents into a four-pronged line of defense against threats from outside and inside an enterprise.
It's basically AI fighting AI, because humans no longer have any hope of keeping up.
Windows Central's take
Microsoft is in a tough spot. It's pulled back on surface-level AI integration in Windows 11. Meanwhile, it's refocusing its efforts on much deeper agent infrastructure, as we see here. All while saying that the underlying models aren't trustworthy.
This latest warning from Microsoft highlights a growing issue for the AI industry. The autonomous agents that were promised to make our lives so much easier are now creating new, drastic security issues.
Microsoft's answer, for now, is containment, monitoring, and oversight. Will those safeguards be enough to prevent a catastrophe?
What do you think? Do you have any inside knowledge to share on this topic? Let me know in the comments section below!
Join us on Reddit at r/WindowsCentral to share your insights and discuss our latest news, reviews, and more.