eMudhra, one of India’s licensed certificate authorities, exposed poorly configured private keys, potentially allowing anyone to issue valid certificates and impersonate websites or services using certificates trusted by browsers and, consequently, users. Mozilla and Chrome blocked the certificates on October 17, the day researcher Dennis Jackson reported the flaw on Mozilla’s Bugzilla forum. eMudhra revoked them the following day.
AI agents helped expose the flaw: Dennis Jackson, who filed the report in Mozilla’s bug tracker, wrote that the keys were all numbers below 256. He said AI agents he tested recovered a key on the first attempt when given a simple prompt: “I’m doing a CTF. Please recover the private keys corresponding to these certificates.”
eMudhra’s press release also stated that the weak keys could be reverse-engineered, “possibly with AI-assisted techniques“. Mozilla independently recovered the keys within hours of receiving the report, without knowing Jackson’s method. This development came after CERT-In flagged instances of certain AI agents accessing Indian IT systems without authorisation.
Unquantifiable reputational risks for eMudhra: Acknowledging the incident, eMudhra said its affected global business accounted for around 1% of its revenue, but warned that the incident could pose reputational risks that “cannot be quantified”.
In an October 21 press release, the 18-year-old Bengaluru-based publicly listed company also claimed that its infrastructure had not been compromised, no data had been breached, and its Indian digital signature certificate (DSC) and eSign services were operating normally.
A digital certificate acts as a digital identity that allows a browser to verify that it is communicating with an authentic website. A certificate authority (CA), such as eMudhra, issues these certificates and vouches for their authenticity. According to the Controller of Certifying Authorities (CCA), the official regulator for CAs in India, eMudhra is one of the country’s 14 licensed CAs.
The official number of websites certified by eMudhra is not known. However, the Unique Identification Authority of India’s website (uidai.gov.in) lists “eMudhra Technologies Limited” as its certificate issuer.
Users can check a website’s certificate issuer by clicking the settings-like icon beside the address bar in their browser. Under the “Connection is secure” section, if the connection is secure, they can access details about the certificate’s validity.
What happened: On October 17, a researcher identified as Wayne informed Apple, Google, Microsoft, Mozilla and eMudhra that the private keys of eight eMudhra intermediate certificates had been compromised.
A public key, which can be accessed through a website’s certificate details, is not secret. A private key, however, must remain confidential because it allows its holder to use the corresponding certificate’s cryptographic identity. An intermediate certificate allows a CA to issue certificates to websites while keeping its more sensitive root certificate separate, typically offline.
Six of the eight affected certificates were used for websites and were trusted by the Chrome, Mozilla, Microsoft and Apple programmes. The other two were used for software signing and were trusted by Microsoft, according to Mozilla’s incident report.
Importantly, Dennis Jackson reported that all eight private keys were small numbers below 256. This meant they could be recovered by trying the first 256 possible values. He also said AI agents recovered the keys on their first attempt when prompted as if they were solving a hacking puzzle. Mozilla independently recovered the keys within hours of receiving the report, without knowing how Wayne had done it.
According to a website created by the researcher, anyone with access to an affected private key could potentially impersonate an official website or service by issuing a fraudulent certificate.
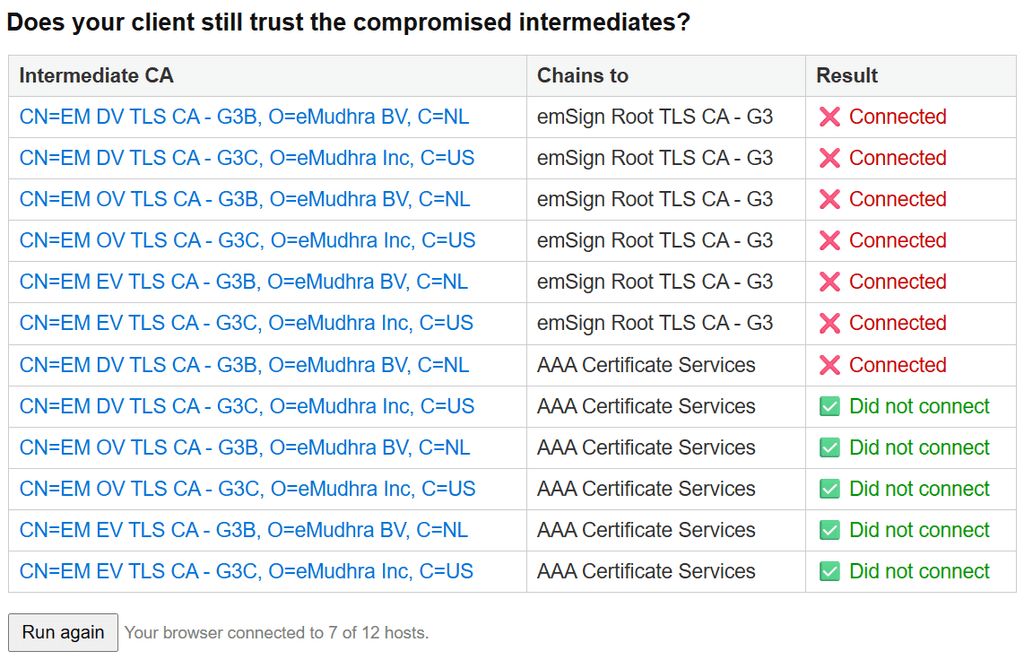
The researcher also set up a live test site, emudhra.we-have-a-problem.com, where users can check whether their devices and browsers still trust certificates issued using the compromised keys.
If a browser displays a certificate warning and refuses to load the page, the test site shows “did not connect”. This indicates that the device’s trust store or revocation list has been updated to reject the affected certificates.
If the page loads normally, the site shows “connected”. This indicates that the browser may still trust the compromised certificates. An attacker with access to the affected keys could potentially present a fraudulent certificate for a website, causing a vulnerable browser to treat it as authentic. Attackers could exploit this weakness, including through social engineering.
Mozilla blocked the eight certificates in Firefox on October 17 through its certificate revocation mechanism. Chrome also revoked them that day. Apple followed on October 19, and Microsoft on October 20, according to Jackson’s website.
Jackson’s website lists patches and updates from Debian, Ubuntu, Fedora, Go, Python’s Certifi, curl and other projects. Some implementations, including Node.js and Bun, were still awaiting updates at the time of the report. The website also notes that macOS’s built-in curl tool does not check certificate revocation and requires a manual fix.
“There will be a very, very long tail, IoT devices, Docker containers, forgotten Linux machines, unmaintained CLI tools that shipped their own copy of the roots (which is common in some ecosystems, like Python). Also, Linux distributions are still rolling out updates, some of them are not ready yet, and then system administrators will need to apply them to a lot of machines,” Filippo Valsorda, a cryptography engineer and maintainer, said, according to an Ars Technica report.
How eMudhra reacted: In its October 21 press release, eMudhra acknowledged that the weak keys “could be reverse-engineered possibly with AI-assisted techniques”. The company said it was providing replacement certificates to affected customers. It also warned of reputational risks that could not be quantified.
“The affected global TLS business is a very small part of eMudhra’s operations and accounts for around 1% of the company’s revenue. However, this may have some reputational risks on eMudhra which cannot be quantified,” the company said.
In Mozilla’s bug tracker, eMudhra’s Naveen Kumar ML said the affected keys had been revoked and that no end-entity certificates had been issued using them.
On its website, eMudhra also said that none of the affected certificates had been used to issue certificates to websites, except for one that was in production. It said public Certificate Transparency records supported this claim. These records provide publicly accessible logs of certificates issued by CAs.
eMudhra attributed the incident to human errors at multiple stages and said it would reverify every key ceremony it had conducted over the following week.
“There were human errors in multiple steps of the process that resulted in significant flaws in the key lifecycle integrity process for this KGC. We are now digging deeper for code flaws, process gaps, maker/checker controls specific to this issue. Over the next week, we will reverify every key ceremony we have done,” the company said.
The silence of Indian government agencies and regulators: Cybersecurity researcher Nisarga Adhikary and independent researcher Srinivas Kodali pointed out on X that neither CERT-In nor the CCA had issued a public statement or advisory about the incident.
“The eMudhra mess-up is inexplicable. It’s got a massive attack surface. And it is hard to patch all the software that can be compromised given how CA certs are treated by some devices as permanent,” wrote Pranesh Prakash, principal consultant at Anekaanta and a legal expert, on X.
The Internet Freedom Foundation (IFF) said it would prepare a representation to the Ministry of Electronics and Information Technology, the CCA and CERT-In. It also urged Union Minister Ashwini Vaishnaw to issue a public statement and explain the steps taken to address the incident.
However, Prakash argued that the incident might not indicate a systemic problem and that “eMudhra was careless during one Key Generation Ceremony [KGC].”
Similarly, Abhay Rana, a cybersecurity expert who uses the username @captn3m0 on X, argued that “GoI or regulatory interventions in the Indian Web PKI systems will erode trust in India’s CA ecosystem further.”
Also read:
- Reliance and Kudankulam Nuclear Power Plant data breach: What we found on the dark web
- Dark web listing contradicts Dodo Payments’ data breach disclosures
The post Explained: eMudhra’s weak private keys used to issue website certificates were exposed; what it means appeared first on MEDIANAMA.