Businesses deploying artificial intelligence must consider what happens to sensitive information while a system is using it, not only where the information is stored. Confidential computing is designed to protect data during processing, adding another layer of security to the controls used to protect information at rest and in transit.
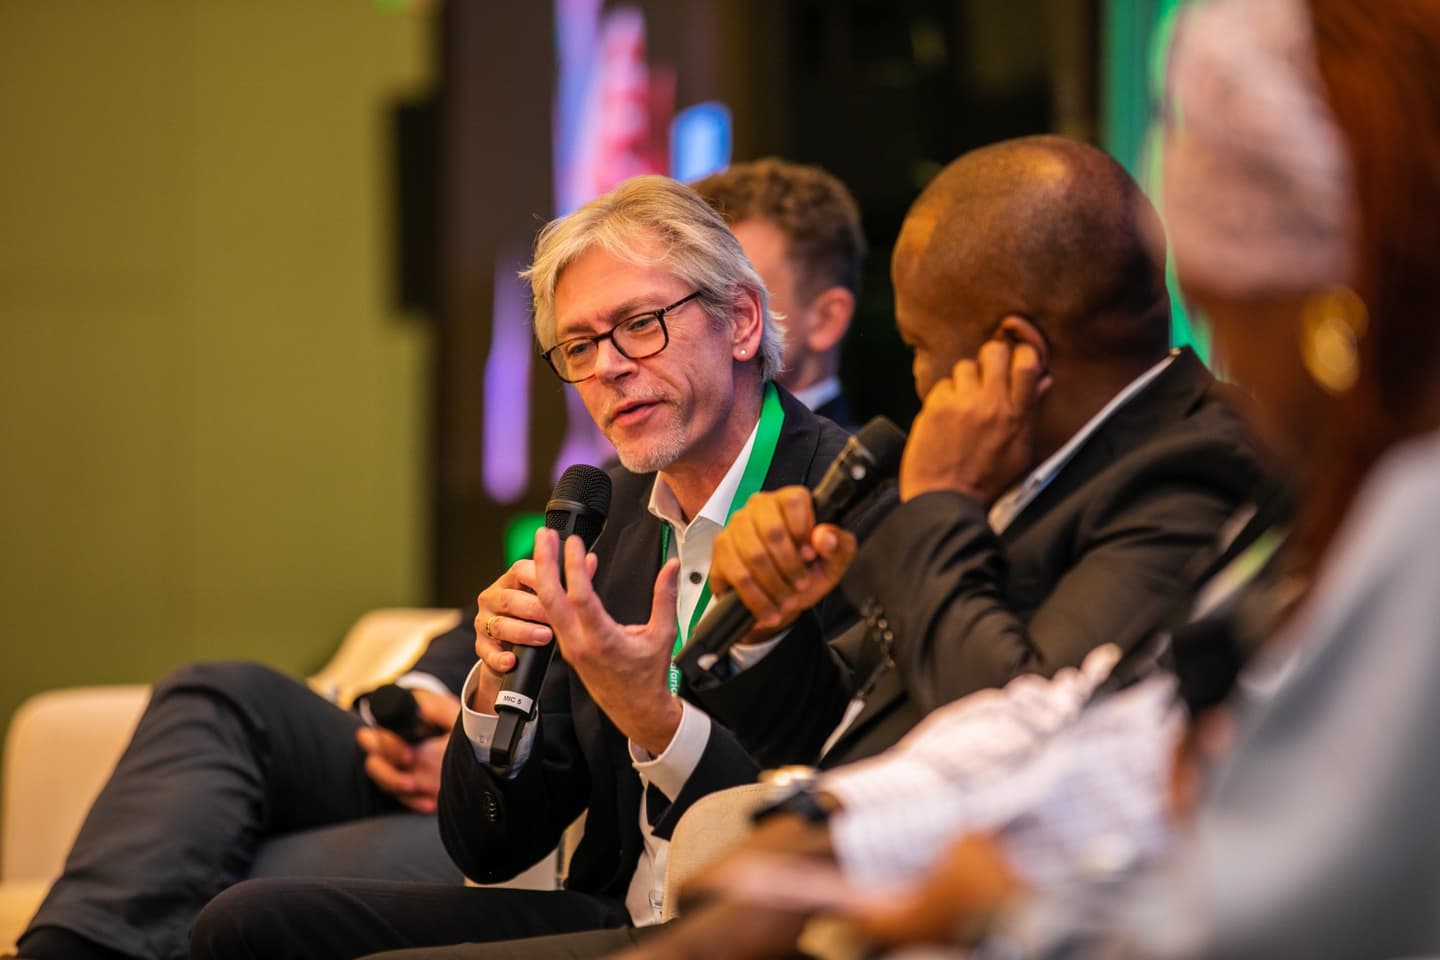
The issue came up during a panel discussion at the Safaricom Cybersecurity Summit 2026 in Nairobi. Dr Markus Leberecht, a principal engineer at Intel, cautioned that keeping AI systems on company premises does not automatically remove insider threats or guarantee that sensitive information is adequately protected. The location of a server matters, but the way data is accessed and processed also shapes the risk.
The security gap between storage and processing
Traditional data protection often focuses on two states. Encryption at rest protects stored information, while encryption in transit protects information moving between systems. When an application needs to process that information, however, it must use the data in a form that the computation can work with.
That processing stage can create a security concern, particularly when workloads handle confidential business records, personal information or sensitive models. Access controls, operating-system security and careful system configuration remain important, but they address different parts of the threat landscape.
AI systems add complexity because they may process large collections of data and connect to multiple services. An organisation needs to understand which data is being used, which components can access it and what happens when a workload runs on infrastructure managed by another party.
What confidential computing does
Confidential computing uses hardware-based security mechanisms to create protected environments for processing data. These environments are commonly known as trusted execution environments. Depending on the platform and implementation, they can help restrict access to data and code while a workload is running, including from some privileged software layers.
The protection is designed to complement other safeguards rather than replace them. Encryption at rest and in transit, identity management, least-privilege access, monitoring and sound application design remain necessary. The actual protection depends on the hardware, software stack, configuration and threat model.
For organisations using AI, the technology may be relevant when sensitive workloads run in shared or externally managed infrastructure, or when there is a need to limit access by components outside a protected environment. It is a technical option to evaluate against specific risks, rather than a universal requirement for every AI project.
Why on-premises AI is not a complete answer
Keeping models and data on premises can give an organisation more direct control over infrastructure and where information is stored. It does not, by itself, prevent an authorised insider from misusing access, stop compromised software from behaving maliciously or ensure that every connected application follows the organisation’s rules.
The same principle applies to cloud deployment. A cloud service can offer security controls and managed infrastructure, but customers still need to understand their responsibilities, configure access appropriately and review how data is handled. Neither deployment model removes the need for a clear security architecture.
Data classification is an important starting point. Organisations should identify which records are sensitive, determine which workloads may process them and set rules for who or what can access the information. They can then assess whether confidential computing, stronger identity controls, isolated workloads or other measures address the risks they have identified.
How organisations should assess the technology
Security and technology teams should begin with a defined use case rather than choosing a technology because it is associated with AI. They need to identify the assets to protect, the parties or software components they do not fully trust, the performance requirements and the consequences of a security failure.
They should also examine how protected workloads are deployed, monitored, updated and recovered. Technical safeguards work best when they form part of a broader system of governance, access control and incident response.
As businesses bring more sensitive information into AI workflows, the protection of data during processing deserves a place in security planning. Confidential computing offers one tool for that task, but its effectiveness depends on how it is implemented and combined with the rest of the organisation’s controls.
Follow Us


By George Kamau
I brunch on consumer tech. Send scoops to george@techtrendsmedia.co.ke