The Cognitive Ceiling of Declarative Cloud
Cloud infrastructure engineering has progressed through successive layers of abstraction. Metal hardware is giving way to virtual machines, virtual machines are evolving into flexible cloud primitives, and ad hoc manual provisioning is being replaced by Infrastructure as Code (IaC). Using Terraform, OpenTofu, Azure Bicep, and ARM templates, engineering teams created repeatable, state auditable, and version-controlled GitOps workflows. However, declarative IaC essentially answers only one static question: What infrastructure must be in place at deployment time?
Modern distributed systems expose the limits of this static paradigm. Today’s systems run across multi-region virtual networks, high throughput microservice meshes, bursting GPU clusters, and asynchronous event streams.
· Does progressive configuration drift or dynamic IAM role assignment create compliance risks?
· Why does p99 latency increase in distributed microservices when CPU usage shows a normal range?
· What operational measures should be taken now to prevent cascading failures?
A few months ago, our team at Victoria & Albert Museum encountered a classic cascading error when an update passed the staging phase, but during a sudden spike in traffic, our AKS cluster connection pools locked up. Our static Terraform configuration doesn't know what's happening at runtime. When such read increments occur, traditional infrastructure as code provides zero adaptation. The deployment pipeline stalled, Slack was flooded with threshold alerts, and we spent the next two hours on the triage bridge piecing together OpenTelemetry traces and crash guides to figure out what the problem was.
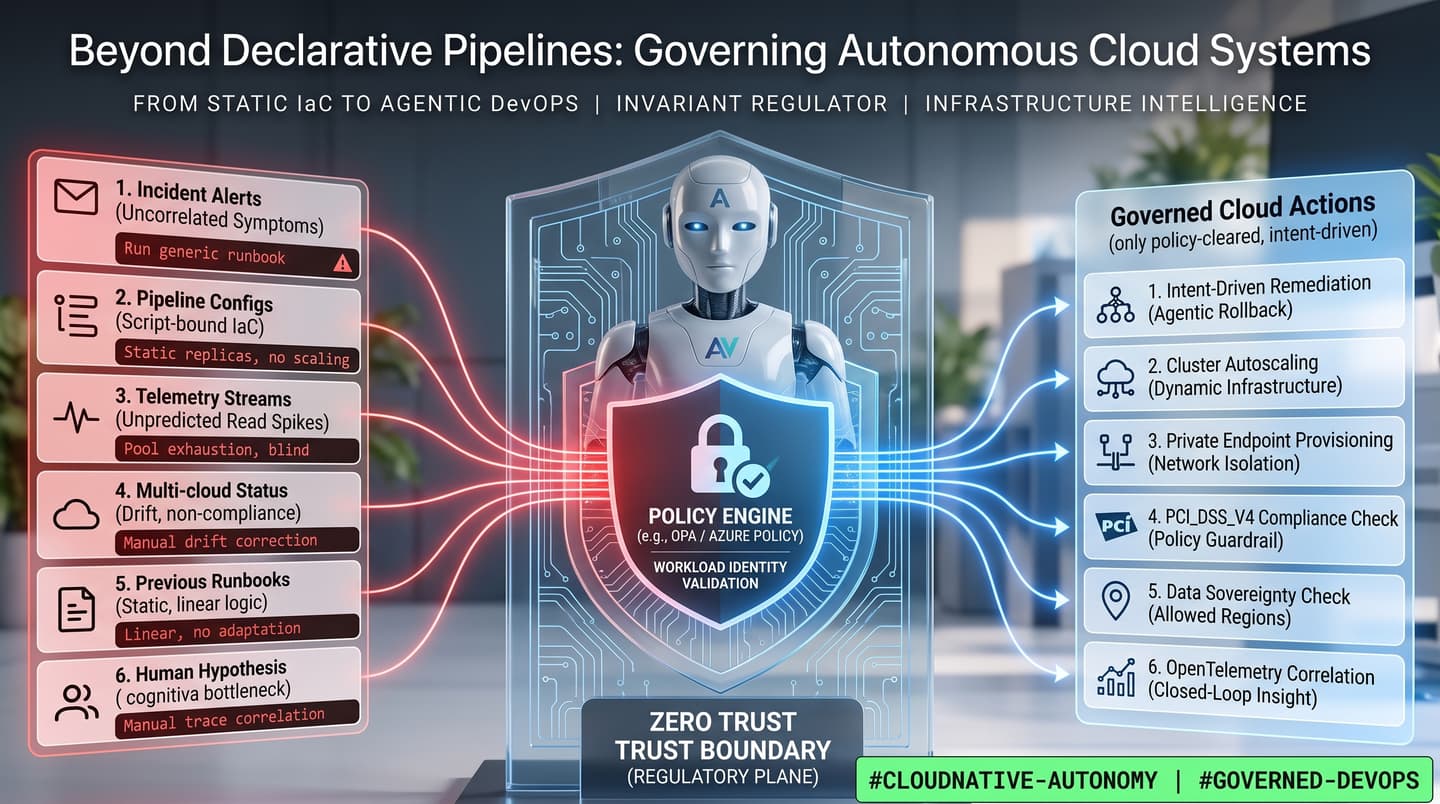
Relying solely on human cognitive bandwidth to maintain operational balance is not scalable. The industry must move beyond static, script-bound IaC to Infrastructure Intelligence and Agentic DevOps creating closed-loop, governed autonomous platforms.
The Closed-Loop Operational Architecture
Agentic DevOps does not grant unlimited large language models (LLMs) arbitrary management rights over cloud subscriptions. Rather, it embeds cognitive reasoning within policy boundaries.
Where traditional DevOps follows a linear delivery pipeline:

Agentic DevOps establishes a continuous, closed-loop feedback system:


- High-Cardinality Telemetry (Observation): The control plane uses Open Telemetry and Azure Monitor/Application Insights to collect metrics, distributed tracing, and structured logs.
- Topological Context Synthesis (Reasoning): When an exception occurs, autonomous agents query the enterprise context graph. The graph connects real-time Kubernetes/cloud topology, active dependency graphs, recent Git diffs, and historical postmortems. This contextual reasoning can distinguish whether delays stem from noisy neighbor resource starvation, repository deadlocks, or regressions introduced in recent releases.
- Structured Tool Orchestration (Decision): Agents use model context protocols (MCPs) or objective function calls to create deterministic action plans. Features like setting up read-only copies, adjusting the Pod's auto-scaling level.
- Invariant Policy Guardrails (Execution): Operational plans must pass through an immutable policy engine (eg Azure Policy, Open Policy Agent) before touching production. The policy layer enforces non-negotiable invariants like network boundaries, data location limits, maximum usage limits, and required loop-human approvals for destructive operations.
- Execution and Continuous Feedback (Verification): Execution uses declarative engines (Bicep, Terraform, Kubernetes API) as the execution layer. The platform monitors after-action telemetry to verify that the fix has returned the system to the target service level objective (SLO) and automatically reverts if non-compliance persists.
Architectural Evolution: From Manual Scripts to Autonomous Platforms
Moving through the maturity stages of cloud engineering changes how teams approach infrastructure, operational friction, and failure modes.
|
Architectural Dimension |
Traditional IaC & DevOps |
Platform Engineering (IDPs) |
Infrastructure Intelligence & Agentic DevOps |
|---|---|---|---|
|
Operational Interface |
Terraform / Bicep manifests, manual Bash scripts |
Self-service portals (Backstage), static Golden Paths |
Machine Readable Intent Specs Dynamic Tool Endpoints |
|
Execution Trigger |
Human PR merge or manual deployment script |
Developer-initiated catalog request |
Autonomous event triggers, continuous SLO feedback loops |
|
Incident Resolution |
Human SRE war rooms, manual metric correlation |
Pre-configured automated runbook scripts |
Agentic root-cause synthesis, self-healing remediation |
|
FinOps Management |
Retrospective monthly invoice reviews |
Static budget caps and resource tagging |
Real-time predictive right-sizing, dynamic capacity arbitrage |
|
Cognitive Load |
High; distributed across product teams |
Moderate; centralized in the platform team |
Low; the system independently maintains operational invariants |
Practical Enterprise Implementations
1. Agentic Incident Triage and Automated Rollback
Consider an enterprise microservices platform deployed on Azure Kubernetes Service (AKS), where an API update causes the thread pool to exhaust during heavy traffic.
Phase 1: Anomaly Ingestion
• Azure Monitor / Application Insights flags p99 latency spike from 35ms to 1,400ms on /checkout.
• Open Telemetry traces isolate dependency bottlenecks at the payment gateway pod boundary.
Phase 2: Contextual Synthesis
• Autonomous agent queries GitOps history: Commit `d8c3f1` deployed 8 minutes ago.
• Agent initiates MCP query against AKS control plane check for pod restarts and CPU limits.
• Root-cause determination: Upstream connection pool starvation due to missing timeout logic.
Phase 3: Remediation Formulation & Guardrail Check
• Agent prepares targeted actions: Canary rollback to commit `a1b9e4` + 10% reduction for non-critical traffic.
• Azure Policy / OPA Gate evaluates action: Rollback complies with safe deployment practices approved.
Phase 4: Execution & Closed-Loop Verification
• Agent calls deployment API rolling replacement to known-good baseline completes in 45 seconds.
• Telemetry confirms p99 latency stabilizes at 32ms synthetic health probes clear.
To illustrate how an autonomous agent interfaces programmatically with the cloud control plane rather than running raw bash commands, the platform exposes discrete remediation tools via the Model Context Protocol (MCP):
from mcp.server.fastmcp import FastMCP
from pydantic import BaseModel, Field

mcp = FastMCP("AKS-Auto-Remediation-Broker")

class RollbackRequest(BaseModel):
    deployment_name: str = Field(..., description="Deployment in AKS")
    namespace: str = Field(default="production", description=" AKS South")
    target_revision: int = Field(..., description="Stable restore")

@mcp.tool()
async def trigger_canary_rollback(req: RollbackRequest) -> str:
    """Invoked by LLM agent to execute a guarded rollback upon latency regression."""
    # This wraps the Kubernetes CoreV1/AppsV1 API
    return f"Rollback initiated for {req.namespace}/{req.deployment_name} to rev {req.target_revision}"
Phase 5: Automated Incident Documentation
• Agent compiles linked traces, topology maps, remediation log, and preventive recommendations into an engineering post-mortem PR for human architecture review.
2. Intent-Driven Azure Landing Zones
Enterprise Azure Landing Zones provide standardized governance, subscription architectures, and networking topologies. However, landing zone provisioning often stalls behind platform team ticketing queues.
An intelligent platform replaces static configuration requests with Intent-Driven Provisioning:
apiVersion: platform.enterprise.azure/v1alpha1
kind: WorkloadIntent
metadata:
  name: payments-processing-pipeline
spec:
  workloadTier: mission-critical
  intent: "Deploy high-throughput payment ingestion worker with private endpoints"
  complianceFramework: PCI_DSS_V4
  objectives:
    p99LatencyMs: 50
    availabilityTarget: "99.99%"
  networkIsolation:
    ingress: private-only
    hubSpokeRouting: enterprise-transit
  dataSovereignty:
    allowedRegions:
      - westeurope
      - northeurope
The platform's underlying agent analyzes this intent, selects compatible landing zone modules, generates fully validated Bicep/Terraform definitions, registers workload identities in Microsoft Entra ID, provides private DNS zones, and links back to a central log analysis workspace, eliminating manual coordination.
3. Machine-Readable Intelligent Golden Paths
Platform Engineering implements Golden Path-based templates that reduce developers' cognitive load. In an agent architecture, platform consumers are no longer just human engineers.
An internal developer platform (IDP) should expose a machine-readable schema, typed tool contracts and programming APIs, and a human-facing portal. Whether invoked by an application engineer through a CLI or by an autonomous agent via an MCP server, the platform applies the exact same security boundaries, Entra ID permissions, compliance validations, and audit tracking.
Security as the Control Plane for Autonomy
When designing our architecture, the biggest challenge we faced was not making the AI agent intelligent enough it was engineering deterministic control. In our architecture, we made a strict design choice: no autonomous agent is ever granted long-lived ambient administrative credentials or unrestricted subscription access. Instead, every agent operates under an ephemeral workload identity managed via Microsoft Entra ID and SPIFFE, with each action evaluated against hard policy-as-code guardrails before any production API call is allowed to execute.
Governed enterprise autonomy requires strict architectural guardrails:

Below is the invariant OPA Rego guardrail enforcing sandbox validation prior to any production cluster mutation:
package enterprise.agentic.guardrails

# Block any autonomous agent tool invocation that attempts non-sandboxed production mutation
default allow = false

deny[msg] {
    input.actor.type == "autonomous_agent"
    input.action == "cluster_remediation"
    input.target_environment == "production"
    not input.verification.policy_cleared
    msg := sprintf("Agent %v denied: Production mutations require pre-cleared sandbox verification.", [input.actor.id])
}

allow {
    count(deny) == 0
}
- Cryptographic Workload Identity: Autonomous agents must never use long-lived service master keys or persistent API secrets. Each agent runs with an isolated workload identity (using Microsoft Entra ID or SPIFFE/SPIRE) and receives short-lived, cryptographically verifiable tokens issued only for the context of the task.
- Just-In-Time (JIT) Least Privilege: By default, the operations agent has only read telemetry permissions. If the automated remediation plan requires privilege escalation (such as restarting an AKS deployment), privileges are immediately escalated through Privileged Identity Management (PIM) and expire immediately after the task is approved.
- Separation of Reasoning and Execution: The LLM inference layer never directly communicates with the hypervisor or cloud control plane. It only communicates with hard-coded MCP tool servers that validate input schemas, reject malicious prompt injections, and enforce structural boundaries.
- Immutable Audit Trails: Compliance requires full traceability. Platform registrations add only audit trails with triggering observability events, agent thought processes, explicit calls to MCP tools, and cryptographic confirmations from the policy engine.
Intelligent FinOps: Economics as a Dynamic Runtime Constraint
Traditional FinOps capabilities are retrospective: teams review cloud spend at the end of the month, identify deviations, and open Jira tickets asking developers to reduce over-estimated VMs. This model of manual review cannot keep up with the flexible, auto-scaling AI architectures.
Infrastructure intelligence integrates FinOps directly into the ongoing operations cycle:
- Predictive Resource Allocation: Machine learning models track temporary workload patterns and dynamically adjust Kubernetes Vertical and Horizontal Pod Autoscalers (VPA/HPA) ahead of expected traffic curves.
- Continuous Capacity Arbitrage: The platform identifies fault-tolerant, stateless processing queues and dynamically shifts execution to spot or preemptible instances. By monitoring cloud preemption signals, the system drains and reschedules pods onto reserved nodes before capacity evictions cause service interruptions.
- Accurate Unit Economics: By linking cloud billing exports directly to the OpenTelemetry tracking context, the platform can determine the exact infrastructure cost per unit.
The Evolution of the Cloud Engineering Role
Agentic DevOps does not replace cloud engineers, it increases their effect.
Previously, engineers spent much of their workday triaging, tweaking YAML configurations, investigating broken deployments, and performing routine maintenance tasks. As closed-loop platforms absorb the overhead of this operation, the engineering responsibilities shift to the design of a higher-leverage system:
Defining strategic platform architecture and machine-readable service boundaries.
- Codifying organizational invariants into Policy-as-Code frameworks.
- Designing deterministic agent guards, failure modes, and MCP tool limits.
- Design high-fidelity observability pipelines and context diagrams.
- Implementation of robust human-loop control models.
The main engineering question varies from:
"How to manually configure and patch this cloud infrastructure?"
to:
"How do you build a strong platform that securely and autonomously manages this infrastructure within proven business boundaries?"
The next frontier:
- Infrastructure-as-Code ensured reproducibility.
- Platform engineering delivered self-service velocity.
- Agentic DevOps introduces contextual reasoning.
- Infrastructure Intelligence delivers governed, resilient autonomy.
The future of cloud engineering will not be won by managing expanding catalogs of static configuration scripts or scaling human on-call shifts. It is a system that combines human strategic intent with autonomous execution to create self-healing, self-optimizing and secure platforms that enable autonomous enterprises worldwide.