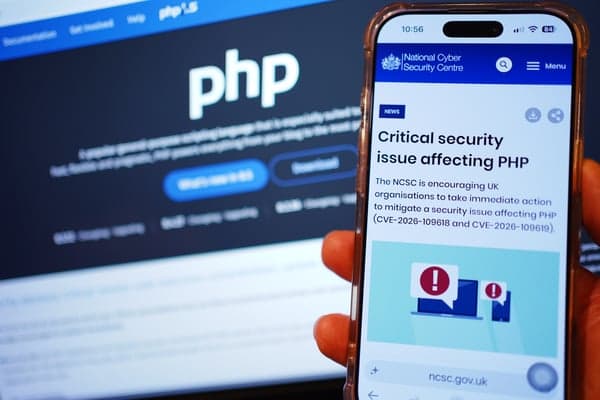
The PHP project released patches on Wednesday for two critical vulnerabilities that can allow unauthenticated remote code execution, sending organizations scrambling to update their systems or take websites offline.
The fixes are in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, the project said. The flaws are tracked as CVE-2026-109618 and CVE-2026-109619. PHP said all installations serving web requests are at risk, with the highest risk for those running Apache with mod_php. PHP underpins roughly 70% of sites worldwide.
The Cybersecurity and Infrastructure Security Agency (CISA) urged organizations to patch the flaws, which it calls "php2shell," and to prioritize internet-facing systems. Organizations that cannot update, or that use PHP 8.1 or earlier, should take PHP-based systems offline until they are patched, CISA said. The agency said it had not observed exploitation as of the alert's publication.
The NSA issued similar guidance, according to TechCrunch. The FBI's cyber division warned of the vulnerabilities on Wednesday as well, according to The Associated Press.
Some site owners pulled services offline, among them parts of Wikipedia and 4chan, according to Axios. The Associated Press said government services and websites in the U.K., Finland and Japan were disrupted. Some sites may remain down because patches differ across software and must be tested, according to The Associated Press.
Cloudflare CEO Matthew Prince wrote on X $TWTR that his company logged exploit attempts in the thousands during the 10 hours leading up to the announcement, a figure that has since grown to millions, according to Axios.
Accounts of how the flaws were found differ. Security firm Calif used OpenAI's GPT-5.6 Sol to find one of them, and Wiz separately used AI tools to find multiple vulnerabilities, according to TechCrunch. The Associated Press said people were the first to find the flaws, while AI agents assisted in working out the ways attackers might abuse them. The PHP Foundation said the flaws had been known since at least 2024 and that work on a fix stalled, according to The Associated Press.
The PHP security team had scheduled the release for 14:00 UTC and rated each flaw 9.2 on the CVSS v4.0 scale. It gave advance notice on Tuesday, and the project reserved the right to release earlier if details became public or exploitation appeared.
PHP said some settings reduce exposure for those who cannot update but do not make an installation safe. The project does not update PHP 8.1 and older, though its security team provided minimal source backports for PHP 7.4, 8.0 and 8.1.
In an informational advisory dated Friday, PHP suggested setting session.upload_progress.enabled=0 until the next bugfix release to guard against a separate, unlikely remote code execution vector, CVE-2026-115560.