
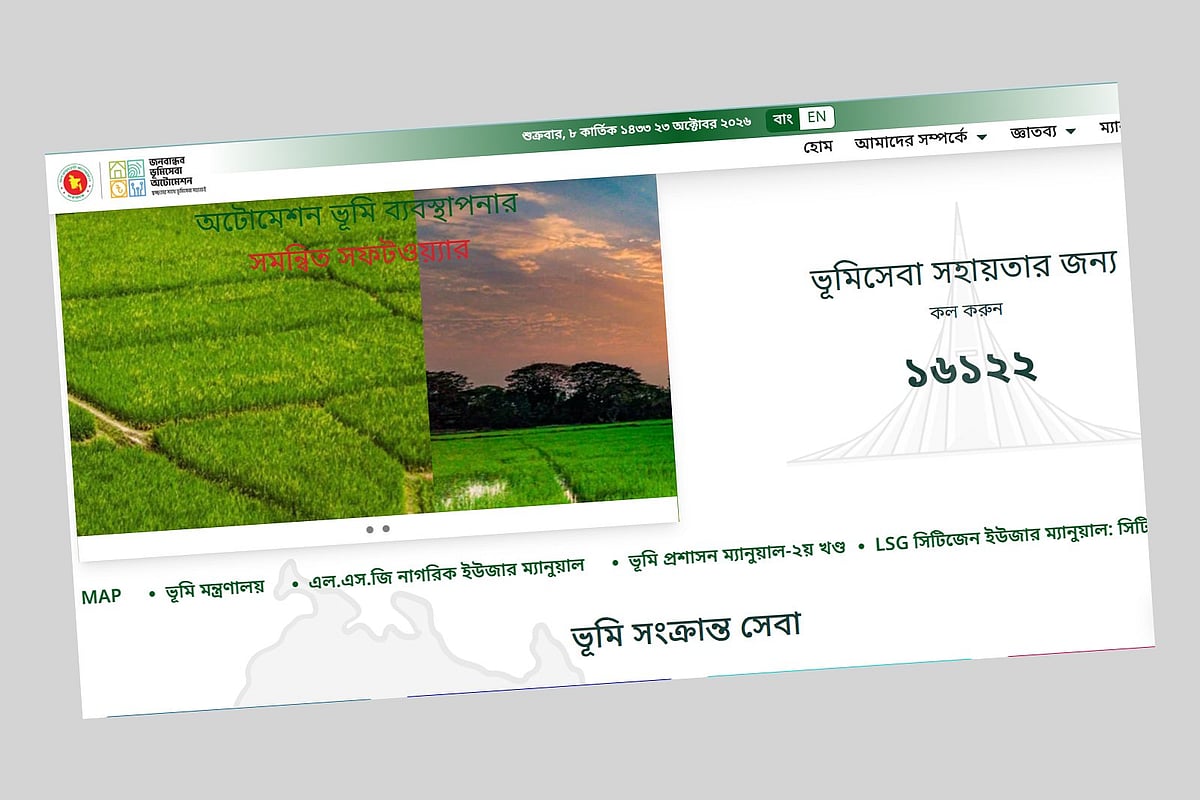
Around 300,000 people in Bangladesh use online services to register changes in land ownership, known as mutation, every month. But when people tried to access the e-mutation service yesterday, Saturday, they found it unavailable.
The government website land.gov.bd, which provides the mutation service, said it was being updated as part of an urgent cybersecurity alert issued by BGD e-GOV CIRT. As a result, land services were temporarily suspended.
Sources at BGD e-GOV CIRT, the agency responsible for overseeing cybersecurity for the government, said the alert had been issued after a security vulnerability in PHP was discovered worldwide.
The vulnerability has led to websites being taken offline around the world. Several websites in Bangladesh have also been temporarily shut down. Besides the land services website, these include Bangladesh Bank, several public and private banks, a private hospital and websites operated by other organisations.
The organisations have taken their websites offline to strengthen security. CIRT sources, however, said they had identified at least one hospital website that had been compromised.
None of the organisations has publicly acknowledged that its website was taken offline because of the PHP vulnerability, making it difficult to establish how many institutions in Bangladesh have been affected.
Asif Mahmud, deputy project director of the Land Management Automation Project, was asked whether the land services website had been taken offline because of the PHP vulnerability.
He told Prothom Alo that a technical issue was being checked in coordination with the Bangladesh Computer Council (BCC) as part of routine maintenance. The website had been taken offline temporarily for this purpose, he said.
He added that the site was scheduled to remain unavailable until noon on Sunday, but it would be restored earlier if the work was completed before then.
The notice on the website, however, says it is being updated in response to an urgent cybersecurity alert from BGD e-GOV CIRT.
What is PHP?
Many internet users may never have heard of PHP, yet they interact with it regularly. PHP, short for “PHP: Hypertext Preprocessor”, is a programming language that operates in the background, on the back end of websites.
A BBC report published on Friday, citing cybersecurity firm Wiz, said PHP powers around 70 per cent of websites worldwide. It was developed in the 1990s by Canadian programmer Rasmus Lerdorf, who made its source code publicly available. This allowed anyone to use it free of charge and modify it as needed.
The BBC report offered an example to explain how PHP works. Imagine ordering a burger at a restaurant. The server takes your order to the kitchen, where the burger is prepared and then brought to your table.
A website works in a similar way. When someone visits a website, PHP processes the request and generates the webpage accordingly. This happens almost instantly in the background, without the user noticing.
How was the vulnerability discovered?
The PHP vulnerability had existed for more than a decade without being detected. Last week, a team of researchers from two US cybersecurity companies identified it with the help of artificial intelligence (AI). The companies are Calif and Wiz, the latter being part of Alphabet, Google’s parent company.
Ryan Austin, a researcher at Calif who helped identify the flaw, told the BBC that it was the most serious vulnerability he had ever discovered.
Concern spread worldwide after news of the vulnerability became public. Fearing that hackers would exploit it to take control of websites and steal data, organisations began announcing precautionary shutdowns.
What has been the impact?
On 21 October, the US National Security Agency (NSA) warned all organisations using PHP. It said that if an organisation could not promptly fix the vulnerability, it should shut down the affected systems. The flaw could allow attackers to target databases directly.
According to the BBC, the alert disrupted various online services, including gaming platforms, government websites and online forums. Among the affected organisations was Wikimedia, the US-based non-profit that operates Wikipedia. As a precaution, it shut down several of its systems.
The UK government said on Thursday that some of its services might remain temporarily unavailable. It had shut down 32 websites as a precaution.
French telecommunications company Orange said it had restricted access to certain services worldwide while work to fix the vulnerability was under way. The Finnish government also took some websites and webpages offline. Some BBC pages were temporarily unavailable as well. The Dutch cybersecurity agency shut down its own website.
Amid the global disruption, a hacking group called “Siriusim” claimed to have gained access to confidential customer information at India’s State Bank of India (SBI), the country’s largest bank. On Friday, the state-owned bank acknowledged that customer data had been leaked.
Although hundreds of websites have reportedly been taken offline worldwide, no organisation has yet disclosed the total financial losses. Nor has the overall number of affected websites been confirmed. Guidance has been issued on how to improve security, including updating PHP to reduce the risk.
Websites shut down in Bangladesh
BGD e-GOV CIRT issued an urgent alert concerning PHP on Thursday, 22 October. It advised relevant organisations to identify PHP installations on their servers, check whether the versions in use were vulnerable and take the necessary security measures.
Bangladesh Bank took its website offline on Thursday following the alert. After the central bank’s move, several other banks also shut down their websites as a precaution. They include Agrani Bank, Janata Bank, IFIC Bank, Standard Islami Bank, SBAC Bank and Bengal Commercial Bank.
The banks said the measures were intended to avoid potential cyber risks and assess the security of their technology infrastructure. Their websites would be restored once the security checks and necessary measures had been completed.
Arif Hossain Khan, executive director and spokesperson for Bangladesh Bank, told Prothom Alo yesterday, “The website has been taken offline as a precaution. Officials from our technology department are working around the clock to ensure that no problems arise. Banking services have not been affected. The website will be restored once the risk has been reduced.”
BGD e-GOV CIRT sources said they had so far identified a private hospital website in Bangladesh as having been compromised. Although the hospital authorities had been informed, they had not contacted CIRT by Saturday evening. Maintenance work was under way on other government and private-sector websites that use PHP.
Nazmul Haque Khandoker, project director of CIRT, told Prothom Alo that after issuing an advisory on the PHP-related problem, the agency had notified organisations whose websites are hosted at the National Data Centre, as well as those covered by the National Portal Framework.
It had also alerted organisations designated as critical information infrastructure (CII). All organisations whose websites are built using PHP had been advised to take the necessary measures, he said.
‘Definitely a cause for concern’
Leaks of citizens’ personal information have become commonplace in Bangladesh. A report published in August by the technology research organisation TechGlobal Institute (TGI) said at least 68 data breaches had occurred in the country between January 2023 and May 2026. Of these, 36 involved government organisations and 32 involved private entities.
In February last year, data from the national identity card (NID) database was leaked. In 2023, information belonging to 50 million people was also exposed in an NID data breach. No action was taken in response to these incidents, the report said.
Against this backdrop, BM Mainul Hossain, a professor at the Institute of Information Technology at the University of Dhaka, was asked whether the PHP vulnerability posed a cause for concern in Bangladesh.
“Definitely. Imagine someone taking control of the land services server and altering land records, or gaining control of the income tax website and deleting its data. What would the consequences be?” he said to Prothom Alo.
Mainul Hossain said Bangladesh needed to remain vigilant, closely monitor the measures being taken and the recommendations being issued around the world, and ensure that adequate security measures were implemented at home.