AI compliance begins with understanding what a system does with information, who can access that information and how the organisation remains accountable for its use. For Kenyan businesses adopting AI tools, these questions arise when employees upload customer records to external services, software vendors introduce AI features into existing products or automated systems influence decisions about customers and staff.
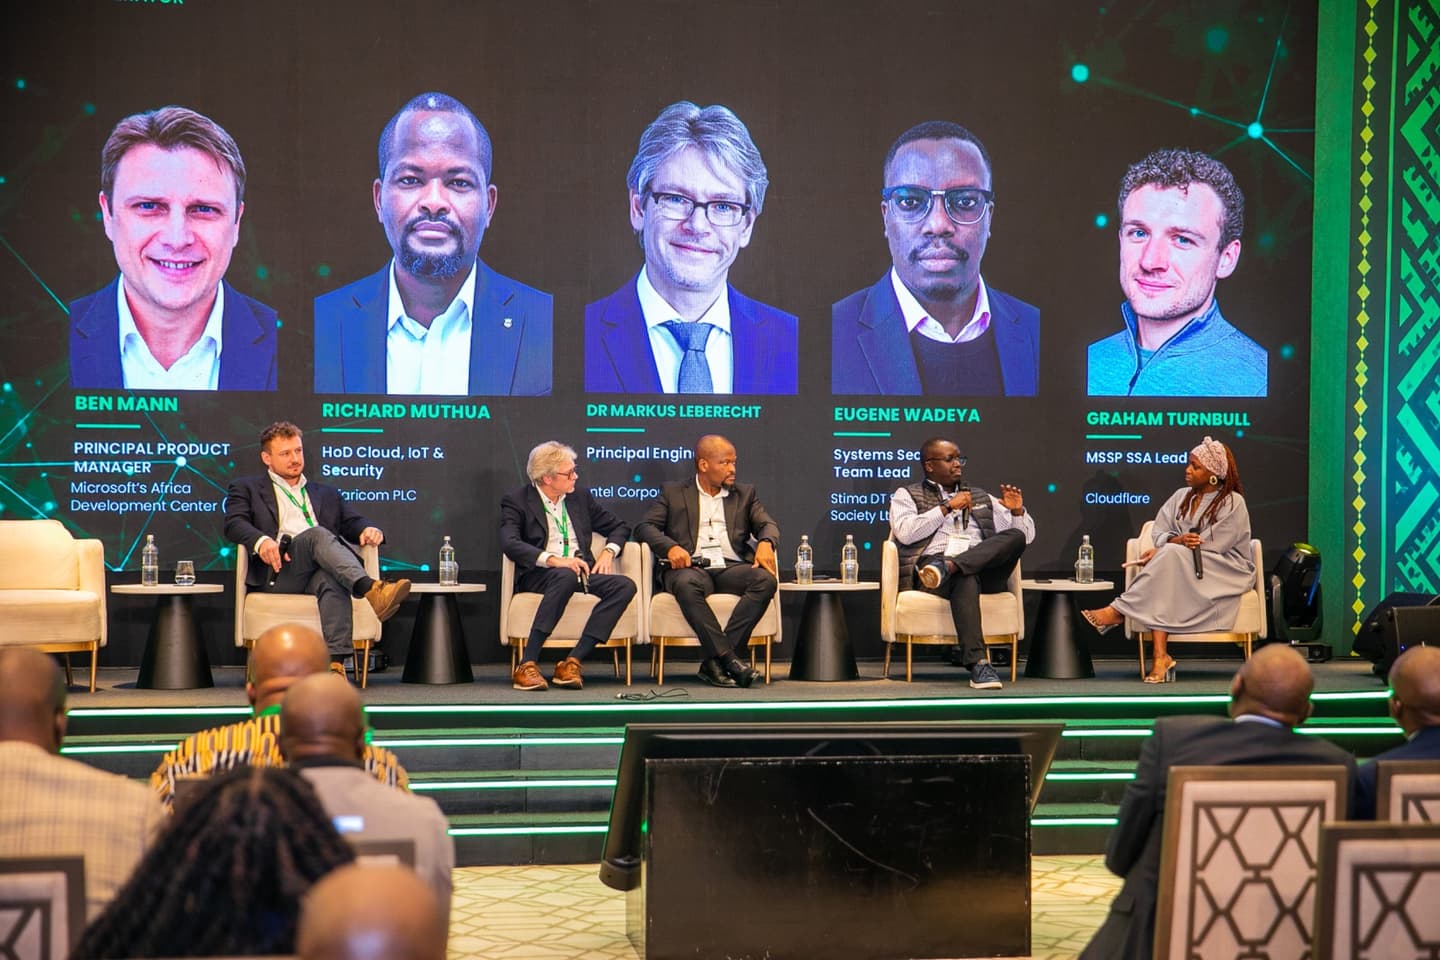
The issues were discussed during the Safaricom Cybersecurity Summit 2026 in Nairobi, where panelists highlighted data classification, processing locations, regulatory obligations and the need for organisations to understand which laws apply to their activities. Their advice points to a practical task for businesses: assess AI systems as part of existing data-protection, security and operational governance rather than treating them as isolated software purchases.
AI adoption creates data-governance questions
An AI application may process personal information, confidential business records or material supplied by customers. Depending on the product and its configuration, that information may pass through an external provider’s infrastructure or become accessible to different components of a wider service. Organisations need to understand these arrangements before deciding whether a tool is suitable for a particular task.
The risk depends on the data involved and the purpose of processing. Using AI to improve the wording of a public announcement raises different questions from using it to analyse employee records, evaluate loan applications or summarise confidential customer communications. A business should classify the information it handles and determine which uses are permitted before staff begin submitting sensitive material.
Why the location and use of data matter
Data may be stored in one jurisdiction, processed in another and accessed by a provider operating across several markets. These arrangements can affect contractual obligations, regulatory requirements and the organisation’s ability to respond to incidents or requests involving personal information.
Kenya’s Data Protection Act, 2019, provides a central legal framework for handling personal data, including requirements concerning lawful processing and safeguards for transfers outside Kenya. The obligations that apply depend on the circumstances, the information involved and the roles of the organisations processing it. Businesses should obtain appropriate legal advice when assessing complex or cross-border arrangements.
The European Union’s General Data Protection Regulation may also be relevant to some organisations, depending on its territorial scope and the activities concerned. A Kenyan company should not assume that GDPR automatically applies to every use of AI, nor should it assume that using an overseas service removes its responsibilities under Kenyan law.
How organisations can assess AI compliance
A practical review should begin with an inventory of AI tools and the business purposes they serve. For each tool, the organisation should identify the categories of information being processed, the people or systems with access, the service provider’s role and the relevant retention and security arrangements. The review should also establish whether information is transferred across borders and which legal requirements govern that processing.
Businesses should then assess the consequences of errors, unauthorised disclosure or inappropriate automated decisions. High-impact uses may require stronger oversight, more detailed risk assessment and clear routes for people to challenge decisions. Human review should be meaningful: a reviewer needs enough information and authority to question an output rather than simply approve what the system recommends.
Contracts and internal policies should align with the actual way a tool is used. Employees need clear guidance on approved applications, sensitive data, record retention and escalation procedures. Procurement and compliance teams should also review AI features introduced by existing suppliers instead of assuming that a previously approved product remains unchanged in its data practices.
What businesses should put in place before deployment
Organisations should assign responsibility for AI governance across the teams that manage technology, information security, legal compliance and business operations. They should document approved uses, restrict access according to job requirements, train staff and establish procedures for reporting incidents or reviewing problematic outputs.
The review should continue after deployment. Changes to a vendor’s features, a new category of data or a different business purpose can alter the risks associated with an AI system. Periodic assessments help ensure that the organisation’s controls remain appropriate as its use of the technology develops.
AI can support useful business processes, but responsible deployment requires organisations to understand the information their systems handle and the decisions they influence. Clear data governance, proportionate security controls and accountable human oversight give businesses a more reliable basis for adopting AI while meeting their legal obligations.
Real ESG impact doesn’t happen in panels alone, it happens in the rooms where financiers, operators, and policymakers actually align. Our GreenShift Forum 2026 cuts the noise, bringing together the people rewiring Africa’s sustainability and energy frameworks for one focused day in Nairobi. Secure your seat.
Go to TECHTRENDSKE.co.ke for more tech and business news from the African continent and across the world.
Follow us on WhatsApp, Telegram, Twitter, and Facebook, or subscribe to our weekly newsletter to ensure you don’t miss out on any future updates. Send tips to editorial@techtrendsmedia.co.ke