The South Korean government raised its cyber crisis alert for the private sector to the second of four levels after critical security flaws were found in PHP, the programming language widely used to build websites around the world. The government asked companies and institutions using PHP to apply security updates immediately.
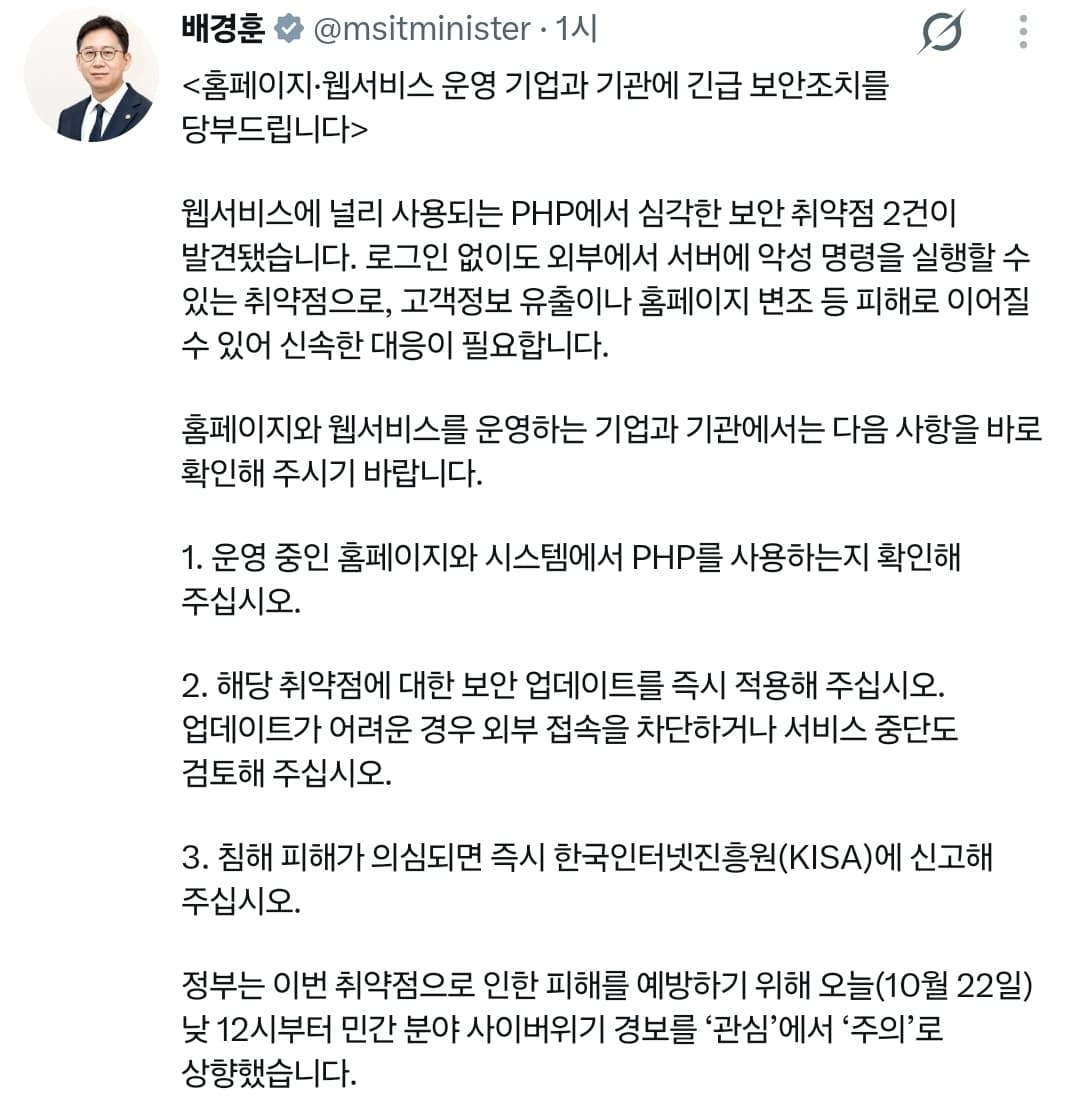
Bae Kyung-hoon, deputy prime minister and minister of science and ICT, wrote on X on the 22nd that the two serious vulnerabilities found in PHP allow an attacker to execute malicious commands on a server from outside without logging in. "To prevent damage, we are raising the private-sector cyber crisis alert from 'attention' to 'caution' as of noon," he said. The second-level alert triggers an emergency response system under which the Korea Internet & Security Agency and other bodies add incident-response staff and keep rapid-deployment teams on standby at all times.
PHP is a programming language used to build a wide range of web services, including homepages, online shopping malls, bulletin boards and administrator pages. Website-building tools widely used in Korea, such as WordPress and Gnuboard, also run on PHP.
The newly discovered vulnerabilities carry a high risk because an attacker can run commands of their choosing on a server by sending specially crafted requests over the internet, without any user ID or password. A successful attack could lead to serious damage, including leaks of customer data and website outages. Because the flaws lie in PHP itself rather than in individual website programs, even securely built websites can be affected.
The European Union's cybersecurity agency and national cybersecurity bodies in Britain, the Netherlands and Germany have rated the vulnerabilities as critical and recommended immediate updates. For systems that cannot be updated right away, they advised disconnecting them from the internet or suspending them temporarily. In Korea, KISA also issued a security update advisory on the 21st, the day the PHP development team released its patches.
Companies and institutions using PHP should check the PHP version on every website and system they operate and update to the latest version immediately. Web services must be restarted after the update for the fix to take effect.
PHP version 8.1 and older no longer receive official updates, so users must migrate to a supported newer version. "PHP may also be running on websites that were built long ago and left unmanaged, on shopping malls built by outside contractors and on equipment management screens, so a thorough check is needed," the ministry said. "Because information about the vulnerabilities has already leaked, even servers that have been updated should be checked for signs of intrusion, such as unusual access logs or the installation of webshell remote-control files, and any suspected breach must be reported to KISA immediately."
Small business owners who run websites through hosting providers can ask their provider whether the security updates have been applied. Many files circulating online as proof-of-concept attack code are fakes with malware hidden inside, so code from unclear sources should not be downloaded or run.
"We have urgently relayed the information to about 28,000 companies that have registered a chief information security officer, as well as to major information and communications infrastructure operators, companies certified under the Information Security Management System, web hosting firms, internet data centers and members of the Cyber Threat Alert System," the ministry said. "We are continuously monitoring attack trends in cooperation with the security industry at home and abroad." The government also plans to discuss security inspections and remedial requests for small and midsize enterprises with other ministries.
"From a corporate standpoint, the usual vulnerability management cycle of manual checks followed by patching within a few days cannot defend against these attacks," Bae said. "An automated response system is essential, including immediate blocking of internet-facing assets and preemptive application of web application firewall rule sets."