For most of its history, Cisco Systems Inc. won by building vertically integrated network products and asking customers to buy all of it. The company did very well with that model. Security, meanwhile, was something Cisco sold as a separate product line rather than something that was inherent to its infrastructure. Patching a core switch meant scheduling a maintenance window, crossing your fingers and hoping nothing broke.
Under Chief Product Officer Jeetu Patel, Cisco has moved away from that model and embraced openness. That’s why I found Cisco’s announcements at this week’s Open Compute Project Global Summit in San Jose more interesting for what they reveal about the company than for the products themselves.
As Mike Wheatley outlined in his SiliconANGLE post, Cisco rolled out a new pluggable optics form factor with Nvidia Corp., shipped its first Silicon One G300 systems, introduced the G302 top-of-rack chip and a new out-of-band management platform, and brought its Live Protect runtime security capability to SONiC. His post detailed the announcements, but it’s worth a deeper look at why these matter for artificial intelligence and what they say about a Cisco trying to be both open and secure, neither of which were strengths before Patel.
The network is now in the critical path of AI
During the event’s pre-briefing, Cisco Senior Vice President of Engineering Will Eatherton discussed the problem the company is trying to solve. A few years ago, a large training run used hundreds of graphics processing units. Today, the largest clusters use hundreds of thousands of GPUs. Cisco cited Epoch AI data showing that projects that once fit in one or two buildings now span campuses, metros and regions, largely because that’s where power and real estate are available.
This changes the role of the network. In a traditional data center interconnect, the wide-area network carries many small, independent flows, and a network hiccup affects a single application or user. In large-scale deployments, the network needs to “scale-across” and carry a small number of massive, synchronized flows between accelerators working on the same job.
As Rakesh Chopra, Cisco Fellow and senior vice president of silicon and systems architecture, explained on the call, scale-across puts the long-haul network “directly in line with the workload performance.” If a link slows down, GPUs sit idle, and idle GPUs are the most expensive waste in information technology today.
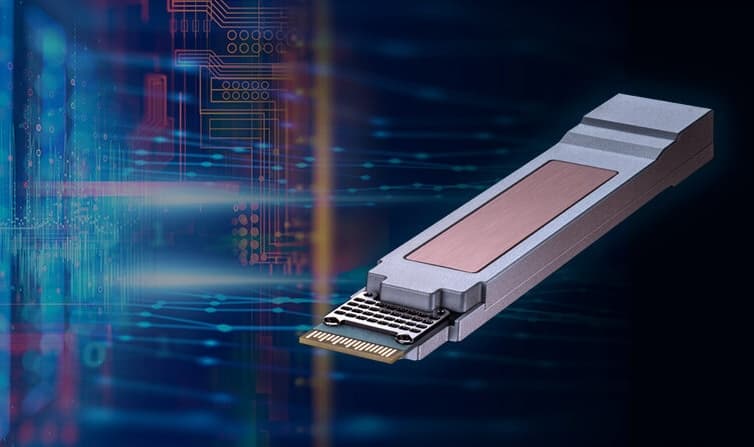
That’s the context for Cisco’s OCP news. The Ultra-Dense Small Form Factor Pluggable, or USFP (pictured), is the first pluggable module designed for 400-gigabit-per-lane signaling, delivering up to 12.8 Tbps and about four times the bandwidth density of today’s leading modules. The key word is pluggable.
Cisco’s optics team made a fair point on the call: the competing XPO approach requires liquid cooling, which no optic in the industry needs today, and it creates real headaches when handling, replacing and validating modules. Keeping the operational model familiar while doubling the lane rate is the kind of pragmatic engineering that speeds adoption.
Equally important, USFP is being standardized as a multisource agreement with TE Connectivity and Amphenol. Optics is one of the highest cost and supply-chain constraints in AI buildouts, and a multivendor spec should drive higher volumes, greater competition,and lower prices.
Open at every layer is a big shift for Cisco
Cisco used the phrase “open at every layer of the stack” throughout the briefing, and Eatherton was clear that this “is not just a SONiC story.” That spans P4 programmability at the chip level, Nvidia Reference Architecture compliance in systems, OpenZR+ in optics, a choice of SONiC, FBOSS, a custom NOS, NX-OS, or IOS XR, third-party controllers, and the CNCF-governed Cilium ecosystem at the Kubernetes layer.
Eatherton called SONiC a first-class network operating system at Cisco and admitted that is “unusual for Cisco in the context of our 20- or 30-year history.” SONiC was once viewed within Cisco circles as a threat, a way for hyperscalers to commoditize switching. Now Cisco offers community builds, custom builds using its software development kit, and a turnkey Cisco-validated version under the Nexus One controller. Though this may seem inconsistent with Cisco’s past strategy, it aligns with Patel’s commitment to make Cisco unrecognizable from what it was two years ago.
The openness also extends to Cisco. Intelligent Collective Networking, the G300 capability that detects remote congestion and link failures and signals back to the ingress leaf in hardware time, is being standardized by the Internet Engineering Task Force rather than kept proprietary. Five years ago, I’m not sure Cisco would have given away something it considers a competitive advantage.
Why the change? Because the customers driving AI infrastructure spending will not accept lock-in. Hyperscalers have built their own operating systems and controllers, and the more mature neoclouds are now closely examining SONiC. Cisco is betting it can win on silicon, optics, systems engineering and support while letting customers choose what runs on top. Microsoft running Silicon One P200 systems in production and Alibaba deploying its in-house router on the P200 at massive scale suggest that bet is paying off.
Being open doesn’t hurt Cisco; it expands its addressable market. A Cisco that requires its full stack can sell only to customers that want it. A Cisco that is open at every layer can sell silicon to one customer, optics to another, and validated SONiC to a third.
Security that keeps the network running
The announcement I believe is most underappreciated is Live Protect for Cisco SONiC. Cisco cited data showing that the mean time to exploit a vulnerability has dropped from about nine months to roughly 10 hours. Eatherton noted that attackers now feed newly published CVEs into large language models and attempt exploits within hours.
That creates an impossible situation for AI network operators. Patching a switch typically requires a reboot, and rebooting a switch in a fabric running a multiweek training job across thousands of GPUs is not something anyone wants to do on short notice. So operators either risk an outage or a breach.
Live Protect addresses this by applying a “shield,” a compensating control, to the live system at the kernel level without downtime or rebooting. The switch is protected immediately, and the patch can be applied during a planned window. Cisco has had this capability in NX-OS for about a year and is bringing it to Cisco-validated SONiC on Nexus One, with availability targeted for the second quarter of 2027.
There are two important aspects to this. First, it reflects Cisco’s move to build security into the infrastructure rather than bolt it on, a shift the company has long discussed but often struggled to deliver, and now appears to be delivering. Second, it brings Cisco’s security engineering to an open operating system.
One criticism of SONiC has been its lack of enterprise-grade security and support, and closing that gap makes SONiC viable beyond the largest hyperscalers. With line-rate, quantum-resilient encryption built into the P200, Cisco now has a security story for AI infrastructure it simply didn’t have a few years ago.
Final thoughts
AI infrastructure is being built under conditions that punish both lock-in and downtime. Cisco’s OCP announcements address both issues and show that the company understands the AI market won’t be won the way the enterprise campus was.
For infrastructure leaders building AI capacity, my advice is to evaluate the network on job completion time and GPU utilization, not port speeds alone; to require open interfaces at the operating system and controller layers so you keep your options; and to ask every vendor how it will protect production fabrics during the hours between a CVE disclosure and a maintenance window.
Zeus Kerravala is a principal analyst at ZK Research, a division of Kerravala Consulting. He wrote this article for SiliconANGLE.
Image: Cisco
A message from John Furrier, co-founder of SiliconANGLE:
Support our mission to keep content open and free by engaging with theCUBE community. Join theCUBE’s Alumni Trust Network, where technology leaders connect, share intelligence and create opportunities.
- 15M+ viewers of theCUBE videos, powering conversations across AI, cloud, cybersecurity and more
- 11.4k+ theCUBE alumni — Connect with more than 11,400 tech and business leaders shaping the future through a unique trusted-based network
SiliconANGLE Media is a recognized leader in digital media innovation, uniting breakthrough technology, strategic insights and real-time audience engagement. As the parent company of SiliconANGLE, theCUBE Network, theCUBE Research, CUBE365, theCUBE AI and theCUBE SuperStudios — with flagship locations in Silicon Valley and the New York Stock Exchange — SiliconANGLE Media operates at the intersection of media, technology and AI.
Founded by tech visionaries John Furrier and Dave Vellante, SiliconANGLE Media has built a dynamic ecosystem of industry-leading digital media brands that reach 15+ million elite tech professionals. Our new proprietary theCUBE AI Video Cloud is breaking ground in audience interaction, leveraging theCUBEai.com neural network to help technology companies make data-driven decisions and stay at the forefront of industry conversations.