Singapore's response to major telecom cyberattack highlights value of constant monitoring and rapid intervention as Korean banks confront security breaches
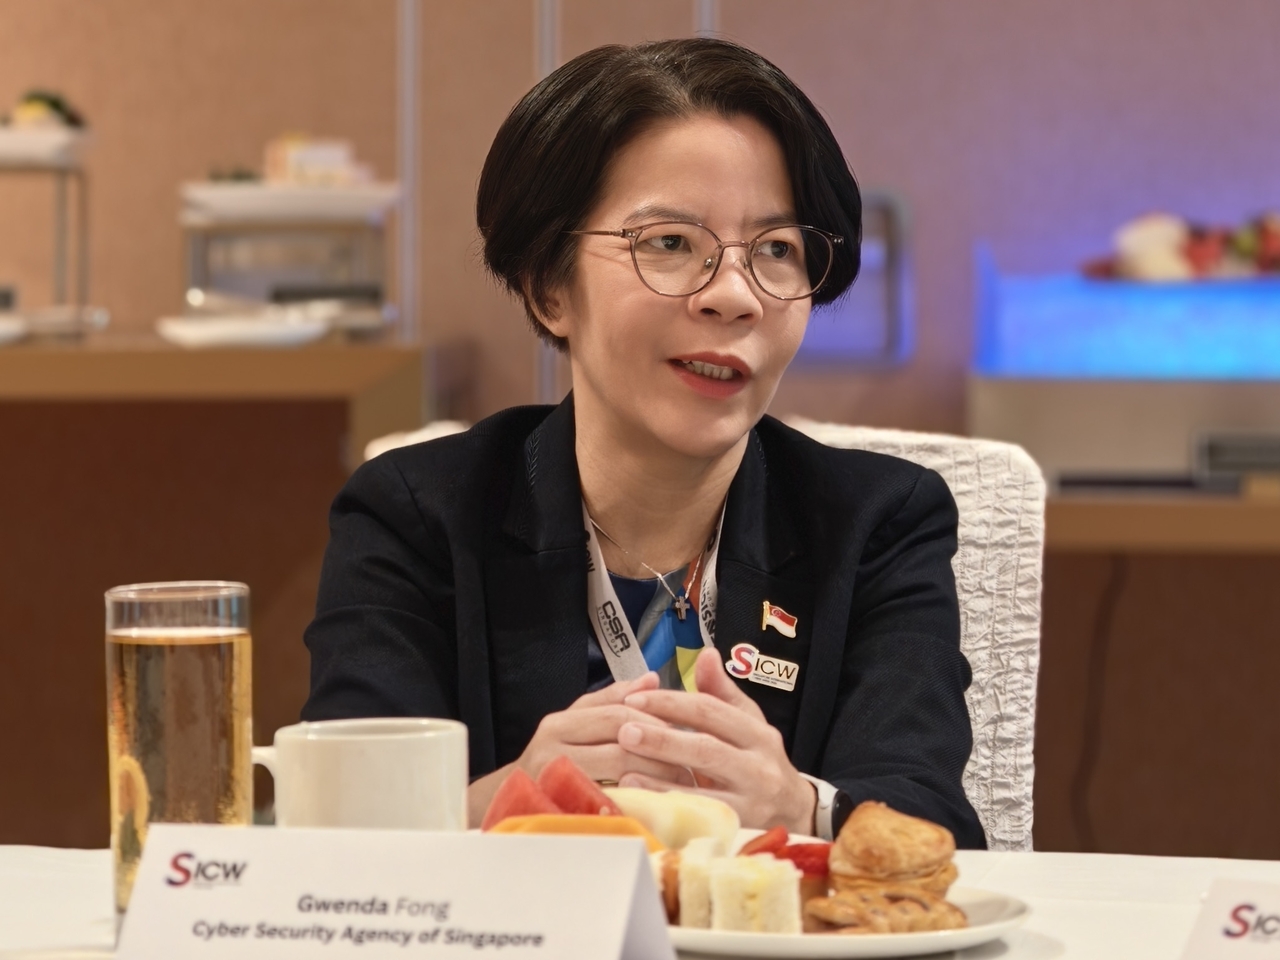
SINGAPORE — Singapore's cybersecurity chief called for continuous monitoring and closer cooperation between governments and businesses Thursday, offering insights as South Korea confronts a series of cyber intrusions targeting financial institutions.
Gwenda Fong, chief executive of Singapore's Cyber Security Agency, said organizations must move beyond a "compliance-based mindset" centered on periodic security checks, particularly as artificial intelligence enables hackers to exploit vulnerabilities faster and at greater scale.
Speaking at a media roundtable during Singapore International Cyber Week 2026, Fong emphasized "continuous monitoring" and coordinated responses involving regulators and critical infrastructure operators.
Her remarks came a day after South Korea's Financial Services Commission disclosed cyber intrusions at 16 financial companies. A separate inspection of 555 firms found security weaknesses at 130, including outdated software, inadequate access controls and insufficient monitoring.
The FSC also acknowledged a gap in its financial-sector threat-sharing platform, FIRST. While the system distributes intelligence collected by regulators and the Financial Security Institute, threats detected independently by individual financial companies have not been shared through it.
The commission plans to expand the platform to enable industry-wide sharing of such information.
Beyond core systems
Recent Korean bank breaches also exposed vulnerabilities in applications outside core transaction systems.
Hackers accessed customer information through applications used by employees and loan brokers at Shinhan, KB Kookmin and Hana banks.
According to incident reports obtained by Korean lawmakers, Shinhan took approximately 15 hours to detect an intrusion, compared with 68 hours at KB Kookmin and 42 hours at Hana.
Mike Yeh, Microsoft's vice president and deputy general counsel for customer security and trust, told The Korea Herald that large organizations often rely on customized software developed by outside contractors, sometimes through "independent projects that may not be supported anymore."
He urged banks to scrutinize software suppliers and restrict employee access privileges.
Singapore has strengthened oversight of similar vulnerabilities.
Goh Jing Xian, assistant director at CSA's Communications and Engagement Office, said amendments to the country's cybersecurity legislation reflected growing risks from interconnected systems, including applications "outside of that main core system."
The amendments, implemented in October 2025, expanded reporting obligations for designated critical infrastructure operators to cover certain suspected advanced persistent threat attacks and disruptions involving noncore systems. Specified incidents must be reported within two hours of becoming known.
Coordinating a national response
Singapore's government-industry coordination was tested during a major cyberattack targeting its four leading telecommunications operators last year.
When hackers linked to advanced threat group UNC3886 infiltrated the operators, CSA coordinated a response involving more than 100 government cybersecurity specialists working alongside the companies.
"We have the mandate, and we were driving the operation," Fong said, describing cooperation with telecommunications regulator IMDA and the affected operators.
The operation lasted more than 11 months. Although attackers penetrated some systems and stole limited technical information, authorities reported no disruption to telecommunications services or evidence of sensitive customer records being stolen.
Singapore is now expanding its National Cybersecurity Command Centre to integrate intelligence from multiple sources, identify vulnerable systems and coordinate responses to major incidents.
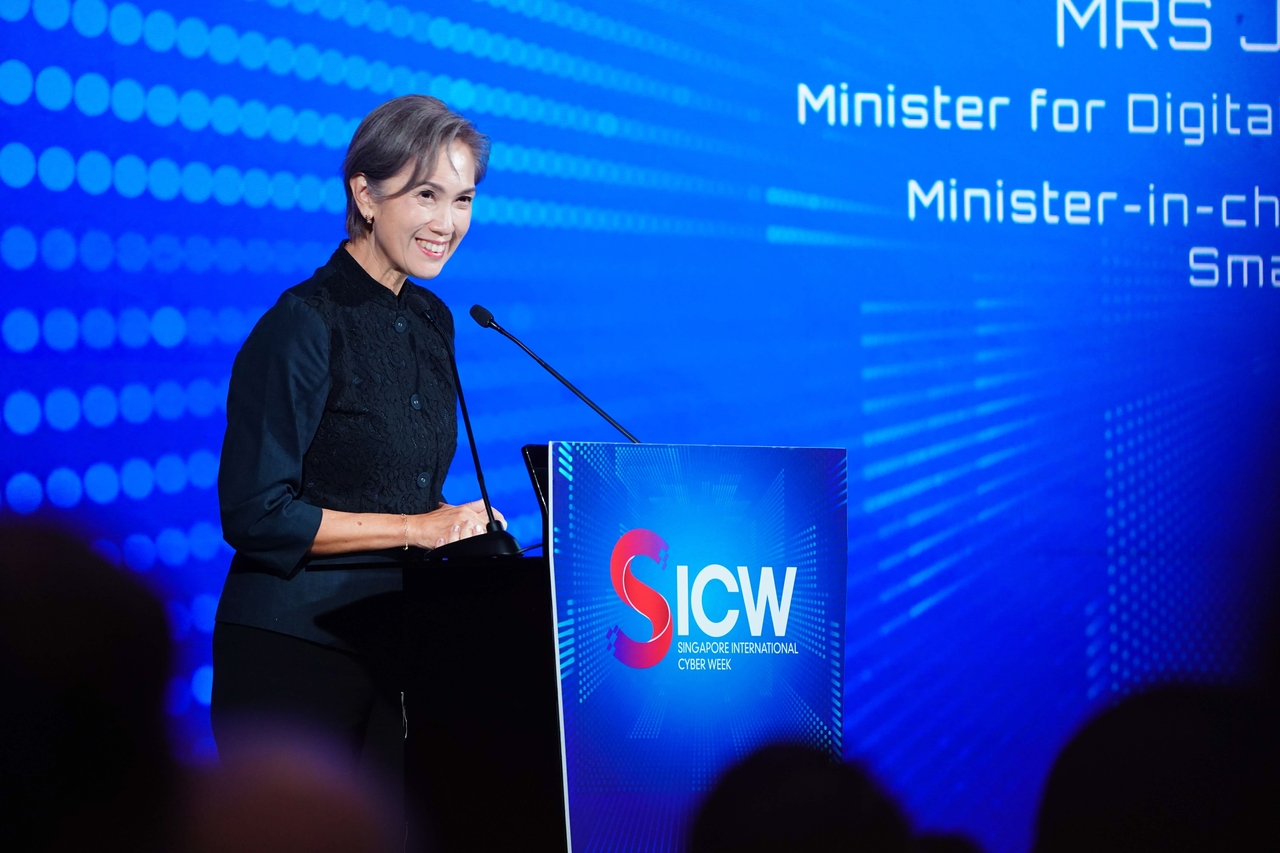
Businesses hold "unique, and frankly, essential insights on the threat landscape which most governments do not have visibility over," Singapore's Minister for Digital Development and Information Josephine Teo said in her opening address Monday.
For Korea, which already operates national and industry-specific cybersecurity systems, the immediate priority is closing gaps in threat sharing and monitoring.
Alongside expanding FIRST, Korean regulators plan to strengthen oversight of externally accessible systems and increase executive accountability for security weaknesses.
mjh@heraldcorp.com