I try not to write too many doom-and-gloom cybersecurity stories, but this week's vulnerabilities involving PHP are too big to ignore.
With the help of AI, PHP flaws that had been lying dormant for years were dredged up and exploited, resulting in parts of the internet going dark as IT experts attempted to fix the problem.
Although your Windows PC isn't in the direct line of fire this time, the sheer speed and ability of AI when it comes to discovering (and exploiting) flaws shouldn't go unnoticed.
I've put together this guide to help you be proactive rather than reactive towards whatever security crisis comes next.
ELI5: What's actually happening with PHP and the internet?
PHP is a programming language that's been around for more than three decades, and it quietly runs a large portion of the internet. Nearly 70% of websites with a known server language use PHP, including WordPress, Yahoo, Etsy, and Wikipedia. To say it's important is an understatement.
This week, two serious PHP security flaws known as "PHP2Shell" were made public. The exploits essentially allowed bad actors to take over servers and steal data. Once this news was public, countless bad actors began directing AI at the vulnerabilities.
The reaction? Some governments pulled their websites down to wait for a fix. IT teams worked countless hours to patch holes. Cloudflare fended off thousands of attempts to exploit the bugs, even before they were publicly announced.
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.October 22, 2026
The PHP Foundation released a patch on October 21, but it's only targeted at newer versions of PHP. There are countless millions of websites and servers running older versions of PHP that didn't get the fix (and may never be secure again).
Is PHP2Shell a one-time incident?
To give you an idea of what we're heading into (and not just in the middle of), Dan Lorenc, CEO of Chainguard, shared on LinkedIn a tale of his journey to find PHP vulnerabilities.
His team had the PHP news early, and it attempted to independently discover the vulnerability. All it took was a prompt for their frontier model to "find bad vulnerabilities in PHP" for this to happen.
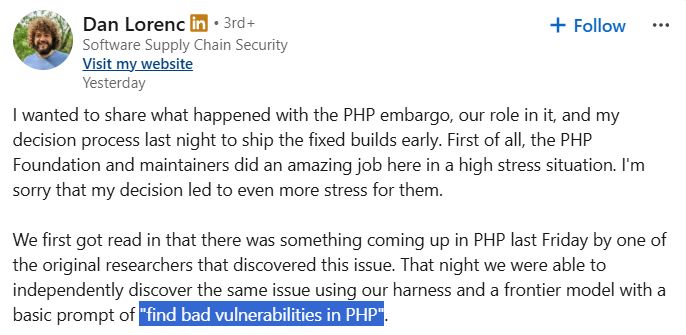
No special AI voodoo. No deep knowledge of security systems. Just a powerful AI with a simple command. As Lorenc points out, "This is unfortunately the new normal for the industry."
I hate to fearmonger, but I'd rather help get you ahead of the next security flaw than pretend everything will work out fine.
Should you be concerned about PHP vulnerabilities?
There's no reason for the average Windows PC user to panic, but you should be aware of what's going on. Being proactive is the best line of defense.
PHP runs on servers, not your desktop or laptop PC, so ordinary users don't need to rush to patch their apps or browsers. However, if you use a website that's now vulnerable, personal information could be exposed.
What to do right now to protect yourself
As seemingly the entire internet goes into high-alert mode, there are three quick tips every regular PC user should be using to protect themselves against attacks.
- Don't enter your credentials on websites that appear to be broken.
- Keep an eye on your email inbox. Vulnerabilities like this often lead to spam and phishing emails. Don't download shady files or visit links you didn't expect to see.
- Keep an eye on your bank statements for any shady activity.
These three tips will get you started, but there's a lot more you should be doing in order to prepare for the next big vulnerability.
How to prepare for the next big vulnerability
We're now entering an era of cybersecurity where you can assume that at some point you will be attacked. Your goal isn't to fend off every attack, but to make the fallout as easy to deal with as possible.
- Use a password manager. Give each account a unique, complicated password.
- Use an authenticator app or passkeys wherever possible. Two-factor authentication via SMS is becoming increasingly risky.
- Keep your PC updated and Windows Security enabled.
- Enable activity alerts from your banking apps.
- Set up a new email address for anything financial.
- Back up your data offline.
- Update your Wi-Fi router's firmware.
- Retire older hardware and devices that no longer receive security updates.
- Remain vigilant.
The bottom line
AI is now able to find security flaws much faster than humans are able to fix them, and the PHP2Shell fallout from this week is very likely only the beginning of a wave of critical security issues that threaten the foundation of the internet.
It's not up to you or me to stop the next problem, but it is up to us to ensure that we mitigate risks.
Join us on Reddit at r/WindowsCentral to share your insights and discuss our latest news, reviews, and more.