
The PHP Foundation runs on about $974,000 a year, with one full-time employee looking after a language behind most of the web.
Two critical PHP flaws sparked a worldwide patching frenzy this week.
One full-timer and 14 contractors keep the language going
“We have one full-time staff member (that’s me) and 14 mostly part-time contractors,” Executive Director Elizabeth Barron said Friday in an interview. The board of the foundation is unpaid, and the money comes from grants and donations.
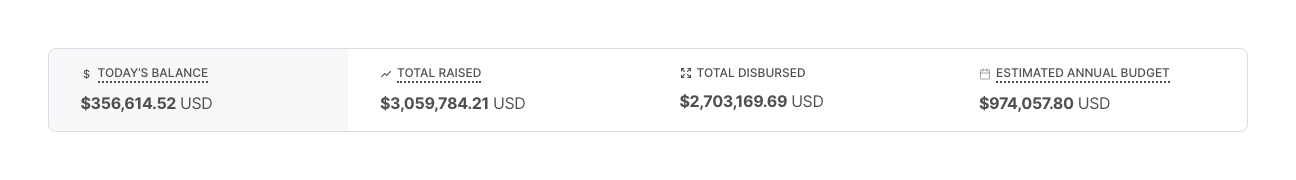
The foundation’s Open Collective page shows its yearly budget as $974,057.80. The foundation has raised $3.06 million since its launch in late 2021, spending $2.70 million.
With that budget, the $356,614.52 left over will cover expenses for four months. It shows that 1,927 people have donated and that 340 people have made monthly pledges worth ~$9,416 in total.
Barron said that in a year, the proposed changes to PHP code have almost doubled, and contributors have not kept up. Every submission and bug report still needs to be checked out by real people with experience.
AI helped researchers detect the two flaws that had been in the PHP code for a decade, and it makes programmers faster, Barron said.
AI also adds review burden to maintainers. She called the programming language badly underfunded, given how much companies and governments rely on PHP.
Barron saw no sign hackers got into patched sites
Since December 2021, Automattic is the biggest backer at $762,500. JetBrains at $476,670.
Sovereign Tech Fund is at ~$214,115. The Linux Foundation is at $183,500.
Smaller amounts are supplied by Private Packagist, Craft CMS, Cybozu, and Tideways. Zend by Perforce has given $56,000 and GoDaddy $48,000.
Chainguard Team has contributed $50,000 since October 21, the day PHP released its patches.
The foundation states on the page that it pays developers to work on the PHP language.
The largest tagged expense category is core developer work. It took 227 payments totaling ~$1.11 million out of 526 paid expenses.
PHP issued patches for CVE-2026-109618 and CVE-2026-109619 on October 21, both with a severity rating of 9.2 out of 10, Cryptopolitan reported. The pair, dubbed PHP2Shell, could allow attackers to execute code without logging in.
Wiz showed the flaws can also spill passwords and API keys from memory. PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 are the fixed releases.
Cloudflare registered millions of exploit attempts, and the government websites in Finland, the Netherlands and France went offline temporarily. The foundation works with OpenAI, Wiz and Calif to fix things.
Barron said there was no evidence hackers exploited the flaws prior to their disclosure or on patched sites.
This open-source language, which is over 30 years old, is employed on 69.3% of websites where the server-side language is known.
If you're reading this, you’re already ahead. Stay there with our newsletter.