A new coalition of nine blockchain organizations is tackling a problem that could eventually put roughly 6.4 million bitcoin at risk, including an estimated 1.1 million BTC associated with Satoshi Nakamoto. Launched this week, the Quantum Alliance wants to establish common security standards before powerful quantum computers can crack the digital signatures protecting cryptocurrency wallets. The threat isn’t here yet, but preparing for it could take years.
Key Takeaways
- The Quantum Alliance launched Oct. 15 with nine organizations working on shared security standards.
- Roughly 6.4 million BTC, including Satoshi-era coins, face potential exposure to future quantum attacks.
- Bitcoin’s biggest hurdle is upgrading wallets and protecting coins whose owners can no longer move them.
Nine Blockchain Organizations Unite as Quantum Threat Looms
Nearly one-third of Bitcoin’s supply could eventually become vulnerable to quantum computers, and a new industry coalition wants to get ahead of the threat. The Quantum Alliance, launched Oct. 15 in Lisbon, brings together nine blockchain organizations to establish common standards for protecting cryptocurrency networks, wallets, and infrastructure.
Its founding contributors estimate that roughly 6.4 million BTC, including coins associated with Bitcoin creator Satoshi Nakamoto, have already exposed the public keys that sufficiently powerful quantum machines could exploit. There’s one important catch. Nobody has built a quantum computer capable of pulling off such an attack.
Why 6.4 Million Bitcoin Are in the Crosshairs
The problem comes down to how Bitcoin protects ownership. Bitcoin wallets use digital signatures to prove that someone has permission to spend their coins. When certain wallets make transactions, they reveal public keys that remain permanently visible on the blockchain.
Today’s computers cannot realistically work backward from those public keys to discover the corresponding private keys. But sufficiently advanced quantum computers running a mathematical technique called Shor’s algorithm could potentially crack that protection.
The Quantum Alliance estimates that approximately 6.04 million to 6.4 million BTC are already exposed in this way, representing roughly 30% of Bitcoin’s total supply. An estimated 1.1 million BTC associated with Satoshi Nakamoto’s early holdings fall within the broader discussion of potentially vulnerable coins. That doesn’t mean anyone can steal those funds today. The danger depends on quantum computers becoming powerful and reliable enough to break the cryptography.
Google Research Adds Pressure to the Quantum Countdown
The heat is on as researchers continue to revise estimates of the computing power needed to threaten Bitcoin. On Thursday, Google Quantum AI revealed a breakthrough using its Willow quantum processor, demonstrating a technique called “magic state cultivation” that reduced errors by a factor of 40. The researchers also achieved 99.99% accuracy in specialized quantum states essential for building powerful, reliable quantum computers. The findings mark another step toward machines capable of eventually threatening Bitcoin’s cryptographic security.
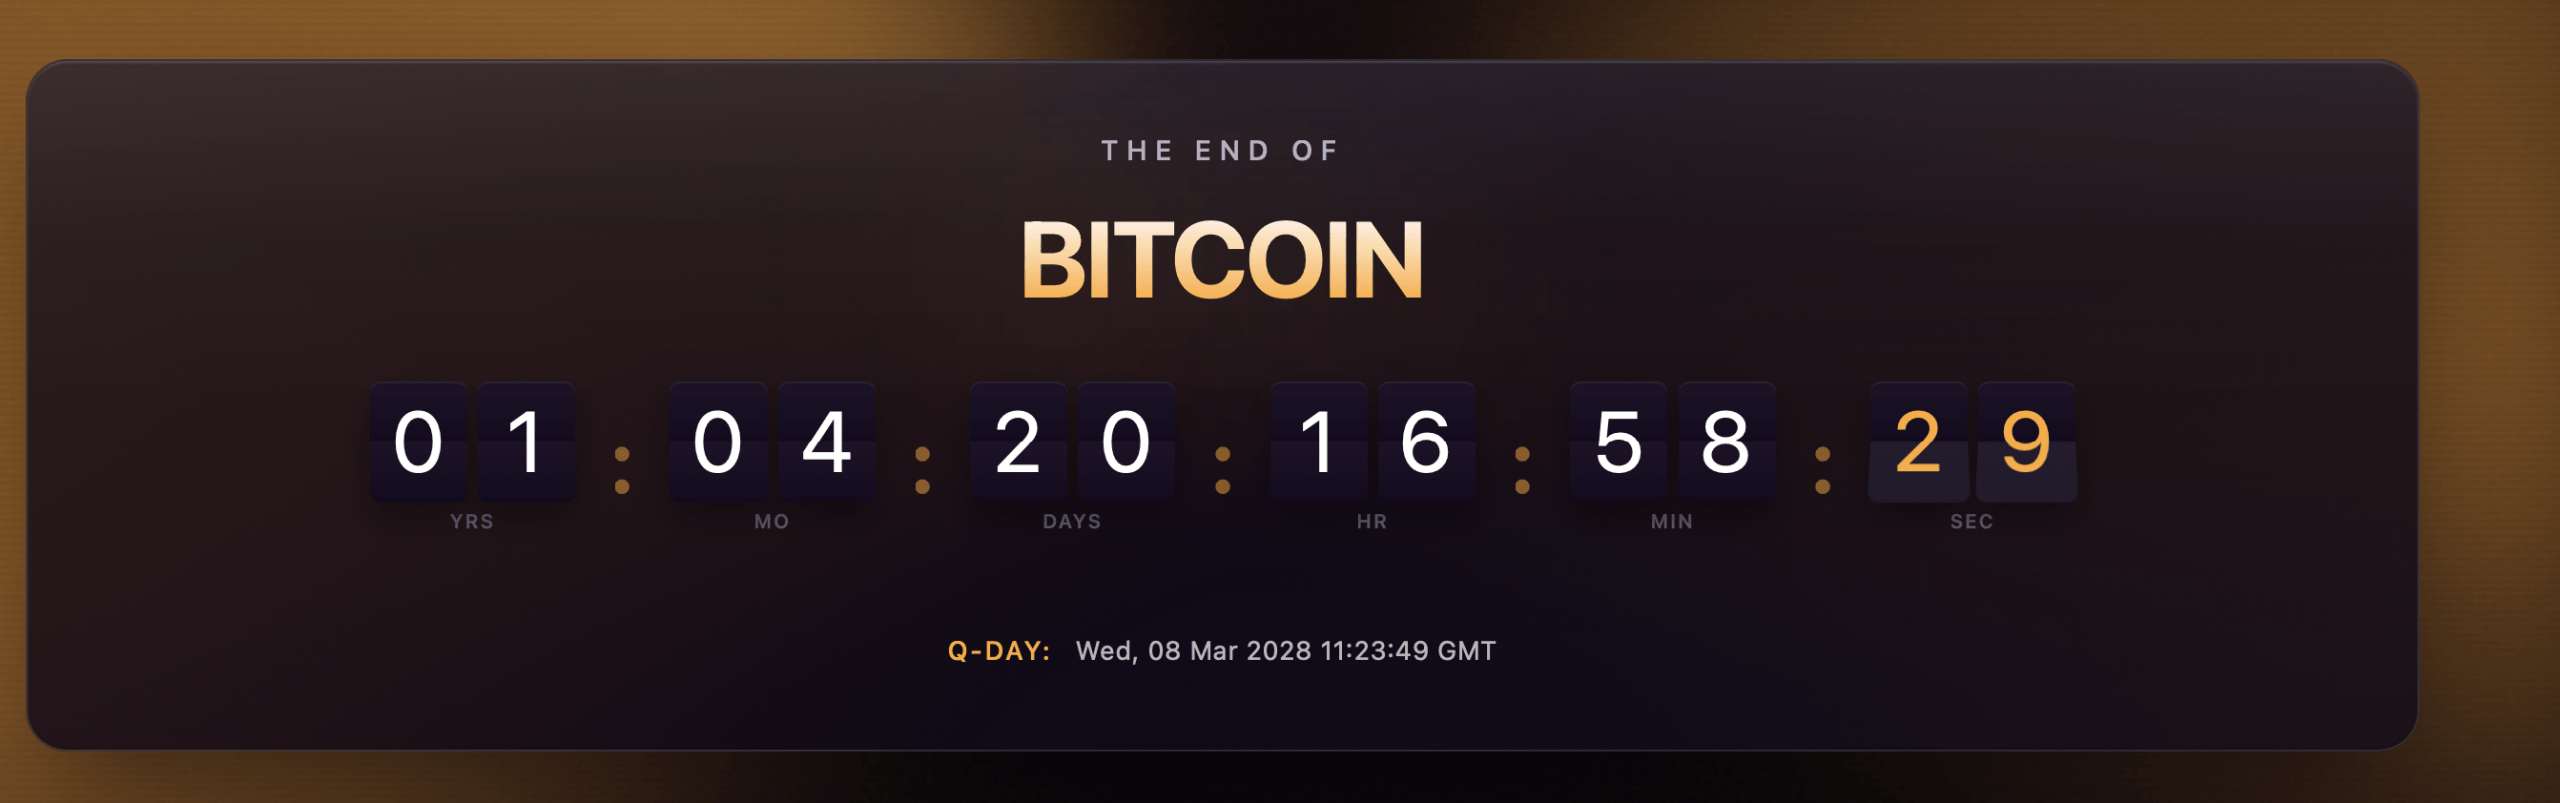
The Quantum Alliance’s contributors have also developed a Quantum Doom Clock pointing to March 2028 as an early possible window for a machine capable of breaking existing protections.
The clock tracks how quickly quantum computers are improving by measuring their qubits, the basic units of quantum computing power. Researchers study past growth, identify the most powerful machines, and use that information to estimate when computers might reach the roughly 856,000 physical qubits their model considers necessary to break today’s cryptocurrency security.
That date isn’t a prediction of an inevitable attack. Other researchers believe the danger is more likely to emerge during the 2030s. Still, preparing an entire cryptocurrency network for new security technology isn’t as simple as updating a password.
Nine Organizations Seek Common Security Standards
The Quantum Alliance includes contributors from Quantus, American Fortress, Intmax, Keystone, Midnight Foundation, Postquant Labs, Abelian, The Vault, and Hacken. Rather than create another blockchain, the group intends to establish publicly available standards for judging whether existing networks are prepared for quantum attacks. Its work covers four areas, including moving existing funds to safer cryptography, evaluating privacy technology, protecting wallets and ensuring security tools work across different blockchains.
Christopher Smith, founder and CEO of Quantus, explained the ambition. “In the future, ‘post-quantum cryptography’ will just be called ‘cryptography’ and everything else will be in a museum,” Smith remarked. The group is modeled on the Internet Engineering Task Force, where technical proposals are developed openly rather than dictated by a single company.
The Toughest Problem May Be Bitcoin Nobody Can Move
Even if Bitcoin adopts stronger cryptography, some coins could remain exposed. Funds held in forgotten wallets, lost accounts, or addresses whose owners never upgrade present a difficult question. Nobody can simply order every Bitcoin holder to move their money. And the problem extends beyond Bitcoin. Stablecoin systems, blockchain bridges, and other cryptocurrency infrastructure also rely on cryptographic protections that future quantum computers might defeat.
The Alliance aims to publish common tests and migration guidelines rather than dictate how individual networks should respond. For now, the industry’s quantum nightmare remains theoretical. The harder question is whether millions of bitcoin can be protected before that changes.