
After a 7-year corporate stint, Tanveer found his love for writing and tech too much to resist. An MBA in Marketing and the owner of a PC building business, he writes on PC hardware, technology, and Windows. When not scouring the web for ideas, he can be found building PCs, watching anime, or playing Smash Karts on his RTX 3080 (sigh).
Modern motherboards still ship with obscure headers that are almost useless for the average user. The reasons range from legacy compatibility and niche relevance to enterprise usage, but some headers can become a security risk under the wrong circumstances. If your PC is old enough, your motherboard may be using a discrete TPM (Trusted Platform Module), leaving the door open for a security exploit using your unpopulated debug header.
The modern TPM 2.0 standard doesn't need a discrete chip since it runs inside the CPU's firmware (fTPM). Intel's 8th Gen, AMD's Ryzen 2000 series, and newer CPUs enjoy broad support for TPM 2.0, but older systems are often dependent on dTPM. On such systems, an attacker with physical access to your machine can easily extract your decryption key with cheap hardware, unless you patch the vulnerability.
Older PCs with a discrete TPM are vulnerable
Firmware TPM is relatively more secure
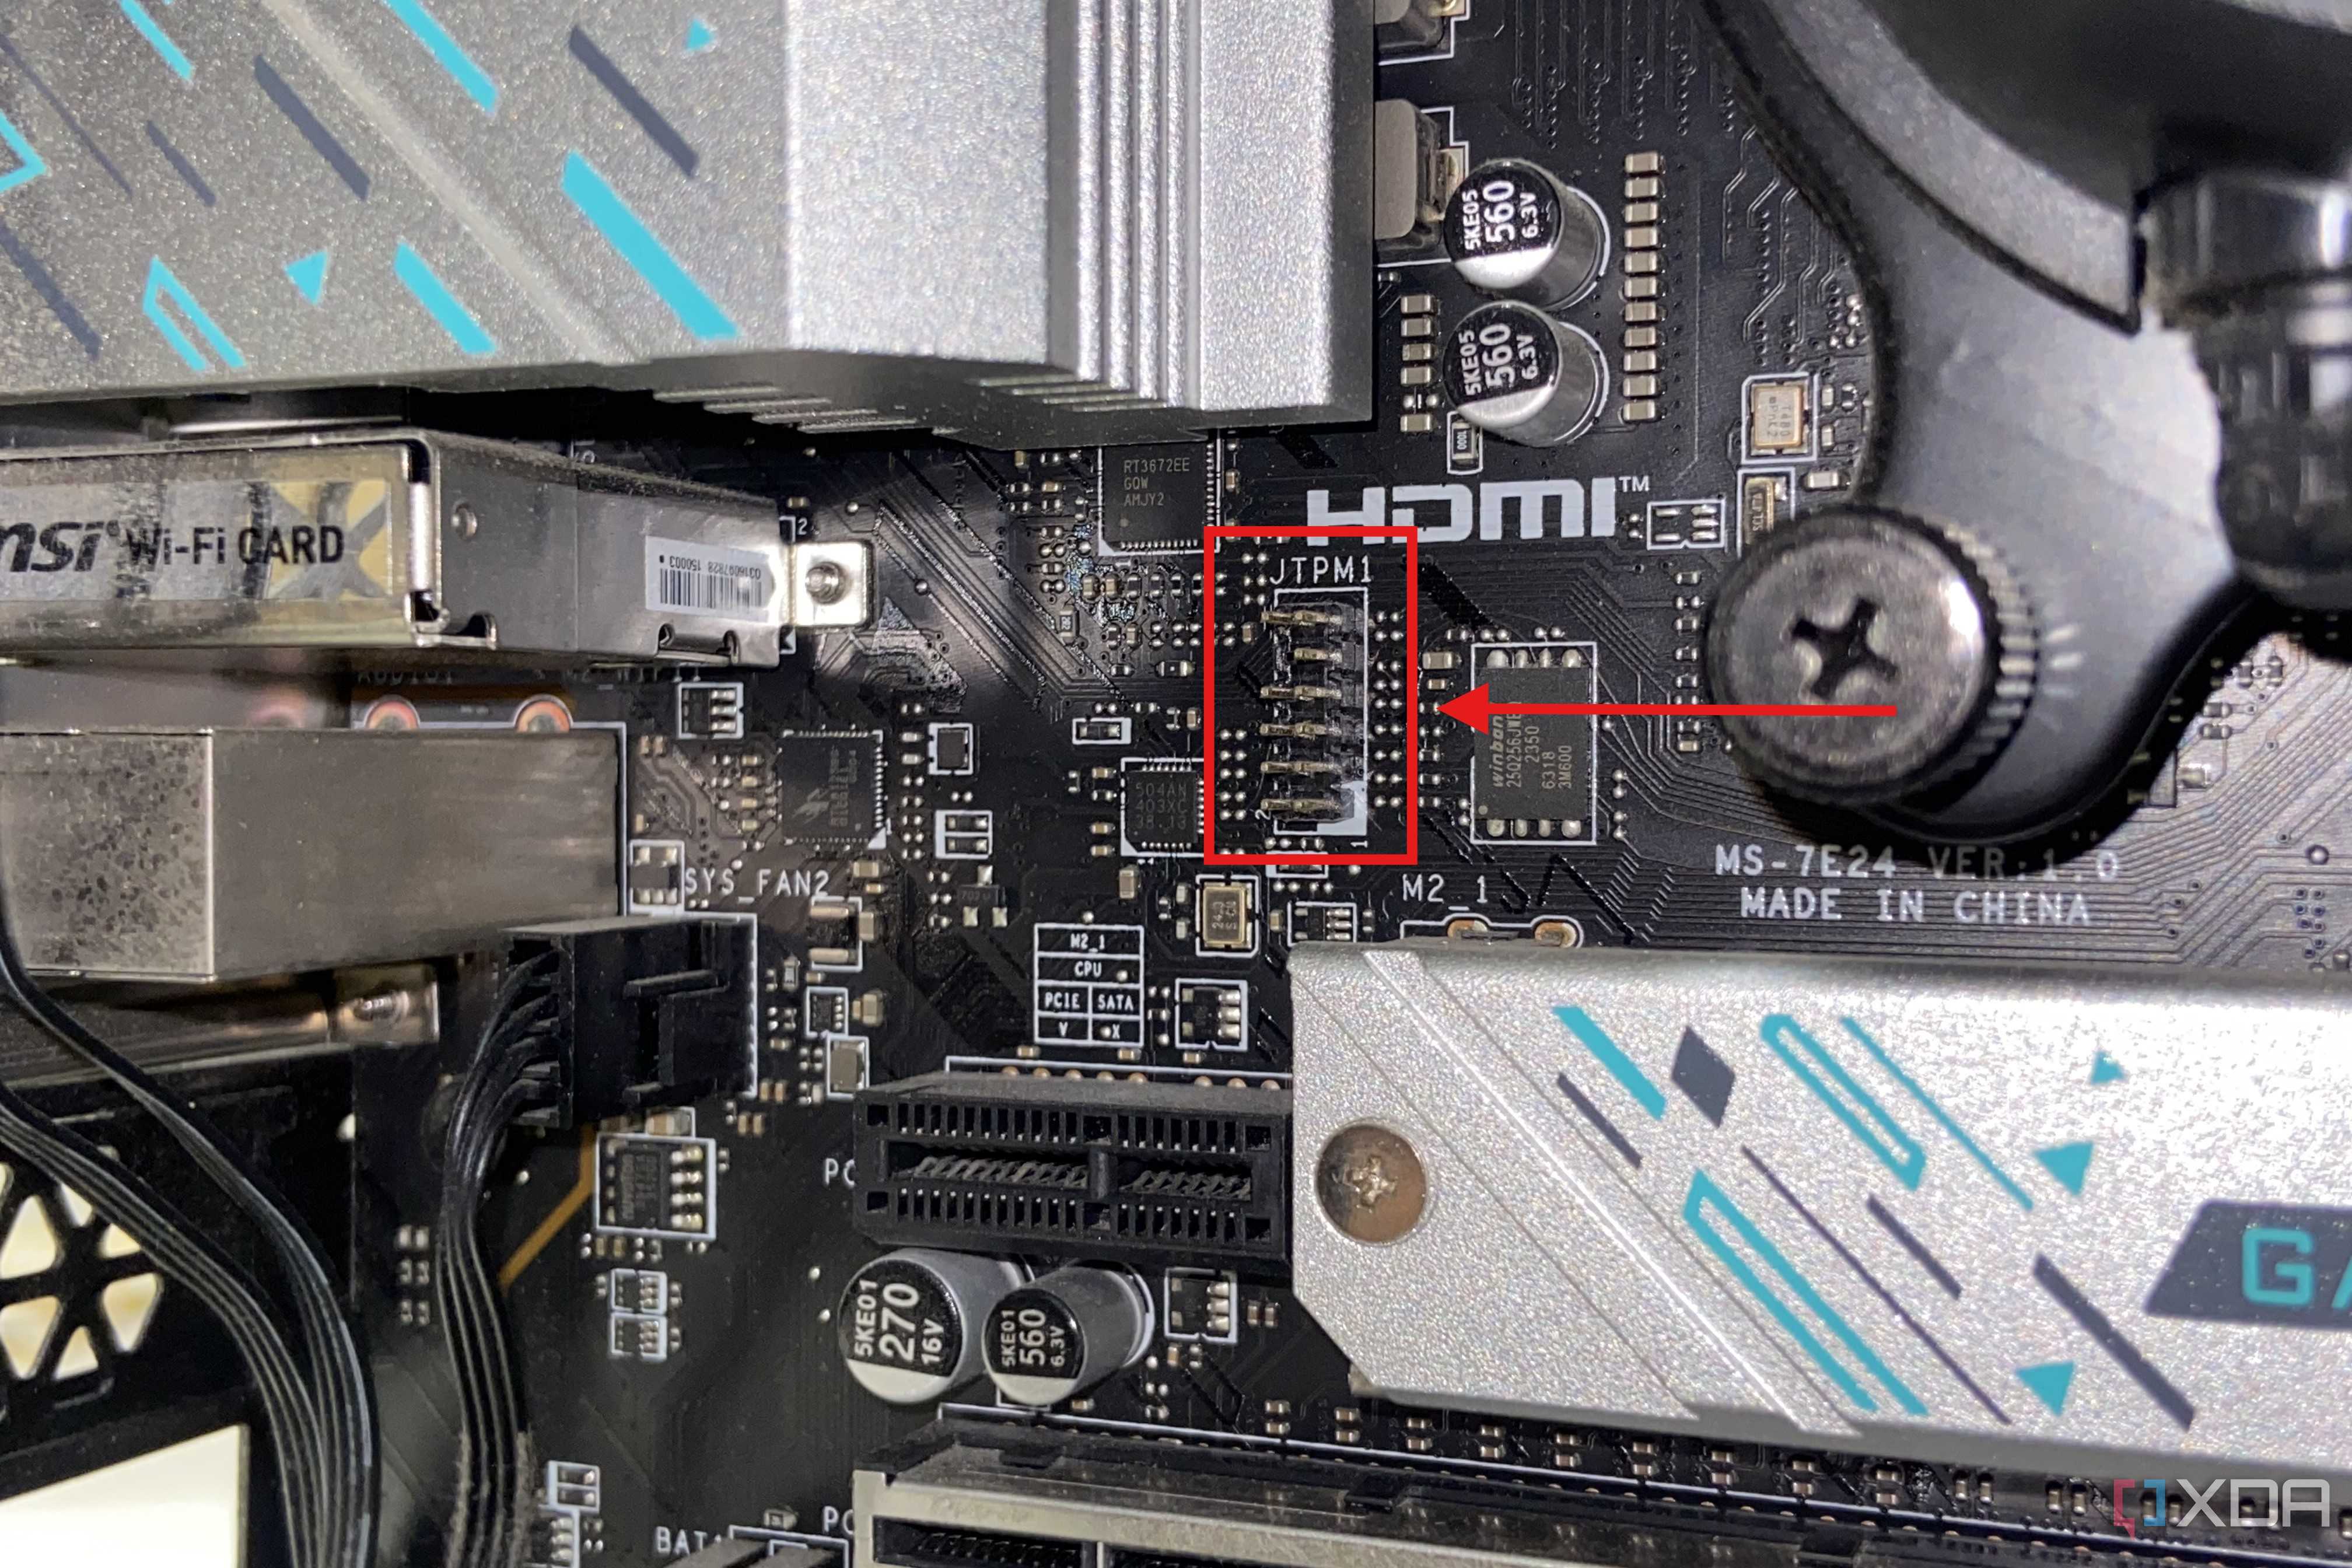

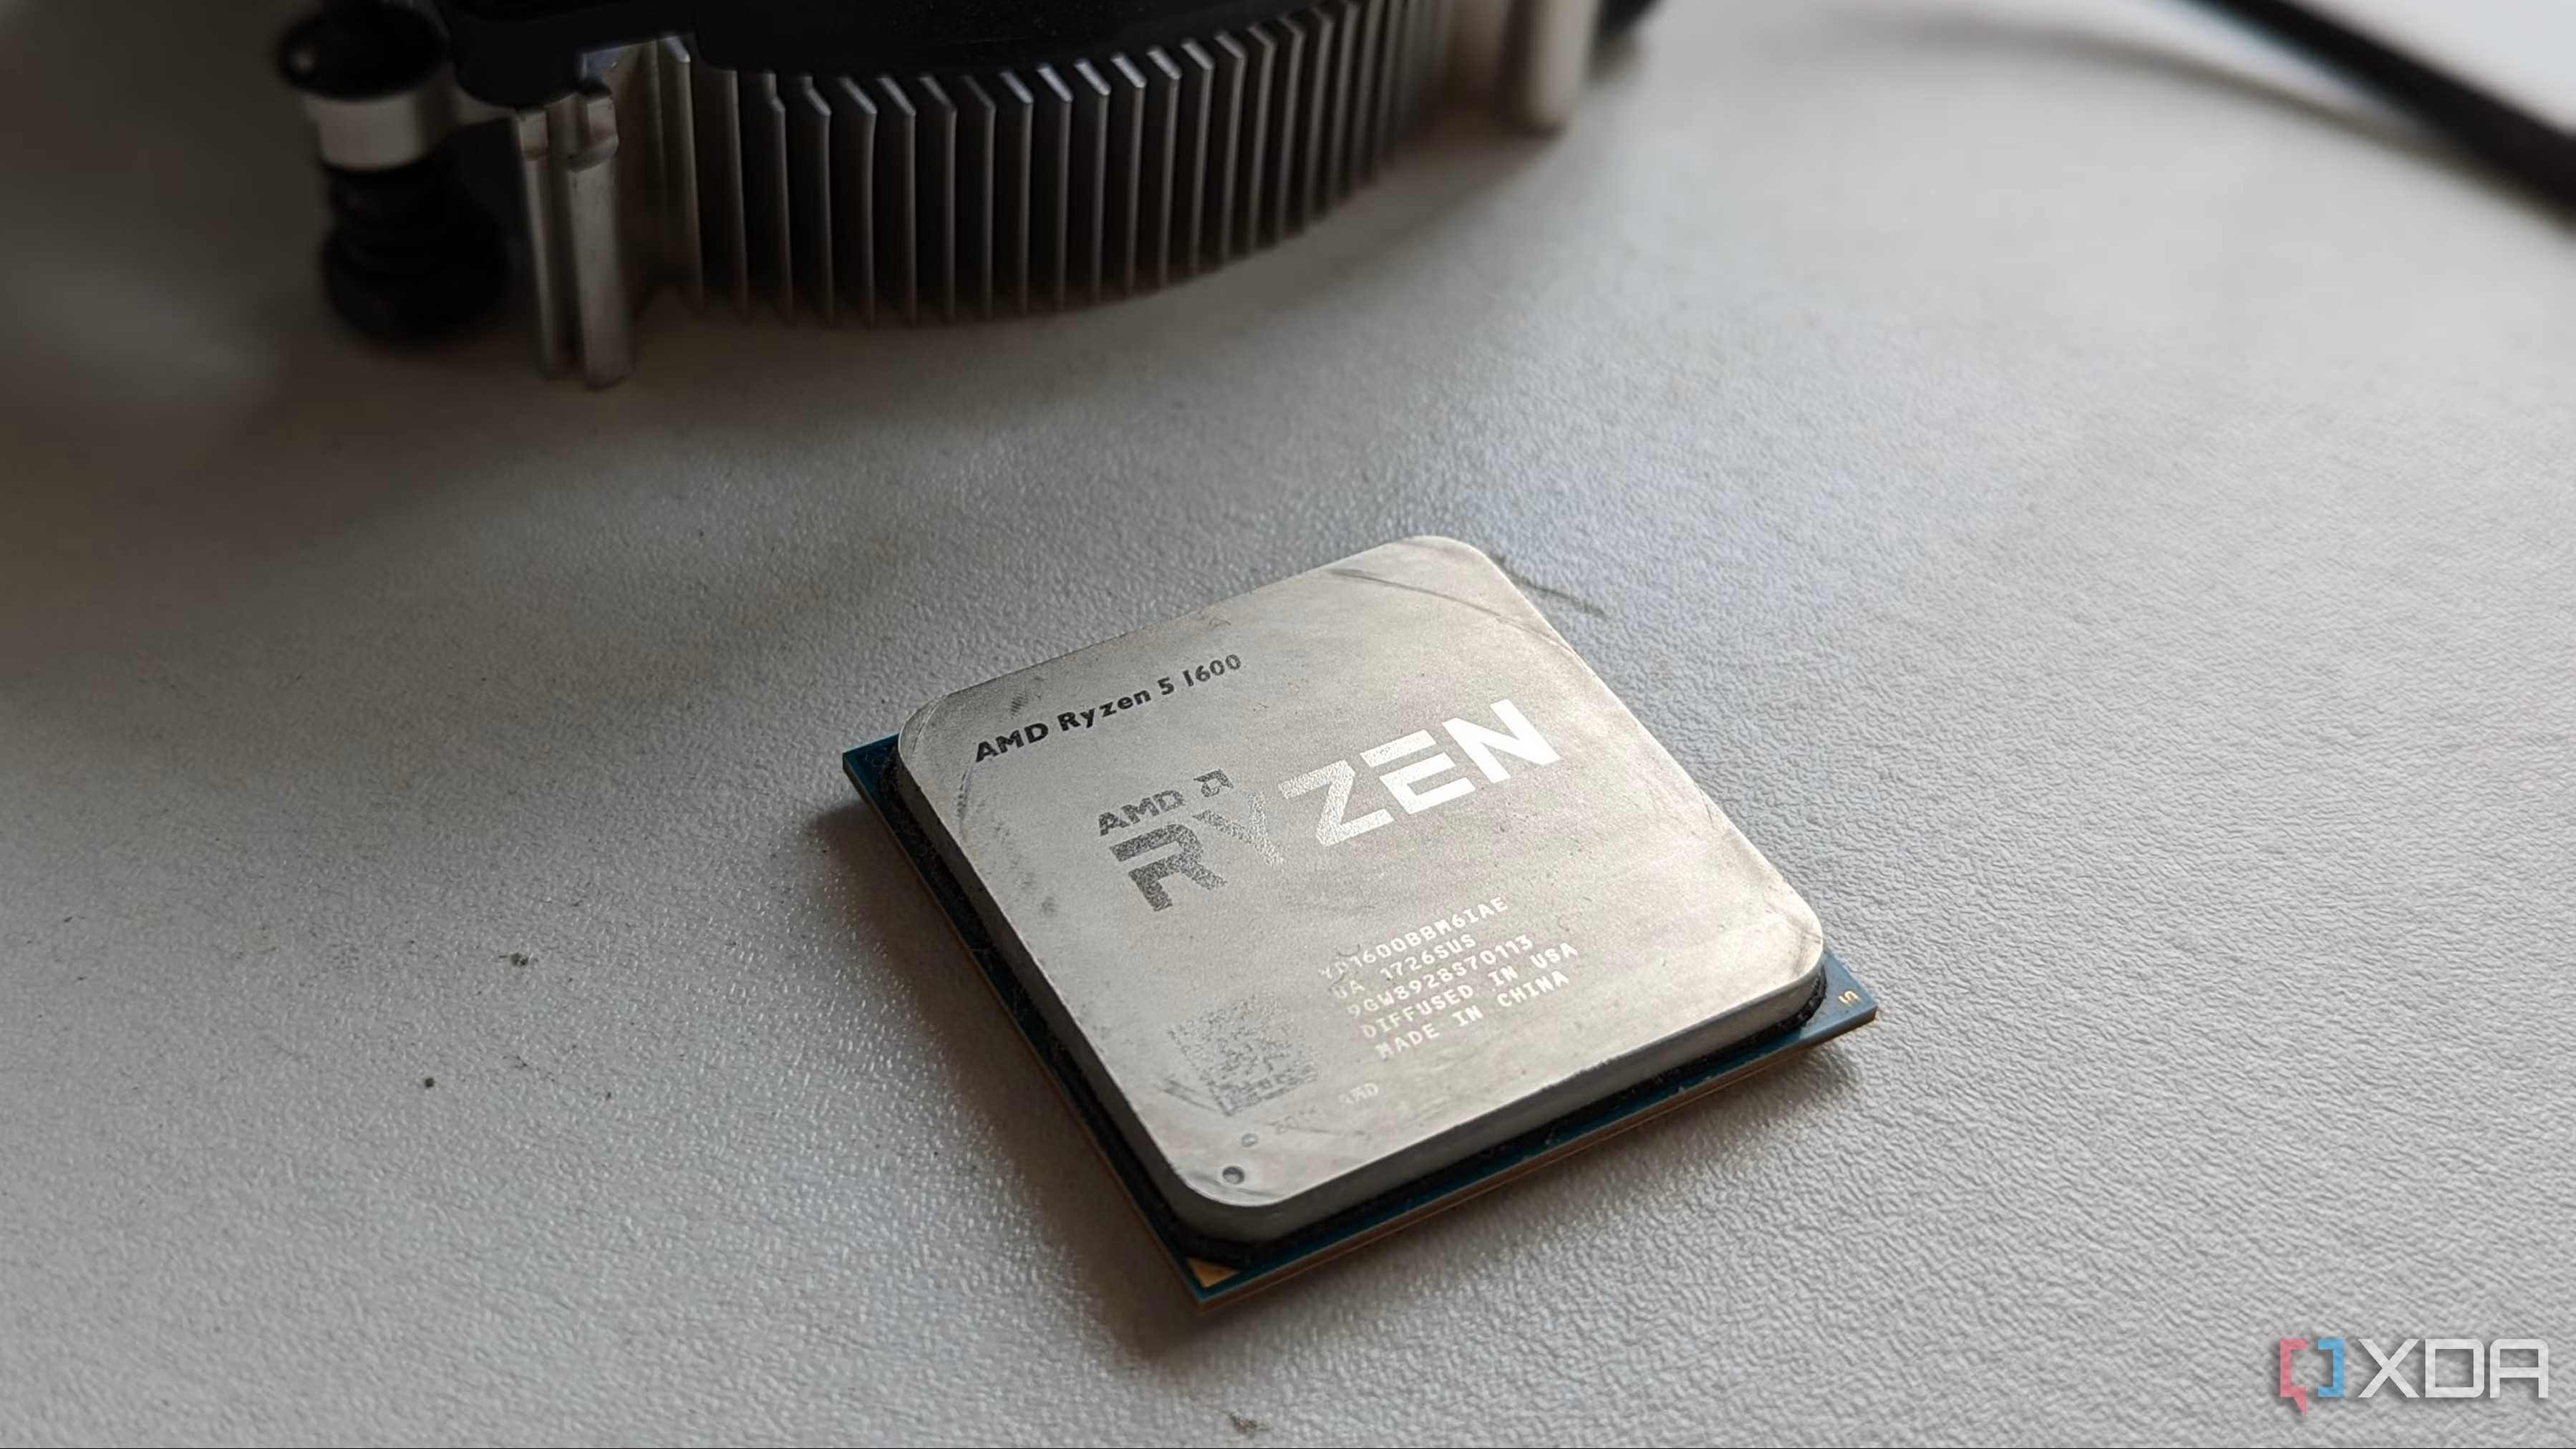
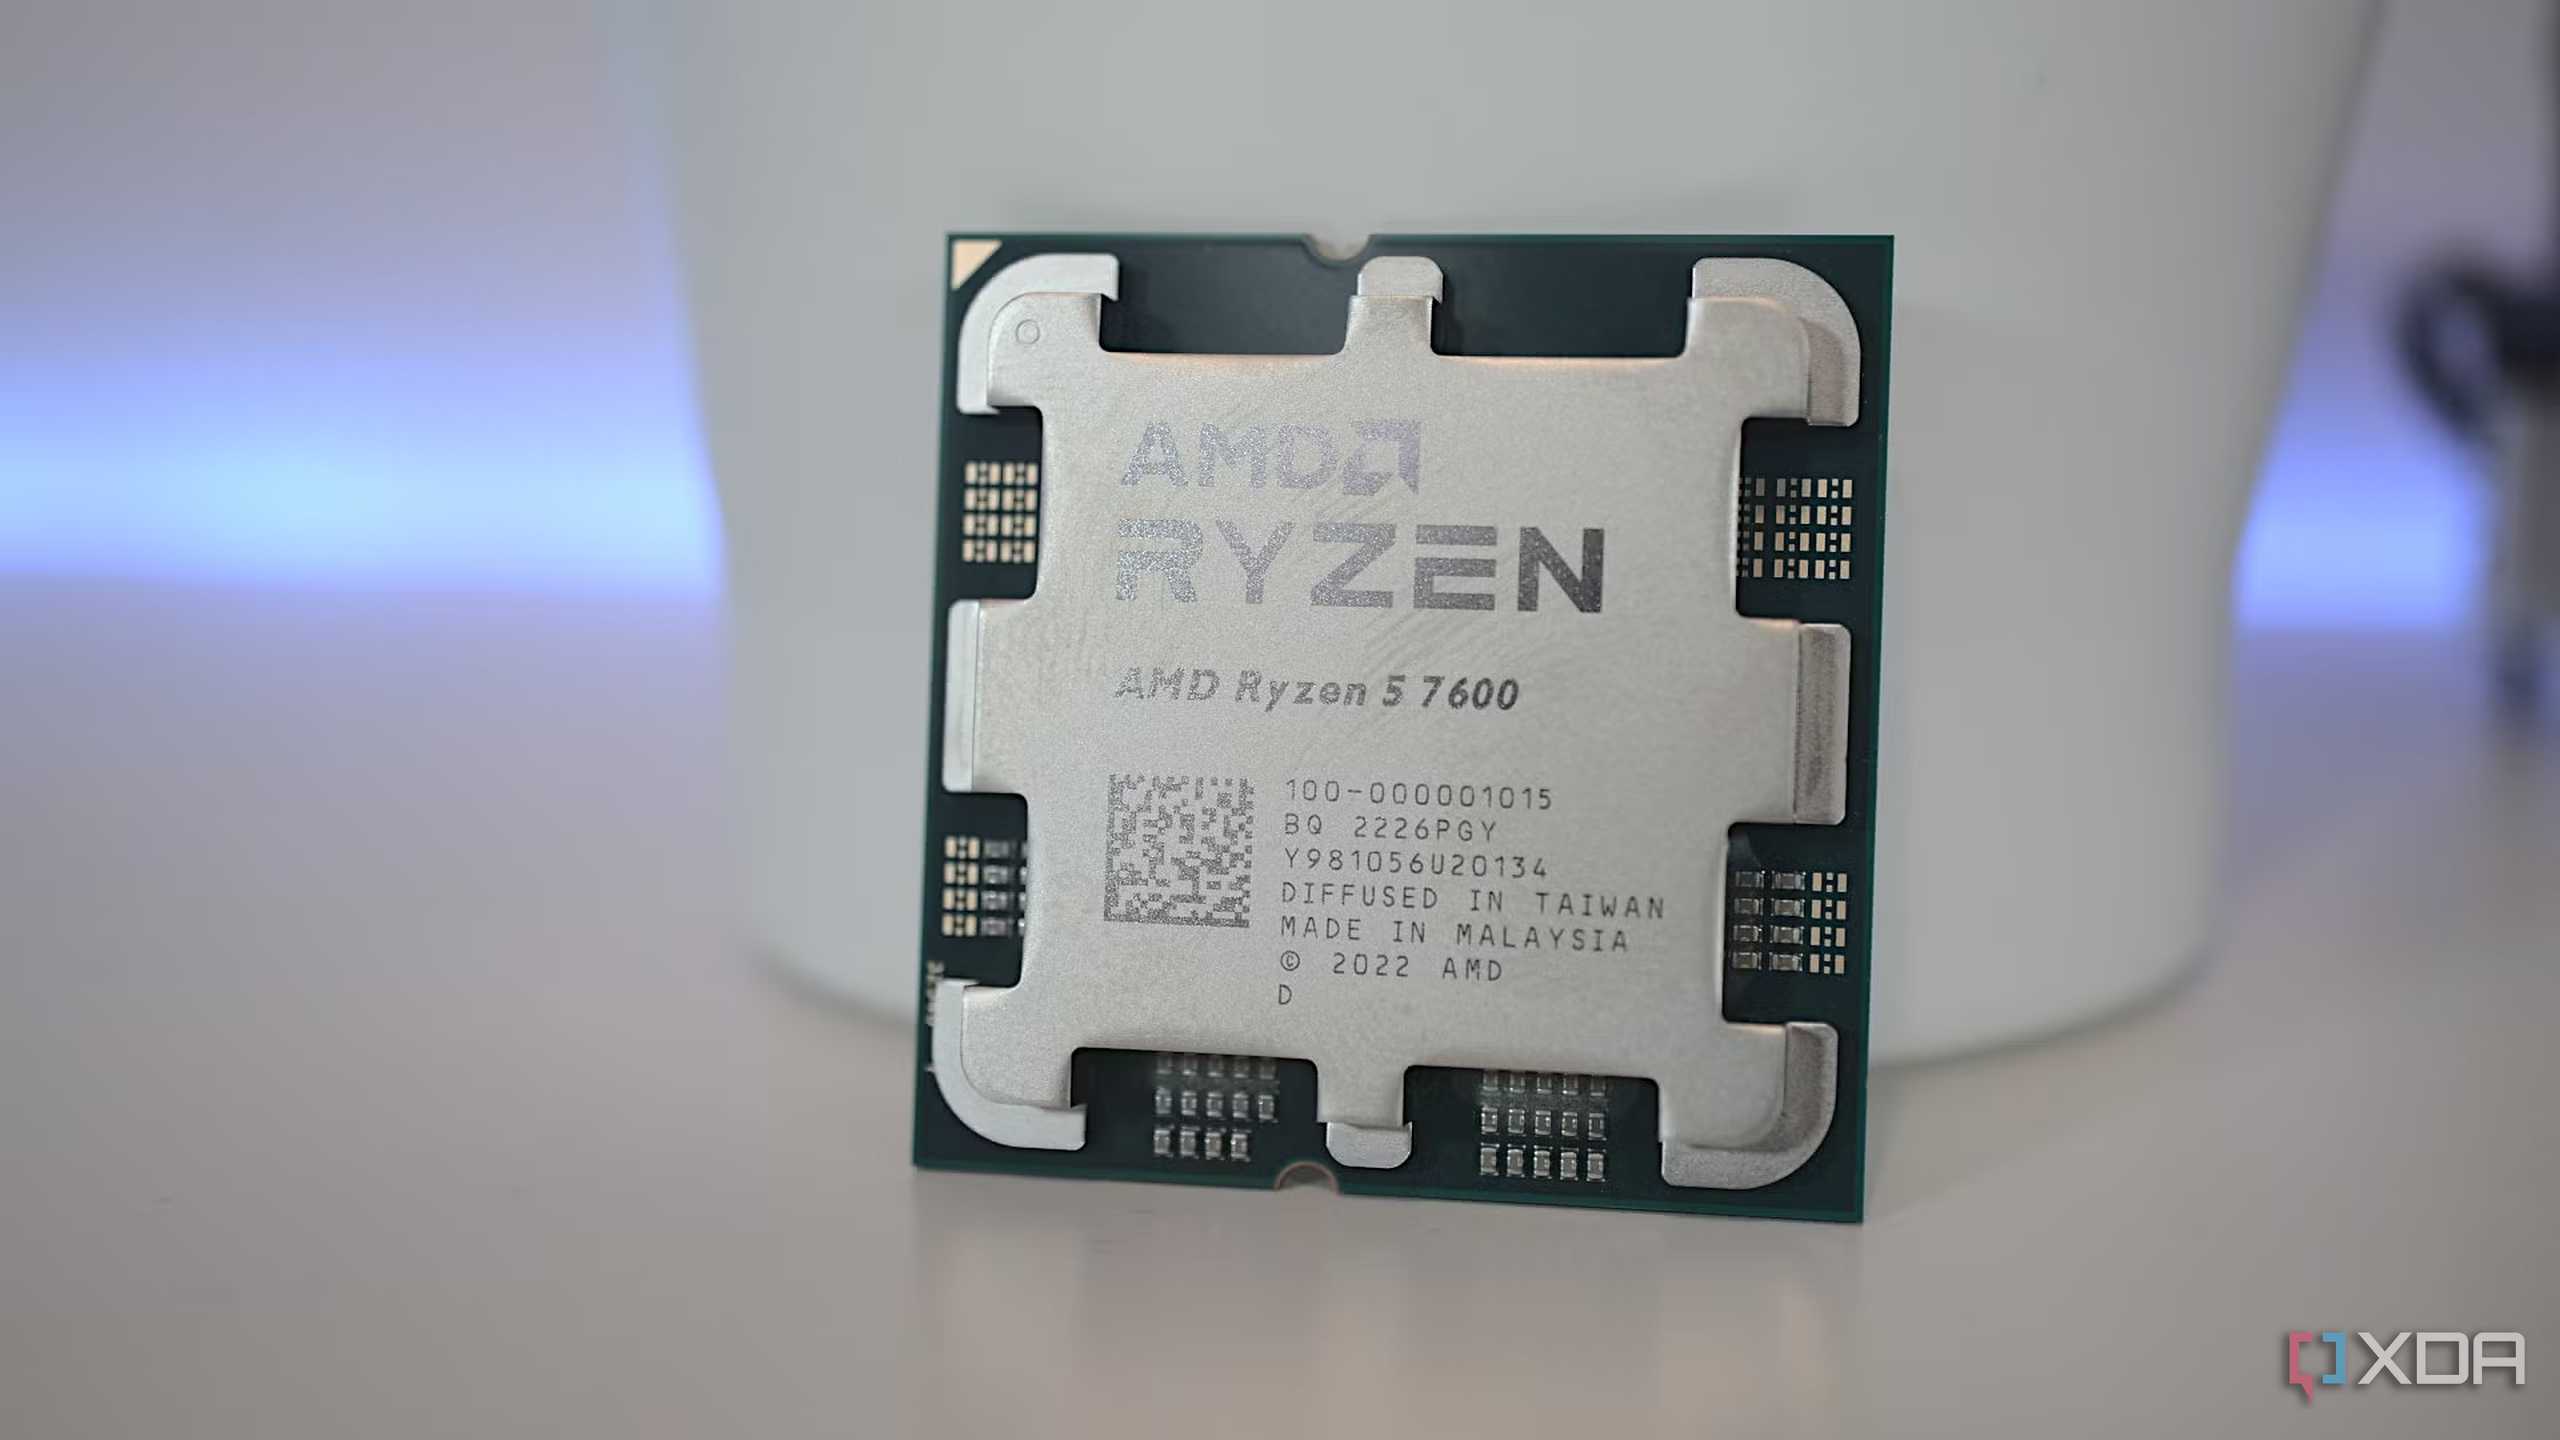
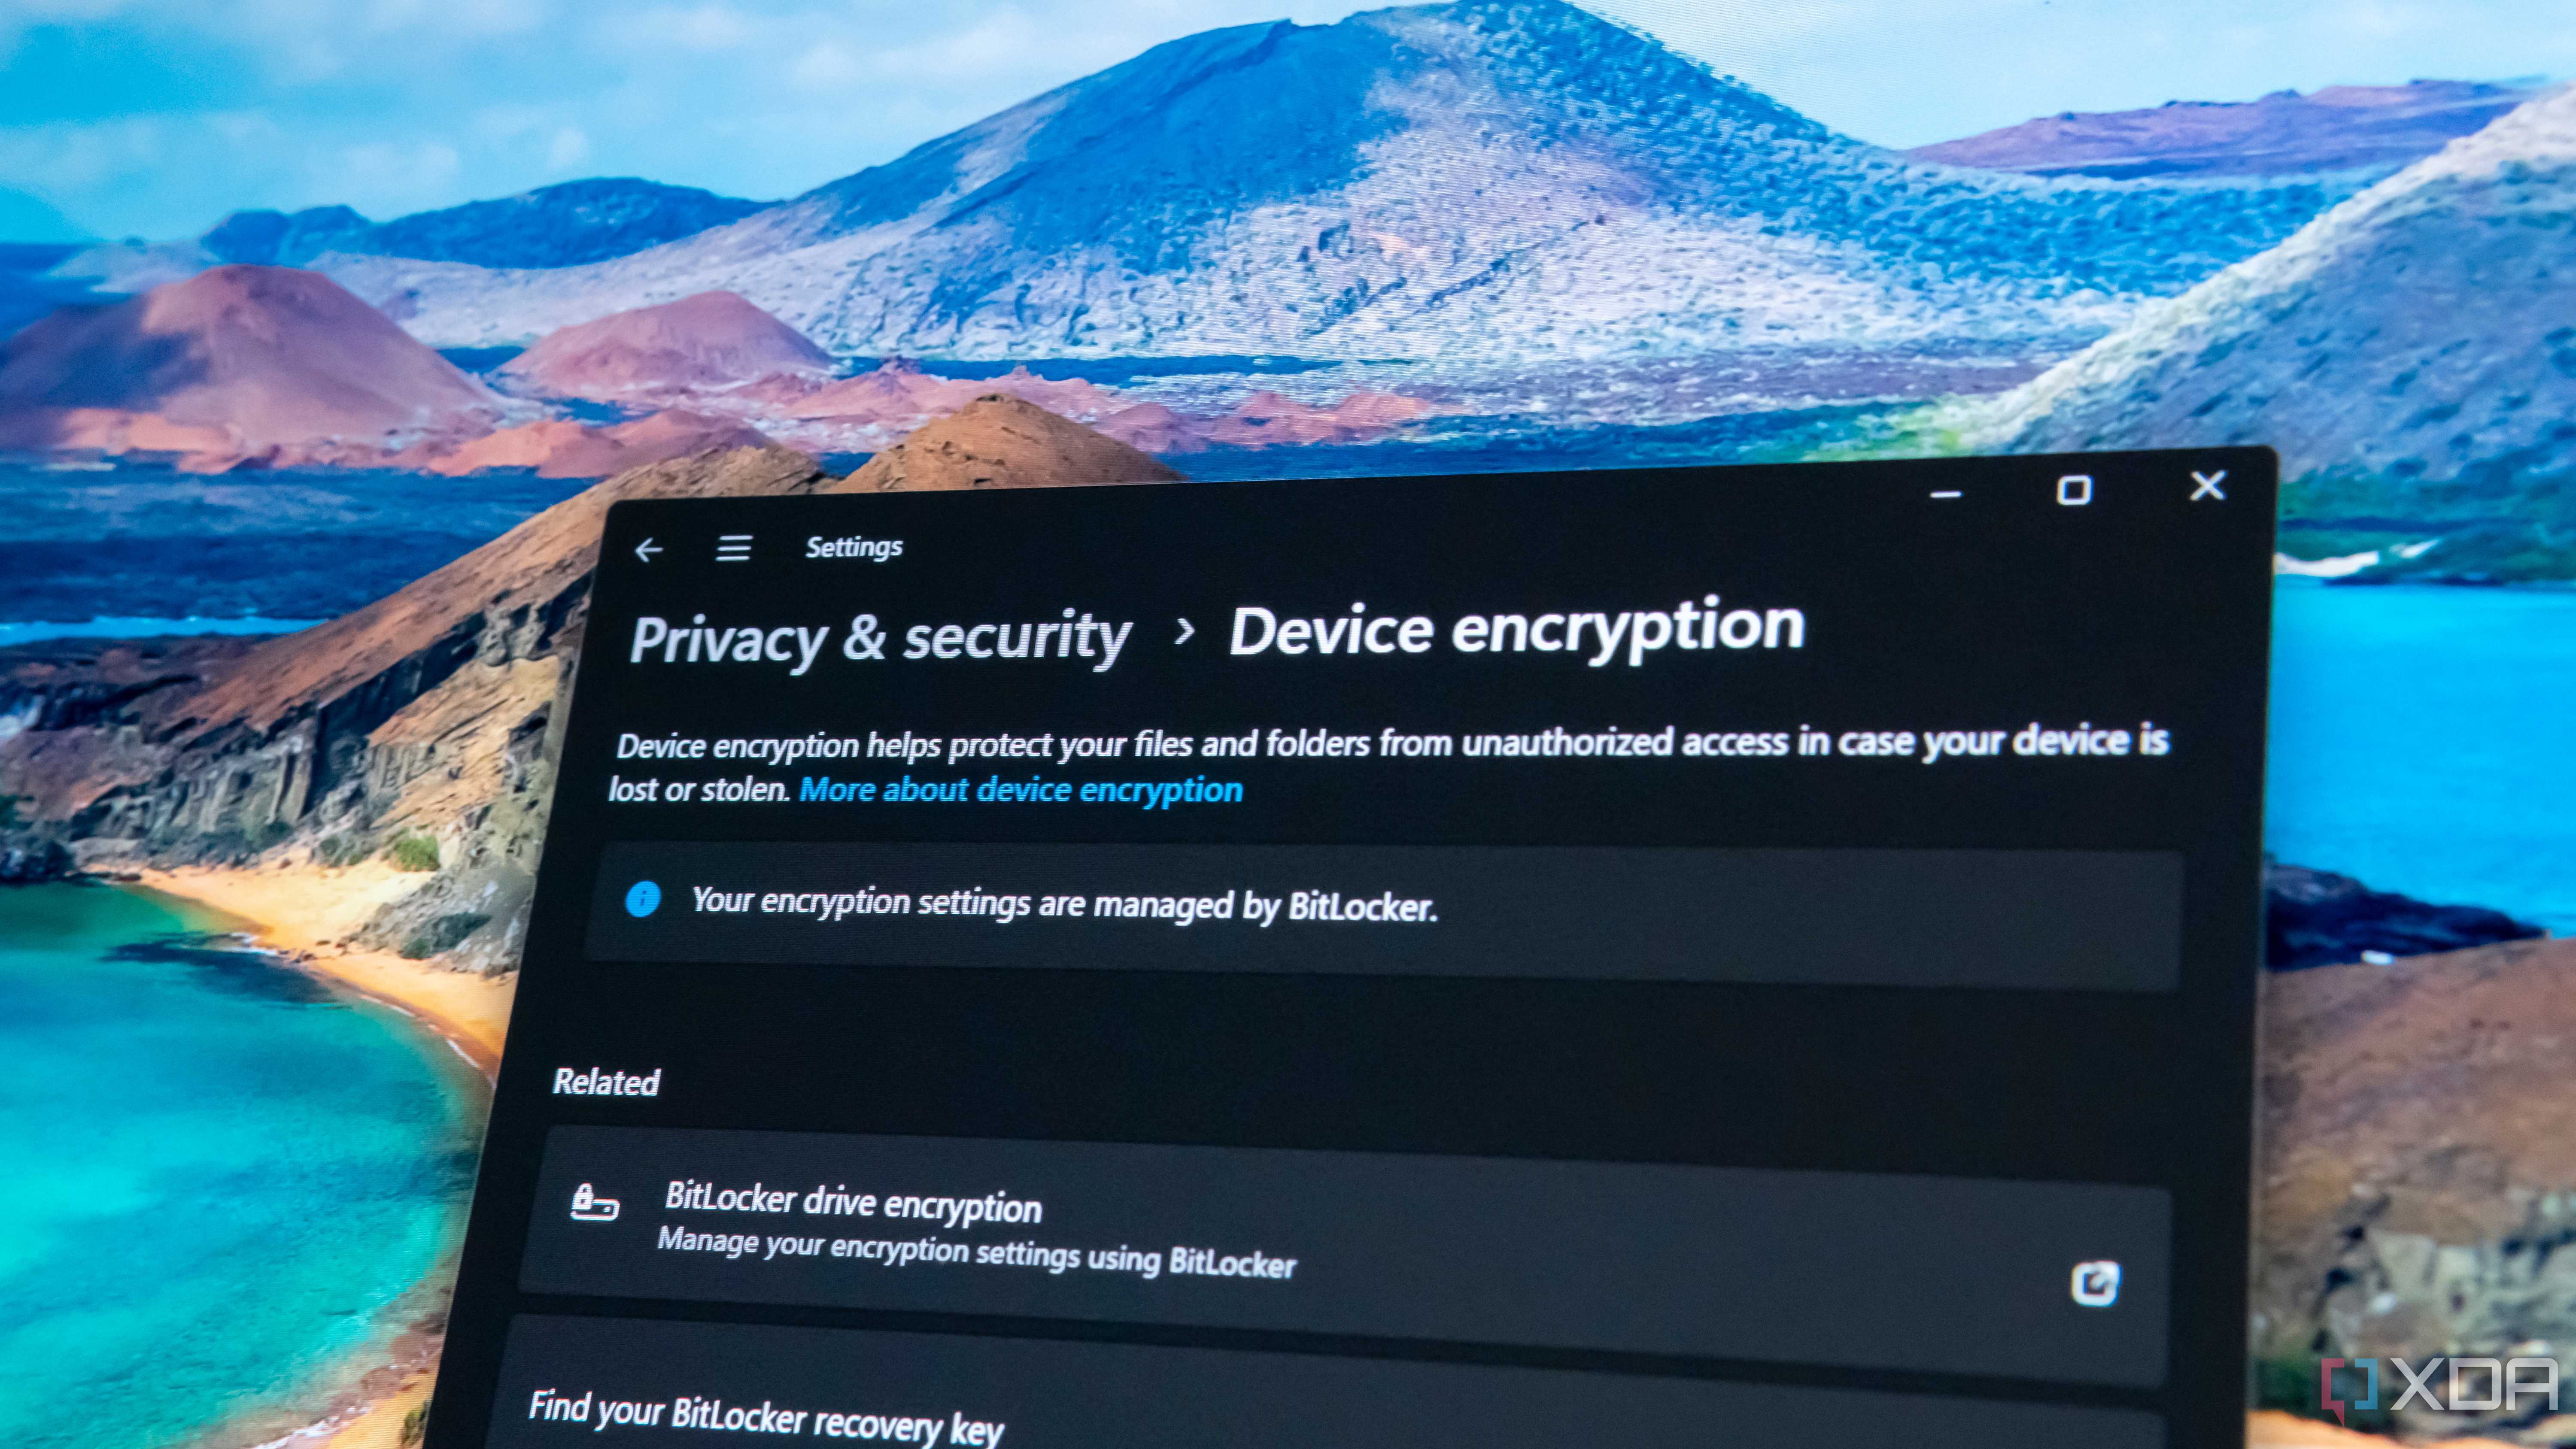
You probably have a relatively new CPU, manufactured in the last 10 years, but older CPUs don't feature universal firmware TPM (fTPM) support. They still use a discrete TPM chip that plugs into the TPM or JTPM1 header on the motherboard. The TPM's job is to verify the integrity of the system on every boot before releasing a cryptographic key to enable software like BitLocker to decrypt your drive. There are successive keys involved, but the primary point here is the pathway.
The TPM will not unseal the master key if it detects any change in the boot parameters, including the BIOS and bootloader code. This is to prevent an attacker who doesn't know the login password from simply booting into a Linux live image or removing the drive itself to access your data. However, an attacker doesn't need to do any of that. They can intercept the master key during the automated TPM-only mode that most machines are configured with.
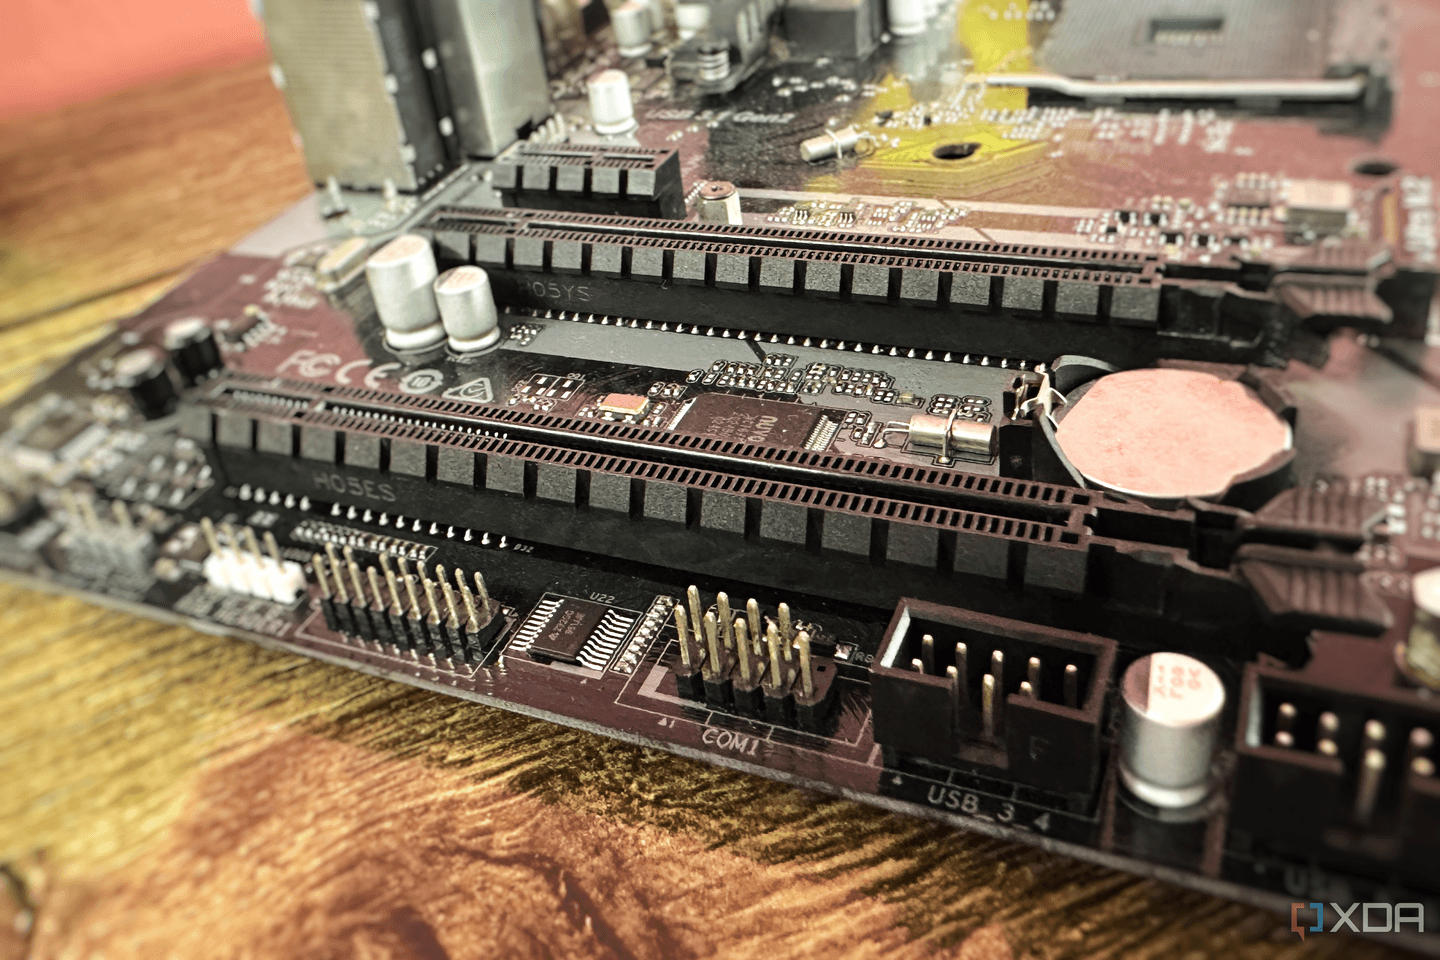
Once the TPM is satisfied with the state of the system, it sends the key to the CPU over a simple bus, usually LPC or SPI, but this traffic is unencrypted. This makes your master key vulnerable to bus sniffing if an attacker gains physical access to your machine. Since the LPC bus is shared with COM (serial header) and old debug headers that are usually unused and ignored, attackers can plug in an FPGA board or logic analyzer to read the unencrypted master key in under a minute.
An attacker doesn't even need to use your unpopulated debug header to do this. They can simply attach probes to the dTPM chip itself and achieve the same result. This key can then be used to decrypt your drive on any other system. Pulse Security, in 2019, demonstrated this exploit using a cheap $40 FPGA board.
You can check whether you have a firmware or discrete TPM by typing "tpm.msc" in a Run window and checking the manufacturer details. If it says Intel, AMD, or Microsoft, you have a firmware TPM. If it lists Infineon, Nuvoton, STMicroelectronics, or something else, your computer is using a discrete TPM.
Physical access makes the attack less likely, but lost laptops are still vulnerable
Your old machine can still be hacked

The elephant in the room is that this attack can't happen over the internet. An attacker needs physical access to your desktop or laptop to execute it. The possibility of it happening on a desktop might be slim, but a stolen or misplaced laptop is still exposed. Researchers have shown that it's possible on Dell, Lenovo, and Microsoft laptops, among others.
Most people use BitLocker in the default TPM-only mode, so the boot process doesn't ask the user for any additional authentication before releasing the master key, provided the boot parameters haven't been tampered with. If a determined attacker steals your laptop or finds it unattended, they need only a few minutes to access the motherboard and execute the exploit with a pre-configured logic analyzer.
BitLocker encryption is something most people don't think about after setting it up on a new PC. It stays in the background and rarely passes your mind. However, older systems with discrete TPM chips remain vulnerable to cheap and simple exploits. Even firmware TPM isn't bulletproof, since voltage injection and software-based attacks remain a concern, but it's still more secure than a discrete, unencrypted TPM authentication process.
You can protect your system with a pre-boot PIN
Stop bus sniffing in its tracks
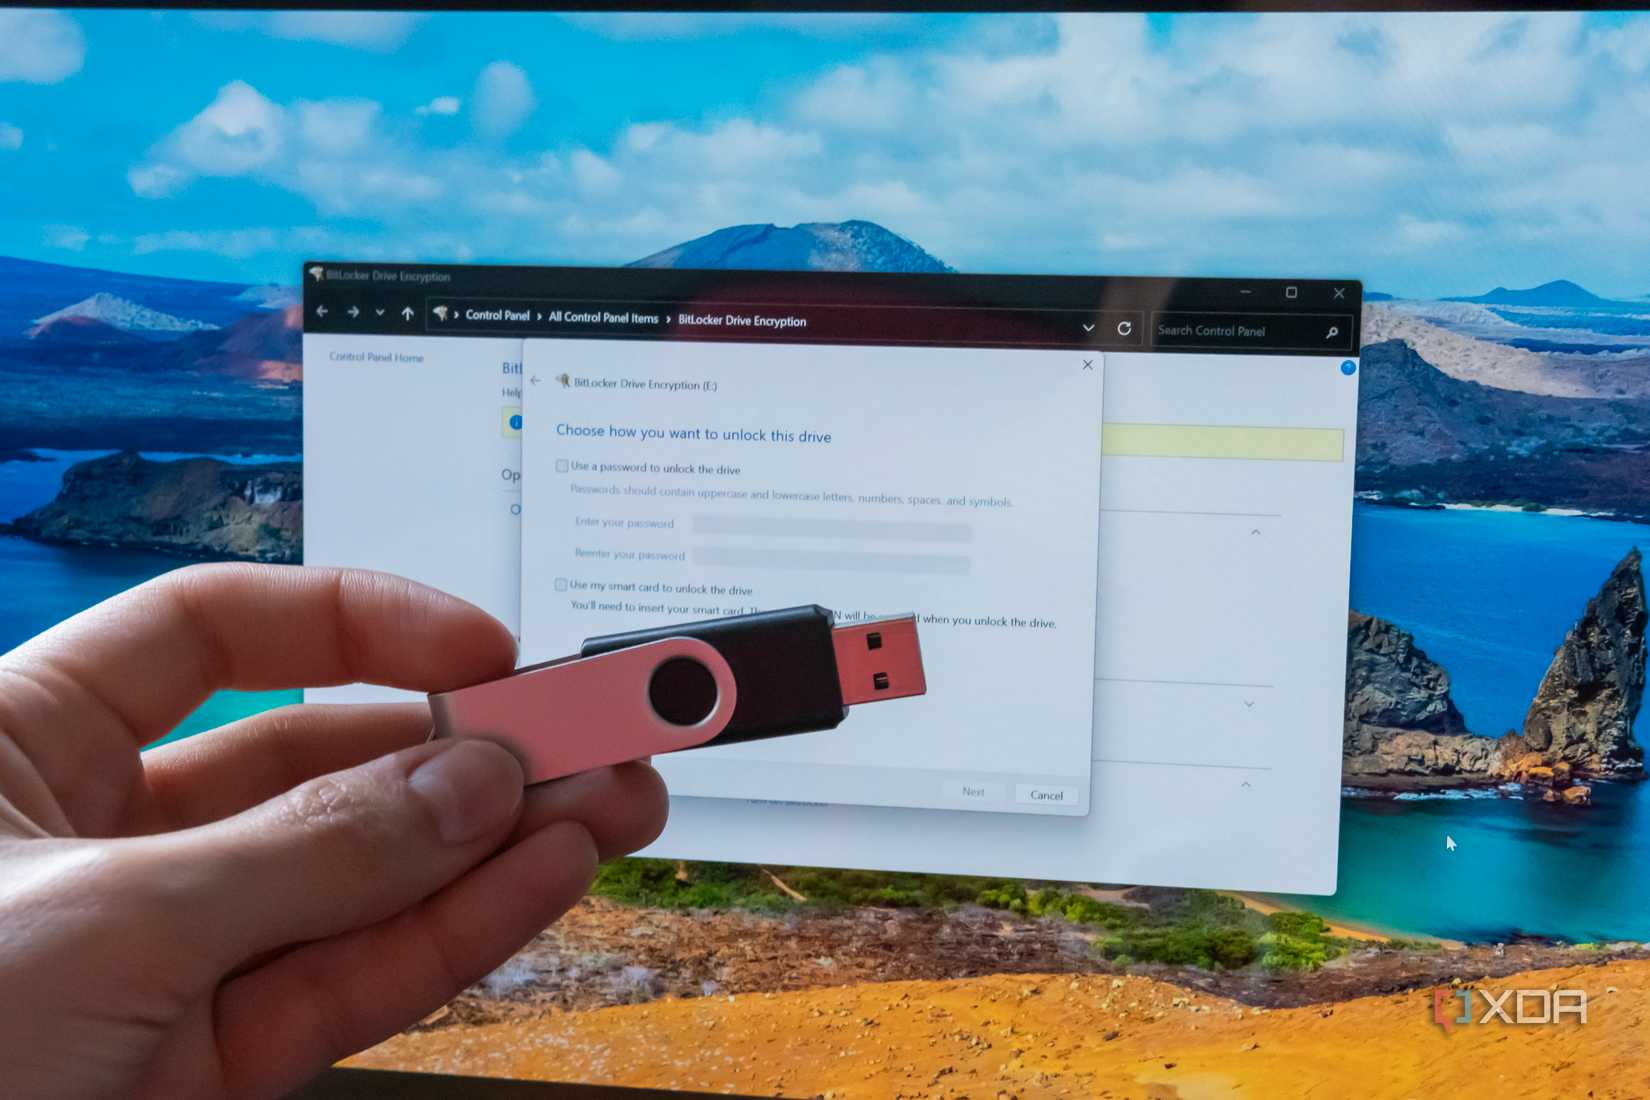
Thankfully, there are ways to patch this vulnerability on your dated system. If fTPM isn't supported by your processor, you can enable a pre-boot PIN or password in your BitLocker settings. This extra layer of authentication breaks the default automated mode, so the TPM doesn't release your master key without the PIN. Even if an attacker uses bus sniffing, they won't gain access to anything since they don't know your PIN or password.
Alternatively, you can configure BitLocker to require a startup key alongside a PIN, and bind this startup key to a USB drive. This adds another layer of security to your system. You will have to enter the PIN as well as plug in your USB drive on every boot, but you'll ensure you've done your best to protect your system.
This "TPM + PIN + startup key" offers triple-factor authentication that secures even modern fTPM-based systems, since voltage glitching and software-based attacks can't access a PIN which isn't stored anywhere (it's in your brain or a secure physical or digital file).
Stealing your BitLocker master key is easier than you think
Most people are probably using a firmware TPM embedded inside the CPU silicon, so bus sniffing isn't possible on such systems. Although these machines are vulnerable to other exploits, they can still be secured via multiple layers of authentication. Older PCs with a discrete TPM chip need urgent attention if one wants to secure against cheap and quick bus sniffing attacks.