About 100,000 pieces of personal information were leaked from 16 financial firms in a string of AI-driven hacking attacks, including a breach at Gopax, a won-based cryptocurrency exchange, South Korea's financial regulators said. To prevent further damage, authorities will review security systems across the entire financial sector and require large financial companies to check for security vulnerabilities at least twice a year.
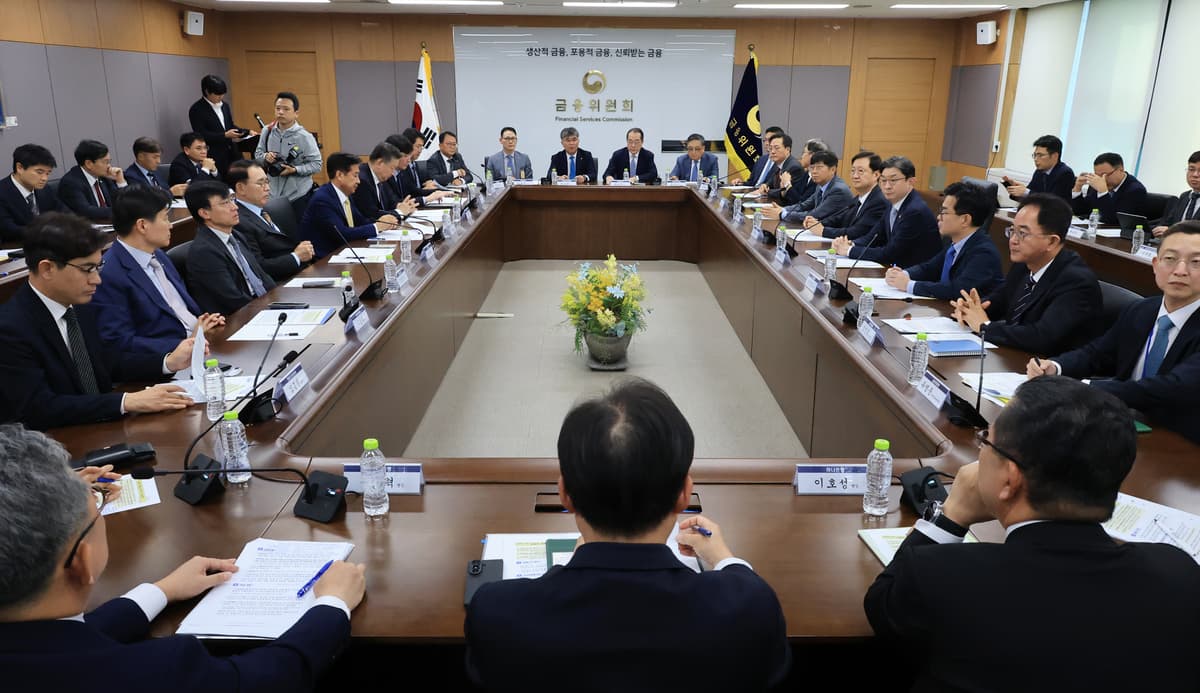
The Financial Services Commission, the Financial Supervisory Service and the Financial Security Institute announced the findings of their investigation into the breaches and a plan to tighten security management on the 14th, following a second emergency response meeting at the Government Complex Seoul chaired by Shin Jin-chang, secretary general of the FSC.
Sixteen financial firms have been confirmed as hacking victims before and after the breach at Shinhan Bank, according to the regulators. Five of them were newly identified on the 14th. DB Savings Bank, KDB Capital and electronic payment firm Brightfix reported breaches, while in the cryptocurrency sector, incidents occurred at Streami, the operator of Gopax, and at coin-market exchange Prabang.
KDB Capital said in a notice on its website on the 14th that it detected abnormal external access on the 12th and that three categories of data — the names, resident registration numbers and dates of birth of 848 customers — were leaked. DB Savings Bank said there had been a hacking attempt but that it was blocked by its security system and no customer information was leaked.
The data leaked from the financial sector so far includes names, contact numbers, resident registration numbers and email addresses. No leaks have been confirmed of information that could be directly exploited for fraudulent payments, such as account numbers or card numbers. The regulators said the number of affected companies could rise further, as they are investigating additional possible breaches based on attacker IP addresses shared by the financial firms.
The investigation also exposed weaknesses in security management across the financial industry. Of 555 financial firms that completed a security checklist through the 8th, 130, or 23.4%, reported some shortcomings, while 425, or 76.6%, reported none. Shortcomings were relatively more common among electronic payment firms and online investment-linked finance providers, which have comparatively weak security capabilities.
The problems found were mainly a failure to apply the latest security patches and poor management of aging computer systems no longer supported by their manufacturers. Some financial firms did not operate round-the-clock security monitoring, and in some cases authentication procedures were missing from systems accessible from outside. The regulators ordered those firms to take immediate steps, including replacing outdated equipment and adding security monitoring staff and facilities.
The authorities said they would overhaul the financial sector's security management framework in response to the incidents. They will first identify every point at which financial firms' computer systems connect to the outside and conduct a full review of authentication, access rights management and internal controls. They also plan to clarify the reporting lines and scope of responsibility of chief executive officers, chief information security officers and chief information officers.
Requirements for large financial firms to check for security vulnerabilities will also be tightened. Financial companies and electronic payment firms are currently required to carry out vulnerability checks and assessments once a year. The regulators will raise that to at least twice a year, starting with large financial firms that have large customer bases. Key external connection points will be added to the list of mandatory checks, and the authorities plan to establish grounds for ad hoc inspections when urgent threats emerge.
For small and midsize financial firms with relatively limited capacity to invest in security, the authorities will push for a joint response system. The Financial Security Institute plans to consider building an artificial intelligence-based joint security monitoring system together with industry associations and federations. The regulators will also review ways to tighten oversight of moneylenders and corporate insurance agencies, which are excluded from security management requirements under the Electronic Financial Transactions Act.
"We will also move quickly on regulatory improvements, such as easing network separation rules, to establish a security system that defends against AI attacks with AI," Shin said.