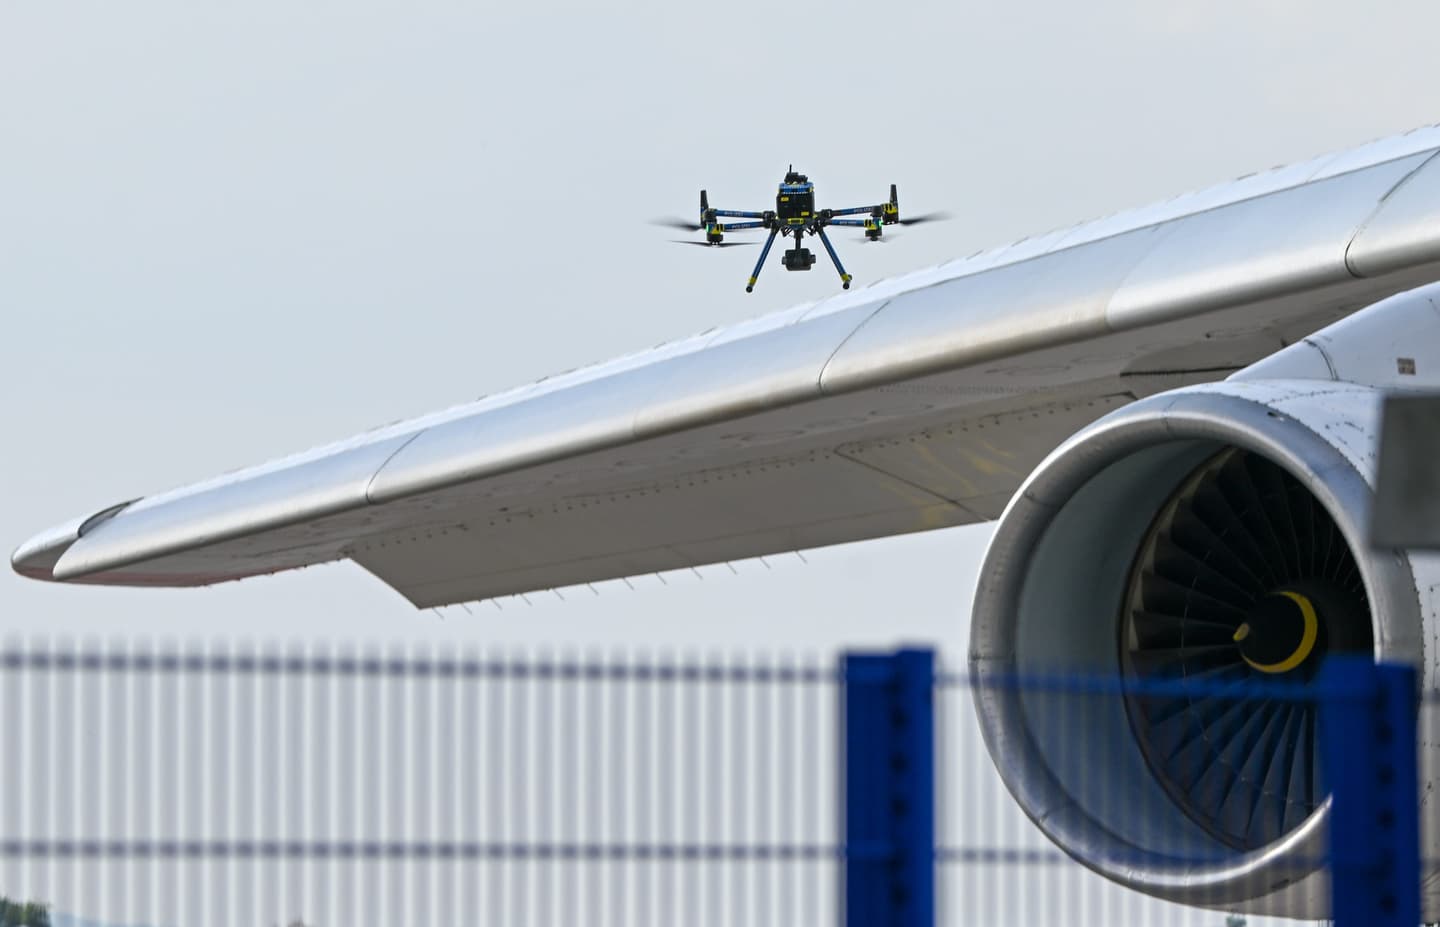
- A failed drone attack on a Ukrainian transport plane in Germany revealed a sophisticated Russian sabotage network, tracing back through motorcycle-riding intermediaries to Moscow’s GRU intelligence agency and exposing a coordinated European bombing campaign.
- Russia has created an “espionage gig economy” using Telegram and cryptocurrency to recruit desperate workers as “disposable agents” for small-scale attacks, making it impossible to distinguish foreign sabotage from random crime or lone-wolf violence.
- By deploying numerous low-skilled agents against minor infrastructure targets, Russia stretches enemy defenses thin using a Soviet-era strategy, though some recruited workers' laziness and corner-cutting may inadvertently undermine the effectiveness of these operations.
It began with a drone on a tarmac in Germany.
The drone’s mission was to destroy a Ukrainian Antonov An-124 cargo plane at Leipzig/Halle Airport. Had it succeeded, the “severe structural damage” it was intended to cause might have been attributed to a lone wolf—either as an act of domestic terrorism or just a random act of unhinged violence.
But, as a joint investigation by The Telegraph and the Welt am Sonntag points out, because the plot failed, authorities in Germany were able to recover the drone completely intact, along with the tin full of explosives that it was carrying. Investigators discovered that the explosive device wasn’t some amateurish improvised bomb made by a madman. Instead, it “closely resembled bombs in Russian plots elsewhere across Europe.” That resemblance allowed them to trace the plot not just to the “disposable agent” recruited to carry it out, but to the motorcycle-riding Russian intermediary German intelligence believes managed him, and to the man in Moscow suspected of giving that biker his marching orders on behalf of Russia’s military intelligence—the GRU.
At the center of this operation, the reporting suggests, is Oleg Levushkin, a motorcycle enthusiast who ran an import business in tea, coffee and spices. German intelligence says his job was “preparing the means of committing the crime before its actual execution,” after which he handed the attack itself to Belarusian proxy agent Andrei Karshakou. Further up the chain, at the far end of this “political leaders to pipe bombs” pipeline, sits Denis Smolyaninov, “an alleged chief planner of bomb attacks across Europe for Russia.”
A December 2025 Lithuanian intelligence report identified Smolyaninov as leading the Ukraine department of the GRU (GRU is the acronym of the department’s previous name during the Soviet period, Главное разведывательное управление—Main Intelligence Directorate). The report notes that Smolyaninov “specialised in psychological operations, and was associated with covert sabotage campaigns organized in Europe using the messaging app Telegram.”
That final sentence in their assessment is the key to understanding what many find so troubling about this new frontier of agent recruitment. Subversive groups and foreign powers no longer need to seek out “fellow travelers” (a euphemism for Communist agents/sympathizers adapted from Anatoly Lunacharsky’s term “попутчик”) at union meetings or intellectual gatherings. Now, even otherwise unassuming or even apolitical individuals can be converted into “disposable agents” with an app you can download on your phone.

Russian revolutionary and socialist writer Anatoly Vasilievich Lunacharsky (1875 - 1933) in 1917.
Some of these gig agents are still acting on ideological grounds, certainly. But others are simply doing it for the money: $5 for putting up an anti-NATO poster, $400 if you install a spy camera, and so on. Payments are made via cryptocurrency; the gig agents’ GRU handlers don’t even need to set foot outside of Moscow.
Many of these unwitting agents are just ordinary people trying to get by. They’re the underemployed, or immigrants seeking gig work that pays under the table. They grab one of these seemingly innocuous jobs just as they would a rideshare or food delivery assignment, sometimes even in the same day, with no thought to the danger—or the geopolitical implications.
Even when an assignment does involve something undeniably destructive or otherwise illegal, like burning down a warehouse, the “disposable agent” is oftentimes more inclined to conclude it’s part of some street-level gangland rivalry rather than a global conflict between powerful nations. They assume their cryptocurrency payment is being furnished by a crime boss rather than the Kremlin.
The Guardian even found a case where these gig workers were completely unaware that they were fighting against their own side. “Last May,” the paper reports, “Polish authorities arrested a Pole and two Belarusians on suspicion of planning sabotage acts for the Russians inside Poland. All three men had previously fought in Ukraine on the side of Kyiv.”
This app-based à la carte infiltration represents an unsettling new chapter in the long history of cloak-and-dagger activity, one the International Institute for Strategic Studies has dubbed the “intelligence-operative gig economy.” It’s the evolution, and maybe even the perfection, of a principle of spycraft first established centuries before the USSR was even a twinkle in Vladimir Lenin’s eye.
The blueprint, it turns out, is roughly 2,400 years old. In the Arthashastra—a Sanskrit treatise on statecraft attributed to the Brahmin Chanakya—an early chapter lays out an entire taxonomy of sancháráh, or “wandering spies.” The roles these spies perform can vary, from the satri, the classmate spies, who stir up the educated populace with provocation, to the tikshna, the firebrands, who face and deal in deadly force for money, and to the parivrajika, the woman ascetic, who can infiltrate the homes of prime ministers and high society.
“The immediate officers of the institutes of espionage shall by making use of signs or writing set their own spies in motion,” the text notes. But it cautions that, crucially, “Neither the institutes of espionage nor they (the wandering spies) shall know each other.”
The Cold War-era KGB understood this, so it relied on layers upon layers of intermediaries and “cutouts” between state officials and the operatives actually getting their hands dirty in the cloak-and-dagger field. It made their spy network much harder for their targets to untangle, and kept the Soviet government at a safe distance, with plenty of plausible deniability should a mission be exposed or have unintended consequences.
According to a report from the International Centre for Defense and Security, modern-day Russia appears to be using contemporary technology to practice the same obfuscation techniques:
“Russian handlers deliberately structure sabotage operations so executors do not know the organisers’ identities. As in organised criminal scams, they employ multiple cutouts (intermediaries), disposable mobile phones, anonymous communication channels, and cryptocurrencies, making it difficult to trace the chain of command back to senior operatives.”
The ICDS’s criminal-enterprise comparison turns out to be apt in more ways than one. Trying to unravel the purposefully obscured chain of command can call to mind the old mafia movies, with cops pinning blurry photographs to a bulletin board, linked by bits of yarn. Yet the KGB knew this kind of obscuring wasn’t just a shield—it could also be a weapon in itself.
The KGB often relied on the doctrine of “маскировка,” literally meaning masking or disguising. The idea originated during WWII, when the Soviet army deceived Axis planners by utilizing fake tank turrets and implied troop movements to create uncertainty and deplete enemy reserves. This form of deception was a component of such pivotal battles as Stalingrad, Kursk, and 1944’s Operation Bagration.
During the Cold War, the Soviet intelligence apparatus relied on маскировка as a form of psychological warfare against its ideological opponents (and, in some senses, to keep its own citizenry in line as well). For example, one might think the goal in arranging an act of arson against an enemy structure is to, in mob parlance, “make it look like an accident.” But there’s a benefit to making it look only almost like an accident. If that fire could have been KGB sabotage, then so could the next one, and the one after that. Once you’ve created that sliver of ambiguity in your espionage activity, every real accident can also be attributed to your nefarious actions by your duly paranoid opponent.
Recent reports suggest that modern Russia operates on much the same principle, and that the advent of the “disposable agent” has made the method easier to deploy than ever. Consider the drone at Leipzig/Halle. Had it detonated on the wing of that Antonov, the planning behind the attack might never have surfaced. In that case, even if investigators identified the operator, they couldn’t easily say whether he was a foreign agent or a lone wolf radicalized online. And if the people carrying out these attacks don’t even know they’re serving Moscow, who can say with confidence which act of violence, or which small act of disruption, is the work of a lone wolf—and which is the work of a disposable agent?

Beyond the mind games, the strategy carries a simpler cost for its targets: every cheap attack forces an expensive defense. It might seem strange that so many of these “disposable agents” are being deployed for one-off attacks on small scale targets. The ICDS’ report speaks of agents being recruited online for tasks like warehouse fires, truck and railway explosions, and even a vandalism campaign against a Jewish memorial in Paris “reminiscent of the KGB’s swastika campaign of 1959.” At first blush, these civilian targets might have little strategic value. But in the big picture, that’s exactly why it benefits Russia to attack them. A $5 arsonist can oblige a government to spend millions guarding everything he might burn next.
A 1948 study for the United States Army’s Center for Military History, “Rear Area Security in Russia,” highlighted a strategy deployed by the Soviet Army that differed from conventional military wisdom. This “Soviet Second Front Behind the German Lines” used Russian partisans to attack individual bridges, trains, supply depots, and other small targets deep inside German territory to force the Nazis to divert much-needed security forces away from the front. The attacks would stress Nazi supply lines and make defending occupied areas in the rear far more costly and complicated.
The KGB’s Division V, which specialized in foreign assassinations and sabotage, adopted a similar strategy during the Cold War. And now, the GRU’s unit 29155 is essentially doing the same thing. By attacking small infrastructure targets with easily deployable disposable agents, they’re forcing their opponents to defend every little potential target in their territory. That doesn’t just cost money and manpower, it also means less attention can be paid to the larger targets that need defending, weakening the entire security apparatus.
Covert warfare is evolving before our eyes in the 21st century. Cultivating a fellow traveler once took years; now an agent can be hired in minutes, unaware of who he’s fighting for, or even that he’s fighting at all. Moscow is redeploying Soviet tradecraft against people desperate enough to take the work, and the espionage gig economy it’s built threatens to destabilize far more than Ukraine. There is a flaw in the design, though. It isn’t that recruits are too skeptical to be fooled. It’s that people chasing easy money are rarely interested in doing the job well.
Consider the Belarusian woman who was convicted with her boyfriend for papering her city with anti-NATO flyers she says neither of them believed in. As The Guardian reported, “Her boyfriend, she claimed, would often put up a poster, take a photo to provide proof, and then immediately pull it down.”
So the next time you see somebody half-heartedly taking a gig from an app, cutting corners and generally phoning it in to milk as much cryptocurrency as possible for the least amount of effort, be grateful. That laziness might be helping to curb a national security threat.
Michale Natale is a News Editor for the Hearst Enthusiast Group. As a writer and researcher, he has produced written and audio-visual content for more than fifteen years, spanning historical periods from the dawn of early man to the Golden Age of Hollywood. His stories for the Enthusiast Group have involved coordinating with organizations like the National Parks Service and the Secret Service, and travelling to notable historical sites and archaeological digs, from excavations of America’ earliest colonies to the former homes of Edgar Allan Poe.